mirror of
https://github.com/sadoyan/aralez.git
synced 2026-10-23 06:01:35 +08:00
Compare commits
| Author | SHA1 | Date | |
|---|---|---|---|
 Ara Sadoyan |
0831ffb801 | ||
|
Ara Sadoyan
|
5d55e2b120 | ||
|
Ara Sadoyan
|
b3c614e592 | ||
|
Ara Sadoyan
|
b22bb2fe16 | ||
|
Ara Sadoyan
|
e6204a2b1d | ||
|
Ara Sadoyan
|
6a78acd486 | ||
|
Ara Sadoyan
|
1a2485b87a | ||
|
Ara Sadoyan
|
3329c34a09 | ||
 Serge |
6df63f69cd | ||
|
Ara Sadoyan
|
4a4f3e6187 | ||
|
Ara Sadoyan
|
31f513cc2a | ||
|
Ara Sadoyan
|
0006d27d02 | ||
|
Ara Sadoyan
|
d2d4100cba | ||
|
Ara Sadoyan
|
f575007044 | ||
|
Ara Sadoyan
|
bb43df0e4d | ||
|
Ara Sadoyan
|
29c3d6a413 | ||
|
Ara Sadoyan
|
c21374f2a2 | ||
|
Ara Sadoyan
|
51eec524ca | ||
|
Ara Sadoyan
|
97ac839001 | ||
|
Ara Sadoyan
|
b63d822577 | ||
|
Ara Sadoyan
|
600cb602e3 | ||
|
Ara Sadoyan
|
29d1f1db78 | ||
|
Ara Sadoyan
|
3ae54185ad | ||
|
Ara Sadoyan
|
430f867792 | ||
|
Ara Sadoyan
|
f6c092adc4 | ||
|
Ara Sadoyan
|
19ad8fdbf4 | ||
|
Ara Sadoyan
|
b55ff2d392 | ||
|
Ara Sadoyan
|
b73ccc527f | ||
|
Ara Sadoyan
|
c89fe48e44 | ||
|
Ara Sadoyan
|
d21fd8cb4b | ||
|
Ara Sadoyan
|
491442bb92 | ||
|
Ara Sadoyan
|
e07791e1f0 | ||
|
Ara Sadoyan
|
7b952b467c | ||
|
Ara Sadoyan
|
9a1e8fe149 | ||
|
Ara Sadoyan
|
874ce4fddb | ||
|
Ara Sadoyan
|
99c7a811da | ||
|
Ara Sadoyan
|
edadda803c | ||
|
Ara Sadoyan
|
c5d0fe60a0 | ||
|
Ara Sadoyan
|
d7fe476b24 | ||
|
Ara Sadoyan
|
aa22749393 | ||
|
Ara Sadoyan
|
4b6a558b4b | ||
|
Ara Sadoyan
|
6c9c7acf65 | ||
 Taqman-probe |
2845dc5923 | ||
|
Ara Sadoyan
|
f2e07a8d70 | ||
|
Ara Sadoyan
|
5815da6576 | ||
|
Ara Sadoyan
|
1ab0916026 | ||
|
Ara Sadoyan
|
707f725b88 | ||
|
Ara Sadoyan
|
eb4e73ece0 | ||
|
Ara Sadoyan
|
53e7dcfd33 | ||
|
Ara Sadoyan
|
f3b346a28d | ||
|
Ara Sadoyan
|
c011800e1e | ||
|
Ara Sadoyan
|
265ff6b774 | ||
|
Ara Sadoyan
|
1c3d9a263f | ||
|
Ara Sadoyan
|
162c5060c9 | ||
|
Ara Sadoyan
|
132cf45dfe | ||
|
Ara Sadoyan
|
77dcafbb4e | ||
|
Ara Sadoyan
|
649bd979f7 | ||
|
Ara Sadoyan
|
bd315106b9 | ||
|
Ara Sadoyan
|
3ba2ed33ae | ||
|
Taqman-probe
|
c09efab9fd | ||
|
Taqman-probe
|
735d605f6d | ||
|
Ara Sadoyan
|
6773d0f502 | ||
|
Ara Sadoyan
|
a8cb727da5 | ||
|
Ara Sadoyan
|
f81194aee7 | ||
|
Ara Sadoyan
|
0f09a2e02b | ||
|
Ara Sadoyan
|
27aca0a3a5 | ||
|
Ara Sadoyan
|
3c99ed0c44 | ||
|
Ara Sadoyan
|
4a6e1d817b | ||
|
Ara Sadoyan
|
f6a2df44d0 | ||
|
Ara Sadoyan
|
e8d976f5f1 | ||
|
Ara Sadoyan
|
a1341e90f7 | ||
|
Ara Sadoyan
|
ddcacc509c | ||
|
Ara Sadoyan
|
2b385cc630 | ||
|
Ara Sadoyan
|
1b5223986d | ||
|
Ara Sadoyan
|
ac2bd8113d | ||
|
Ara Sadoyan
|
4d9a2ecfe3 | ||
|
Taqman-probe
|
aa70d818b2 | ||
|
Ara Sadoyan
|
15d356f087 | ||
|
Ara Sadoyan
|
b17962e6d5 | ||
|
Ara Sadoyan
|
ea779182f2 | ||
|
Ara Sadoyan
|
9339a142a6 | ||
|
Ara Sadoyan
|
cfc9bd319d | ||
|
Ara Sadoyan
|
a5ced59e5c | ||
|
Ara Sadoyan
|
c3df7bc131 | ||
|
Ara Sadoyan
|
0248d73836 | ||
|
Ara Sadoyan
|
96a5aef7d0 | ||
|
Ara Sadoyan
|
5c3b72b7a3 | ||
|
Ara Sadoyan
|
3cf0fc493f | ||
|
Ara Sadoyan
|
207ee481fb | ||
|
Ara Sadoyan
|
1c2f7327aa | ||
|
Ara Sadoyan
|
310a554a25 | ||
|
Ara Sadoyan
|
69a5167346 | ||
|
Ara Sadoyan
|
4734ccab2f | ||
|
Taqman-probe
|
61d65f6e4e | ||
|
Taqman-probe
|
20ac39067d | ||
|
Taqman-probe
|
7afa76de8f | ||
|
Ara Sadoyan
|
e29161965f | ||
 Zsombor Gegesy |
9216710dda |
@@ -0,0 +1,9 @@
|
||||
helm-extra-args: --timeout 300s
|
||||
check-version-increment: true
|
||||
debug: true
|
||||
chart-dirs:
|
||||
- charts
|
||||
validate-maintainers: true
|
||||
namespace: default
|
||||
release-label: test
|
||||
target-branch: main
|
||||
@@ -0,0 +1,23 @@
|
||||
---
|
||||
# See https://docs.github.com/en/github/administering-a-repository/configuration-options-for-dependency-updates
|
||||
|
||||
version: 2
|
||||
updates:
|
||||
- package-ecosystem: "github-actions"
|
||||
directory: "/"
|
||||
commit-message:
|
||||
prefix: "chore:"
|
||||
open-pull-requests-limit: 8
|
||||
rebase-strategy: disabled
|
||||
schedule:
|
||||
interval: "monthly"
|
||||
day: "monday"
|
||||
time: "10:00"
|
||||
timezone: "UTC"
|
||||
cooldown:
|
||||
default-days: 7
|
||||
groups:
|
||||
actions:
|
||||
patterns:
|
||||
- "actions/*"
|
||||
- "helm/*"
|
||||
@@ -0,0 +1,28 @@
|
||||
name: Helm chart check
|
||||
|
||||
on:
|
||||
pull_request:
|
||||
branches:
|
||||
- main
|
||||
paths:
|
||||
- "charts/**"
|
||||
|
||||
jobs:
|
||||
helm-lint:
|
||||
name: Helm chart check
|
||||
timeout-minutes: 5
|
||||
runs-on: ubuntu-latest
|
||||
steps:
|
||||
- name: Checkout
|
||||
uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
|
||||
with:
|
||||
persist-credentials: false
|
||||
|
||||
- name: Install chart-testing tools
|
||||
id: lint
|
||||
uses: helm/chart-testing-action@6ec842c01de15ebb84c8627d2744a0c2f2755c9f # v2.8.0
|
||||
|
||||
- name: Run helm chart linter
|
||||
run: ct --config .github/ct.yml lint
|
||||
- name: Run helm template
|
||||
run: helm lint charts/aralez
|
||||
+4
-2
@@ -5,12 +5,13 @@
|
||||
*.dll
|
||||
*.exe
|
||||
*.sh
|
||||
/docs/
|
||||
*.yaml
|
||||
/docs
|
||||
assets/
|
||||
assets
|
||||
/target/
|
||||
*.iml
|
||||
.idea/
|
||||
.etc/
|
||||
*.ipr
|
||||
*.iws
|
||||
/out/
|
||||
@@ -21,4 +22,5 @@ crashlytics.properties
|
||||
crashlytics-build.properties
|
||||
/target
|
||||
/z_shpo
|
||||
/configs
|
||||
Makefile
|
||||
|
||||
Generated
+1092
-1183
File diff suppressed because it is too large
Load Diff
+40
-25
@@ -1,7 +1,11 @@
|
||||
[package]
|
||||
name = "aralez"
|
||||
version = "0.9.2"
|
||||
version = "0.93.4"
|
||||
edition = "2021"
|
||||
license = "Apache-2.0"
|
||||
description = "Reverse proxy built on top of Cloudflare's Pingora"
|
||||
exclude = ["configs/*"]
|
||||
repository = "https://github.com/sadoyan/aralez"
|
||||
|
||||
[profile.release]
|
||||
opt-level = 3
|
||||
@@ -11,40 +15,51 @@ panic = "abort"
|
||||
strip = true
|
||||
|
||||
[dependencies]
|
||||
tokio = { version = "1.52.3", features = ["full"] }
|
||||
pingora = { version = "0.8.0", features = ["lb", "openssl"] } # openssl, rustls, boringssl
|
||||
serde = { version = "1.0.228", features = ["derive"] }
|
||||
tokio = { version = "1.53.1", features = ["full"] }
|
||||
pingora = { version = "0.8.1", features = ["lb", "openssl"] } # openssl, rustls, boringssl
|
||||
pingora-core = "0.8.1"
|
||||
pingora-proxy = "0.8.1"
|
||||
pingora-http = "0.8.1"
|
||||
pingora-limits = "0.8.1"
|
||||
pingora-cache = "0.8.1"
|
||||
dashmap = "7.0.0-rc2"
|
||||
pingora-core = "0.8.0"
|
||||
pingora-proxy = "0.8.0"
|
||||
pingora-http = "0.8.0"
|
||||
pingora-limits = "0.8.0"
|
||||
async-trait = "0.1.89"
|
||||
log = "0.4.29"
|
||||
futures = "0.3.32"
|
||||
async-trait = "0.1.92"
|
||||
log = "0.4.34"
|
||||
notify = "9.0.0-rc.4"
|
||||
axum = { version = "0.8.9" }
|
||||
reqwest = { version = "0.13.3", features = ["json", "stream", "blocking"] }
|
||||
serde_yml = "0.0.12"
|
||||
rand = "0.10.1"
|
||||
base64 = "0.22.1"
|
||||
jsonwebtoken = { version = "10.4.0", default-features = false, features = ["use_pem", "rust_crypto"] }
|
||||
tonic = "0.14.6"
|
||||
serde = { version = "1.0.229", features = ["derive"] }
|
||||
noyalib = { version = "0.0.32", features = ["compat-serde-yaml"] }
|
||||
rand = "0.10.2"
|
||||
base64 = "0.23.1"
|
||||
jsonwebtoken = { version = "11.0.0", default-features = false, features = ["use_pem", "rust_crypto"] }
|
||||
sha2 = { version = "0.11.0-rc.5", default-features = false }
|
||||
base16ct = { version = "1.0.0", features = ["alloc"] }
|
||||
urlencoding = "2.1.3"
|
||||
arc-swap = "1.9.1"
|
||||
mimalloc = { version = "0.1.50", default-features = false }
|
||||
arc-swap = "1.9.2"
|
||||
prometheus = "0.14.0"
|
||||
x509-parser = "0.18.1"
|
||||
rustls-pemfile = "2.2.0"
|
||||
tower-http = { version = "0.6.10", features = ["fs"] }
|
||||
tower-http = { version = "0.7.1", features = ["fs"] }
|
||||
privdrop = "0.5.6"
|
||||
ctrlc = "3.5.2"
|
||||
serde_json = "1.0.149"
|
||||
serde_json = "1.0.151"
|
||||
subtle = "2.6.1"
|
||||
moka = { version = "0.12.15", features = ["sync"] }
|
||||
moka = { version = "0.12.16", features = ["sync"] }
|
||||
ahash = "0.8.12"
|
||||
instant-acme = "0.8.5"
|
||||
rcgen = "0.14.7"
|
||||
log4rs = "1.4.0"
|
||||
rcgen = "0.14.10"
|
||||
log4rs = { version = "1.4.0", features = ["rolling_file_appender", "compound_policy", "size_trigger", "fixed_window_roller", "gzip"] }
|
||||
mimalloc = { version = "0.1.52", default-features = false }
|
||||
signal-hook = "0.4.4"
|
||||
sd-notify = "0.5.0"
|
||||
libc = "0.2.186"
|
||||
tokio-native-tls = "0.3.1"
|
||||
hyper = "1.11.1"
|
||||
hyper-util = "0.1.20"
|
||||
http-body-util = "0.1.5"
|
||||
bytes = "1.12.1"
|
||||
|
||||
rustls = { version = "0.23", default-features = false, features = ["ring"] }
|
||||
kube = { version = "4.2.0", features = ["runtime", "client", "derive"] }
|
||||
k8s-openapi = { version = "0.28.0", features = ["v1_32"] }
|
||||
futures = "0.3.34"
|
||||
lazy_static = "1.5.0"
|
||||
|
||||
-13
@@ -1,13 +0,0 @@
|
||||
FROM debian:trixie-slim
|
||||
|
||||
RUN apt-get update && apt-get install -y ca-certificates curl net-tools iputils-ping
|
||||
RUN apt-get clean && rm -rf /var/lib/apt/lists/*
|
||||
|
||||
COPY aralez /usr/local/bin/aralez
|
||||
|
||||
RUN chmod +x /usr/local/bin/aralez
|
||||
RUN mkdir -p /etc/aralez/certs/upstreams
|
||||
|
||||
WORKDIR /etc/aralez
|
||||
|
||||
ENTRYPOINT ["/usr/local/bin/aralez", "-c", "/etc/aralez/main.yaml"]
|
||||
@@ -6,16 +6,25 @@
|
||||
|
||||
### **Reverse proxy built on top of Cloudflare's Pingora**
|
||||
|
||||
Aralez is a high-performance Rust reverse proxy with zero-configuration automatic protocol handling, TLS, and upstream management,
|
||||
featuring Consul and Kubernetes integration for dynamic pod discovery and health-checked routing, acting as a lightweight ingress-style proxy.
|
||||
Aralez is a high-performance Rust reverse proxy with zero-configuration automatic protocol handling, TLS, and upstream management, featuring Consul and Kubernetes integration for dynamic pod discovery and health-checked routing, acting as a
|
||||
lightweight ingress-style proxy.
|
||||
|
||||
|
||||
---
|
||||
What Aralez means ?
|
||||
**Aralez = Արալեզ** <ins>Named after the legendary Armenian guardian spirit, winged dog-like creature, that descend upon fallen heroes to lick their wounds and resurrect them</ins>.
|
||||
What Aralez means ? **Aralez = Արալեզ** <ins>Named after the legendary Armenian guardian spirit, winged dog-like creature, that descend upon fallen heroes to lick their wounds and resurrect them</ins>.
|
||||
|
||||
Built on Rust, on top of **Cloudflare’s Pingora engine**, **Aralez** delivers world-class performance, security and scalability — right out of the box.
|
||||
|
||||
[](https://www.buymeacoffee.com/sadoyan)
|
||||
---
|
||||
|
||||
## Links
|
||||
|
||||
- [**Documentation**](https://aralez.rs) : The manual you should read
|
||||
- [**Downloads**](https://github.com/sadoyan/aralez/releases) : Binary downloads
|
||||
- [**Issues**](https://github.com/sadoyan/aralez/issues) : Issues and requests
|
||||
- [**Crates**](https://crates.io/crates/aralez) : The Rust crate registry
|
||||
- [**DockerHUB**](https://hub.docker.com/r/sadoyan/aralez) : DockerHUB official repository
|
||||
- [**GitHUB Packages**](https://github.com/sadoyan/aralez/pkgs/container/aralez) : GitHUB ghcr.io images
|
||||
|
||||
---
|
||||
|
||||
@@ -26,6 +35,7 @@ Built on Rust, on top of **Cloudflare’s Pingora engine**, **Aralez** delivers
|
||||
- **Let’s Encrypt Certificates** — Ordering and renewal of SSL/TLS certificates via the HTTP-01 challenge.
|
||||
- **Upstreams TLS detection** — Aralez will automatically detect if upstreams uses secure connection.
|
||||
- **Built in rate limiter** — Globar or route limit requests to upstreams.
|
||||
- **Caching Proxy** — In memory cache with configurable TTL, without external dependencies.
|
||||
- **Authentication** — Supports Basic Auth, API tokens, and JWT verification.
|
||||
- **Basic Auth**
|
||||
- **API Key** via `x-api-key` header
|
||||
@@ -50,38 +60,36 @@ Built on Rust, on top of **Cloudflare’s Pingora engine**, **Aralez** delivers
|
||||
|
||||
### `main.yaml`
|
||||
|
||||
| Key | Example Value | Description |
|
||||
|----------------------------------|--------------------------|----------------------------------------------------------------------------------------------------|
|
||||
| **threads** | 12 | Number of running daemon threads. Optional, defaults to 1 |
|
||||
| **runuser** | aralez | Optional, Username for running aralez after dropping root privileges, requires to launch as root |
|
||||
| **rungroup** | aralez | Optional,Group for running aralez after dropping root privileges, requires to launch as root |
|
||||
| **daemon** | false | Run in background (boolean) |
|
||||
| **upstream_keepalive_pool_size** | 500 | Pool size for upstream keepalive connections |
|
||||
| **pid_file** | /tmp/aralez.pid | Path to PID file |
|
||||
| **error_log** | /tmp/aralez_err.log | Path to error log file |
|
||||
| **upgrade_sock** | /tmp/aralez.sock | Path to live upgrade socket file |
|
||||
| **config_address** | 0.0.0.0:3000 | HTTP API address for pushing upstreams.yaml from remote location |
|
||||
| **proxy_tls_grade** | (high, medium, unsafe) | Grade of TLS ciphers, for easy configuration. High matches Qualys SSL Labs A+ (defaults to medium) |
|
||||
| **config_tls_key_file** | etc/key.pem | Private Key file path. Mandatory if proxy_address_tls is set, else optional |
|
||||
| **proxy_address_http** | 0.0.0.0:6193 | Aralez HTTP bind address |
|
||||
| **proxy_address_tls** | 0.0.0.0:6194 | Aralez HTTPS bind address (Optional) |
|
||||
| **proxy_configs** | etc/ | The top directory of config files |
|
||||
| **upstreams_conf** | etc/upstreams.yaml | The location of upstreams file |
|
||||
| **log_level** | info | Log level , possible values : info, warn, error, debug, trace, off |
|
||||
| **log_file** | /full/path/to/aralez.log | Optional, the location of log file. If thi entry does not exist logs will be emitted to stdout. |
|
||||
| **hc_method** | HEAD | Healthcheck method (HEAD, GET, POST are supported) UPPERCASE |
|
||||
| **hc_interval** | 2 | Interval for health checks in seconds |
|
||||
| **master_key** | Random long string | Master key for working with API server and JWT Secret generation |
|
||||
| **file_server_folder** | /some/local/folder | Optional, local folder to serve |
|
||||
| **file_server_address** | 127.0.0.1:3002 | Optional, Local address for file server. Can set as upstream for public access |
|
||||
| **config_api_enabled** | true | Boolean to enable/disable remote config push capability |
|
||||
| Key | Example Value | Description |
|
||||
|----------------------------------|----------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------|
|
||||
| **threads** | 12 | Number of running daemon threads. Optional, defaults to 1 |
|
||||
| **runuser** | aralez | Optional. Username for running aralez after dropping root privileges (requires launch as root) |
|
||||
| **rungroup** | aralez | Optional. Group for running aralez after dropping root privileges (requires launch as root) |
|
||||
| **daemon** | false | Run in background (boolean) |
|
||||
| **upstream_keepalive_pool_size** | 500 | Pool size for upstream keepalive connections |
|
||||
| **pid_file** | /tmp/aralez.pid | Path to PID file |
|
||||
| **config_address** | 0.0.0.0:3000 | HTTP API address for pushing upstreams.yaml from remote location |
|
||||
| **proxy_tls_grade** | high, medium, unsafe | Grade of TLS ciphers. `high` matches Qualys SSL Labs A+ (defaults to `medium`) |
|
||||
| **proxy_address_http** | 0.0.0.0:6193 | Aralez HTTP bind address |
|
||||
| **proxy_address_tls** | 0.0.0.0:6194 | Aralez HTTPS bind address (Optional) |
|
||||
| **proxy_configs** | /etc/aralez/ | Direcotry containing configuration files, must be writeable by user `aralez` |
|
||||
| **upstreams_conf** | /etc/aralez/upstreams.yaml | Location of the upstreams file |
|
||||
| **access_log** | access | Configure access logging. Values: `access, error` |
|
||||
| **log_level** | info | Log level: `info`, `warn`, `error`, `debug`, `trace`, `off` |
|
||||
| **log_file** | /tmp/aralez.log, 20, 5, compress | Optional, the location of log file, file size in megabytes, number of log files to keep, compress files .valueas are separated by comma. Defaults to None, 100, 5, No |
|
||||
| **hc_method** | HEAD | Healthcheck method: HEAD, GET, POST (UPPERCASE) |
|
||||
| **hc_interval** | 2 | Interval for health checks in seconds |
|
||||
| **file_server_folder** | /some/local/folder | Optional. Local folder to serve |
|
||||
| **file_server_address** | 127.0.0.1:3002 | Optional. Local address for file server |
|
||||
| **config_api_enabled** | true | Enable/disable remote config push capability |
|
||||
| **cache_size_mb** | 50 | Optional. Enable internal cache with size in megabytes of value. Cache is entirely disabled when this line is commented out. |
|
||||
| **cache_ttl** | 10 | Optional. Set Default TTL in seconds for cached items, works if cache control headers are not set via upstream. Defaults to 60 if cache_size_mb is set. |
|
||||
|
||||
---
|
||||
|
||||
## Installation
|
||||
|
||||
Download the prebuilt binary for your architecture from releases section of [GitHub](https://github.com/sadoyan/aralez/releases) repo
|
||||
Make the binary executable `chmod 755 ./aralez-VERSION` and run.
|
||||
Download the prebuilt binary for your architecture from releases section of [GitHub](https://github.com/sadoyan/aralez/releases) repo Make the binary executable `chmod 755 ./aralez-VERSION` and run.
|
||||
|
||||
File names:
|
||||
|
||||
@@ -99,8 +107,7 @@ File names:
|
||||
|
||||
**glibc** builds are in general faster, but have few, basic, Glibc dependencies:
|
||||
|
||||
**musl** builds are 100% portable, static compiled binaries and have zero system dependencies.
|
||||
In general musl builds have a little less performance.
|
||||
**musl** builds are 100% portable, static compiled binaries and have zero system dependencies. In general musl builds have a little less performance.
|
||||
|
||||
The most intensive tests shows 107k-110k requests per second on **Glibc** binaries against 97k-100k **Musl** ones.
|
||||
|
||||
@@ -111,6 +118,27 @@ For getting the best performance on newer hardware use `aralez-x86_64-*.gz`.
|
||||
|
||||
```shell
|
||||
docker run -d -v /path/to/config:/etc/aralez:rw -p 80:80 -p 443:443 sadoyan/aralez
|
||||
docker run -d -v /path/to/config:/etc/aralez:rw -p 80:80 -p 443:443 sadoyan/aralez:compat
|
||||
docker run -d -v /path/to/config:/etc/aralez:rw -p 80:80 -p 443:443 ghcr.io/sadoyan/aralez:latest
|
||||
docker run -d -v /path/to/config:/etc/aralez:rw -p 80:80 -p 443:443 ghcr.io/sadoyan/aralez:compat
|
||||
```
|
||||
|
||||
**Dockerfile :**
|
||||
|
||||
```dockerfile
|
||||
FROM debian:trixie-slim
|
||||
|
||||
RUN apt-get update && apt-get install -y ca-certificates curl net-tools iputils-ping
|
||||
RUN apt-get clean && rm -rf /var/lib/apt/lists/*
|
||||
|
||||
COPY aralez /usr/local/bin/aralez
|
||||
|
||||
RUN chmod +x /usr/local/bin/aralez
|
||||
RUN mkdir -p /etc/aralez/certs/upstreams
|
||||
|
||||
WORKDIR /etc/aralez
|
||||
|
||||
ENTRYPOINT ["/usr/local/bin/aralez", "-c", "/etc/aralez/main.yaml"]
|
||||
```
|
||||
|
||||
## Running the Proxy
|
||||
@@ -121,7 +149,7 @@ docker run -d -v /path/to/config:/etc/aralez:rw -p 80:80 -p 443:443 sadoyan/aral
|
||||
|
||||
## Systemd integration
|
||||
|
||||
Assuming Arales in installed in `/opt/aralez` folder
|
||||
Assuming Aralez in installed in `/opt/aralez` folder
|
||||
|
||||
```bash
|
||||
cat > /etc/systemd/system/aralez.service <<EOF
|
||||
@@ -209,7 +237,7 @@ DEFAULT:
|
||||
|
||||
**This means:**
|
||||
|
||||
- Sticky sessions are enabled globally. This setting applies to all upstreams. If enabled the value withh be set for `Max-Age=` cookie.
|
||||
- Sticky sessions are enabled globally. This setting applies to all upstreams. If enabled the value will be set for `Max-Age=` cookie.
|
||||
- HTTP to HTTPS redirect disabled globally, but can be overridden by `to_https` setting per upstream.
|
||||
- All upstreams will receive custom headers : `X-Forwarded-Proto:https` and `X-Forwarded-Port:443`
|
||||
- Additionally, myhost.mydomain.com with path `/` will receive custom headers : `X-Another-Header:Hohohohoho` and `X-Something-Else:Foobar`
|
||||
@@ -251,17 +279,25 @@ DEFAULT:
|
||||
To enable TLS for the proxy server.
|
||||
|
||||
- Set `proxy_address_tls` in `main.yaml`
|
||||
- Provide at least on `tls_certificate/tls_key_file` pair.
|
||||
- Provide at least one `tls_certificate/tls_key_file` pair.
|
||||
- First pair is required to create the TLS listener.
|
||||
- This pair can be anything, even self-signed with dummy domain.
|
||||
- After getting normal certificate it can be deleted
|
||||
|
||||
```shell
|
||||
mkdir -p /etc/aralez/certificates
|
||||
chown -R aralez:aralez /etc/aralez
|
||||
cd /etc/aralez/certificates
|
||||
openssl req -x509 -newkey rsa:4096 \
|
||||
-keyout dummy.key -out dummy.crt -sha256 -days 3650 -nodes \
|
||||
-subj "/C=XX/ST=StateName/L=CityName/O=CompanyName/OU=CompanySectionName/CN=CommonNameOrHostname"
|
||||
```
|
||||
|
||||
---
|
||||
|
||||
## Remote Config API
|
||||
|
||||
Push new `upstreams.yaml` over HTTP to `config_address` (`:3000` by default). Useful for CI/CD automation or remote config updates.
|
||||
URL parameter. `key=MASTERKEY` is required. `MASTERKEY` is the value of `master_key` in the `main.yaml`
|
||||
Push new `upstreams.yaml` over HTTP to `config_address` (`:3000` by default). Useful for CI/CD automation or remote config updates. URL parameter. `key=MASTERKEY` is required. `MASTERKEY` is the value of `master_key` in the `main.yaml`
|
||||
|
||||
```bash
|
||||
curl -XPOST --data-binary @./etc/upstreams.txt 127.0.0.1:3000/conf?key=${MASTERKEY}
|
||||
@@ -342,22 +378,22 @@ curl -u username:password -H 'Host: myip.mydomain.com' http://127.0.0.1:6193/
|
||||
|
||||
| Feature / Proxy | **Aralez** | **Nginx** | **HAProxy** | **Traefik** | **Caddy** | **Envoy** |
|
||||
|--------------------|:----------:|:-----------:|:-----------:|:-----------:|:----------:|:---------:|
|
||||
| **Reload** | ✅ Hot | ⚙️ Manual | ⚙️ Manual | ✅ Hot | ✅ Hot | ✅ Hot |
|
||||
| **Cert load** | ✅ Hot | ❌ Reload | ❌ Reload | ✅ Yes | ✅ Yes | ⚙️ No ? |
|
||||
| **Authentication** | ✅ Yes | ⚙️ Limited | ⚙️ Limited | ✅ Yes | ✅ Yes | ✅ Yes |
|
||||
| **HTTP2** | ✅ Yes | ⚙️ Manual | ⚙️ Manual | ✅ Yes | ✅ Yes | ✅ Yes |
|
||||
| **TLS Grades** | ✅ Yes | ⚙️ Manual | ⚙️ Manual | ⚙️ Manual | ✅ Yes | ⚙️ Manual |
|
||||
| **gRPC** | ✅ Auto | ⚙️ Manual | ⚙️ Manual | ⚙️ Manual | ⚙️ Manual | ⚙️ Manual |
|
||||
| **SSL Proxy** | ✅ Auto | ⚙️ Manual | ⚙️ Manual | ✅ Yes | ✅ Yes | ✅ Yes |
|
||||
| **HTTP/2** | ✅ Auto | ⚙️ Manual | ⚙️ Manual | ✅ Yes | ✅ Yes | ✅ Yes |
|
||||
| **WebSocket** | ✅ Auto | ⚙️ Manual | ⚙️ Manual | ✅ Yes | ✅ Yes | ✅ Yes |
|
||||
| **Sticky Session** | ✅ Yes | ❌ No | ⚙️ Yes | ✅ Yes | ⚙️ Limited | ✅ Manual |
|
||||
| **Prometheus** | ✅ Yes | ⚙️ External | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes |
|
||||
| **Consul** | ✅ Yes | ❌ No | ⚙️DNS API | ✅ Yes | ❌ No | ✅ Yes |
|
||||
| **Kubernetes** | ✅ Yes | ⚙️ Ingress | ⚙️ External | ✅ Yes | ⚙️ Limited | ✅ Yes |
|
||||
| **Limiter** | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes |
|
||||
| **Static Files** | ✅ Yes | ✅ Yes | ⚙️ Lua ? | ✅ Yes | ✅ Yes | ❌ No |
|
||||
| **Health Checks** | ✅ Yes | ⚙️ Manual | ⚙️ Manual | ✅ Yes | ✅ Yes | ✅ Yes |
|
||||
| **Built With** | Rust | C | C | Go | Go | C++ |
|
||||
|
||||
---
|
||||
@@ -404,7 +440,7 @@ curl -u username:password -H 'Host: myip.mydomain.com' http://127.0.0.1:6193/
|
||||
|
||||
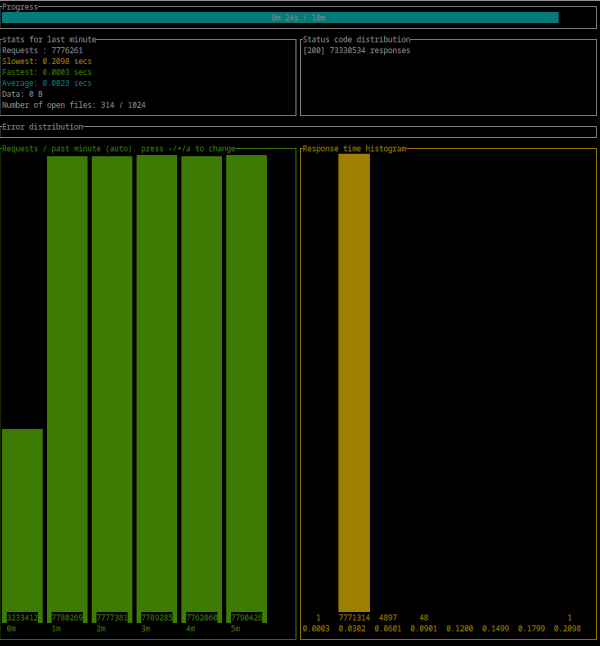
## Results reflect synthetic performance under optimal conditions.
|
||||
|
||||
- CPU : Intel(R) Xeon(R) CPU E3-1270 v6 @ 3.80GHz
|
||||
- CPU : Intel (R) Xeon (R) CPU E3-1270 v6 @ 3.80GHz
|
||||
- 300 : simultaneous connections
|
||||
- Duration : 10 Minutes
|
||||
- Binary : aralez-x86_64-glibc
|
||||
@@ -460,7 +496,7 @@ Error distribution:
|
||||
|
||||
|
||||
|
||||
- CPU : Intel(R) Xeon(R) CPU E3-1270 v6 @ 3.80GHz
|
||||
- CPU : Intel (R) Xeon (R) CPU E3-1270 v6 @ 3.80GHz
|
||||
- 300 : simultaneous connections
|
||||
- Duration : 10 Minutes
|
||||
- Binary : aralez-x86_64-musl
|
||||
@@ -518,7 +554,7 @@ Error distribution:
|
||||
|
||||
## Aralez, Nginx, Traefik performance benchmark
|
||||
|
||||
This benchmark is done on 4 servers. With CPU Intel(R) Xeon(R) E-2174G CPU @ 3.80GHz, 64 GB RAM.
|
||||
This benchmark is done on 4 servers. With CPU Intel (R) Xeon (R) E-2174G CPU @ 3.80GHz, 64 GB RAM.
|
||||
|
||||
1. Sever runs Aralez, Traefik, Nginx on different ports. Tuned as much as I could .
|
||||
2. 3x Upstreams servers, running Nginx. Replying with dummy json hardcoded in config file for max performance.
|
||||
@@ -531,10 +567,3 @@ The results show requests per second performed by Load balancer. You can see 3 b
|
||||
1. Requests via http1.1 to plain text endpoint.
|
||||
2. Requests to via http2 to SSL endpoint.
|
||||
3. Mixed workload with plain http1.1 and htt2 SSL.
|
||||
|
||||
## Links
|
||||
|
||||
- [**Documentation**](https://aralez.rs) : The manual you should read
|
||||
- [**Downloads**](https://github.com/sadoyan/aralez/releases) : Binary downloads
|
||||
- [**Issues**](https://github.com/sadoyan/aralez/issues) : Issues and requests
|
||||
|
||||
|
||||
@@ -0,0 +1,23 @@
|
||||
# Patterns to ignore when building packages.
|
||||
# This supports shell glob matching, relative path matching, and
|
||||
# negation (prefixed with !). Only one pattern per line.
|
||||
.DS_Store
|
||||
# Common VCS dirs
|
||||
.git/
|
||||
.gitignore
|
||||
.bzr/
|
||||
.bzrignore
|
||||
.hg/
|
||||
.hgignore
|
||||
.svn/
|
||||
# Common backup files
|
||||
*.swp
|
||||
*.bak
|
||||
*.tmp
|
||||
*.orig
|
||||
*~
|
||||
# Various IDEs
|
||||
.project
|
||||
.idea/
|
||||
*.tmproj
|
||||
.vscode/
|
||||
@@ -0,0 +1,18 @@
|
||||
# yaml-language-server: $schema=https://json.schemastore.org/chart.json
|
||||
apiVersion: v2
|
||||
name: aralez
|
||||
description: Ingress controller for Kubernetes
|
||||
type: application
|
||||
home: https://github.com/sadoyan/aralez/charts
|
||||
sources:
|
||||
- https://github.com/sadoyan/helm-charts/tree/main/charts/aralez
|
||||
keywords:
|
||||
- ingress-controller
|
||||
- aralez
|
||||
maintainers: []
|
||||
#
|
||||
# Versions are expected to follow Semantic Versioning (https://semver.org/)
|
||||
version: 0.0.1
|
||||
#
|
||||
# renovate: datasource=docker depName=ghcr.io/sadoyan/aralez
|
||||
appVersion: 0.93.3
|
||||
@@ -0,0 +1,17 @@
|
||||
{{ template "chart.header" . }}
|
||||
|
||||
{{ template "chart.deprecationWarning" . }}
|
||||
|
||||
{{ template "chart.badgesSection" . }}
|
||||
|
||||
{{ template "chart.description" . }}
|
||||
|
||||
{{ template "chart.homepageLine" . }}
|
||||
|
||||
{{ template "chart.maintainersSection" . }}
|
||||
|
||||
{{ template "chart.sourcesSection" . }}
|
||||
|
||||
{{ template "chart.requirementsSection" . }}
|
||||
|
||||
{{ template "chart.valuesSection" . }}
|
||||
@@ -0,0 +1,18 @@
|
||||
ingressClass: aralez
|
||||
ingressClassResource:
|
||||
enabled: true
|
||||
|
||||
# hostNetwork: true
|
||||
# hostPort:
|
||||
# ports:
|
||||
# http: 8080
|
||||
# https: 8443
|
||||
|
||||
priorityClassName: system-cluster-critical
|
||||
|
||||
env: []
|
||||
|
||||
args: []
|
||||
|
||||
useDaemonSet: true
|
||||
terminationGracePeriodSeconds: 120
|
||||
@@ -0,0 +1,104 @@
|
||||
{{/*
|
||||
Expand the name of the chart.
|
||||
*/}}
|
||||
{{- define "aralez.name" -}}
|
||||
{{- default .Chart.Name .Values.nameOverride | trunc 63 | trimSuffix "-" }}
|
||||
{{- end }}
|
||||
|
||||
{{/*
|
||||
Create a default fully qualified app name.
|
||||
We truncate at 63 chars because some Kubernetes name fields are limited to this (by the DNS naming spec).
|
||||
If release name contains chart name it will be used as a full name.
|
||||
*/}}
|
||||
{{- define "aralez.fullname" -}}
|
||||
{{- if .Values.fullnameOverride }}
|
||||
{{- .Values.fullnameOverride | trunc 63 | trimSuffix "-" }}
|
||||
{{- else }}
|
||||
{{- $name := default .Chart.Name .Values.nameOverride }}
|
||||
{{- if contains $name .Release.Name }}
|
||||
{{- .Release.Name | trunc 63 | trimSuffix "-" }}
|
||||
{{- else }}
|
||||
{{- printf "%s-%s" .Release.Name $name | trunc 63 | trimSuffix "-" }}
|
||||
{{- end }}
|
||||
{{- end }}
|
||||
{{- end }}
|
||||
|
||||
{{/*
|
||||
Create chart name and version as used by the chart label.
|
||||
*/}}
|
||||
{{- define "aralez.chart" -}}
|
||||
{{- printf "%s-%s" .Chart.Name .Chart.Version | replace "+" "_" | trunc 63 | trimSuffix "-" }}
|
||||
{{- end }}
|
||||
|
||||
{{/*
|
||||
Common labels
|
||||
*/}}
|
||||
{{- define "aralez.labels" -}}
|
||||
helm.sh/chart: {{ include "aralez.chart" . }}
|
||||
{{ include "aralez.selectorLabels" . }}
|
||||
{{- if .Chart.AppVersion }}
|
||||
app.kubernetes.io/version: {{ .Chart.AppVersion | quote }}
|
||||
{{- end }}
|
||||
app.kubernetes.io/managed-by: {{ .Release.Service }}
|
||||
{{- with .Values.podLabels }}
|
||||
{{ toYaml . }}
|
||||
{{- end }}
|
||||
{{- end }}
|
||||
|
||||
{{/*
|
||||
Selector labels
|
||||
*/}}
|
||||
{{- define "aralez.selectorLabels" -}}
|
||||
app.kubernetes.io/name: {{ include "aralez.name" . }}
|
||||
app.kubernetes.io/instance: {{ .Release.Name }}
|
||||
{{- end }}
|
||||
|
||||
{{/*
|
||||
Return a podAffinity/podAntiAffinity definition
|
||||
*/}}
|
||||
{{- define "affinities.pods" -}}
|
||||
{{- if eq .Values.podAntiAffinityPreset "soft" }}
|
||||
{{- include "affinities.pods.soft" . -}}
|
||||
{{- else if eq .Values.podAntiAffinityPreset "hard" }}
|
||||
{{- include "affinities.pods.hard" . -}}
|
||||
{{- end -}}
|
||||
{{- end -}}
|
||||
|
||||
{{/*
|
||||
Return a soft podAntiAffinity definition
|
||||
*/}}
|
||||
{{- define "affinities.pods.soft" -}}
|
||||
podAntiAffinity:
|
||||
preferredDuringSchedulingIgnoredDuringExecution:
|
||||
- podAffinityTerm:
|
||||
labelSelector:
|
||||
matchLabels: {{- (include "aralez.selectorLabels" .) | nindent 12 }}
|
||||
namespaces:
|
||||
- {{ .Release.Namespace | quote }}
|
||||
topologyKey: kubernetes.io/hostname
|
||||
weight: 1
|
||||
{{- end -}}
|
||||
|
||||
{{/*
|
||||
Return a hard podAntiAffinity definition
|
||||
*/}}
|
||||
{{- define "affinities.pods.hard" -}}
|
||||
podAntiAffinity:
|
||||
requiredDuringSchedulingIgnoredDuringExecution:
|
||||
- labelSelector:
|
||||
matchLabels: {{- (include "aralez.selectorLabels" .) | nindent 10 }}
|
||||
namespaces:
|
||||
- {{ .Release.Namespace | quote }}
|
||||
topologyKey: kubernetes.io/hostname
|
||||
{{- end -}}
|
||||
|
||||
{{/*
|
||||
Create the name of the service account to use
|
||||
*/}}
|
||||
{{- define "aralez.serviceAccountName" -}}
|
||||
{{- if .Values.serviceAccount.create }}
|
||||
{{- default (include "aralez.fullname" .) .Values.serviceAccount.name }}
|
||||
{{- else }}
|
||||
{{- default "default" .Values.serviceAccount.name }}
|
||||
{{- end }}
|
||||
{{- end }}
|
||||
@@ -0,0 +1,21 @@
|
||||
{{- $ca := genCA .Chart.Name 3650 }}
|
||||
{{- $server := genSignedCert "server" (list "127.0.0.1") nil 3650 $ca }}
|
||||
apiVersion: v1
|
||||
kind: Secret
|
||||
metadata:
|
||||
name: {{ include "aralez.fullname" . }}-tls
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
type: kubernetes.io/tls
|
||||
data:
|
||||
{{- $secretName := printf "%s-tls" (include "aralez.fullname" .) }}
|
||||
{{- $secretData := (lookup "v1" "Secret" .Release.Namespace $secretName).data }}
|
||||
{{- if and $secretData (hasKey $secretData "ca.crt") }}
|
||||
ca.crt: {{ get $secretData "ca.crt" }}
|
||||
tls.crt: {{ get $secretData "tls.crt" }}
|
||||
tls.key: {{ get $secretData "tls.key" }}
|
||||
{{- else }}
|
||||
ca.crt: {{ $ca.Cert | b64enc }}
|
||||
tls.crt: {{ $server.Cert | b64enc }}
|
||||
tls.key: {{ $server.Key | b64enc }}
|
||||
{{- end }}
|
||||
@@ -0,0 +1,28 @@
|
||||
apiVersion: v1
|
||||
kind: ConfigMap
|
||||
metadata:
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
data:
|
||||
aralez.yaml: |
|
||||
daemon: false
|
||||
upstreams_conf: /etc/aralez/upstreams.yaml
|
||||
proxy_configs: /etc/aralez-proxy
|
||||
proxy_address_http: "0.0.0.0:{{ .Values.hostPort.ports.http }}"
|
||||
proxy_address_tls: "0.0.0.0:{{ .Values.hostPort.ports.https }}"
|
||||
config_api_enabled: false
|
||||
config_address: "0.0.0.0:3000"
|
||||
upgrade_sock: /tmp/aralez.sock
|
||||
pid_file: /tmp/aralez.pid
|
||||
log_level: debug
|
||||
hc_method: HEAD
|
||||
hc_interval: 5
|
||||
|
||||
upstreams.yaml: |
|
||||
provider: "kubernetes"
|
||||
sticky_sessions: 172000
|
||||
kubernetes: {}
|
||||
{{- with .Values.upstreams }}
|
||||
{{- toYaml . | nindent 4 }}
|
||||
{{- end }}
|
||||
@@ -0,0 +1,130 @@
|
||||
apiVersion: apps/v1
|
||||
{{- if .Values.useDaemonSet }}
|
||||
kind: DaemonSet
|
||||
{{- else }}
|
||||
kind: Deployment
|
||||
{{- end }}
|
||||
metadata:
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
spec:
|
||||
{{- if not (or .Values.autoscaling.enabled .Values.useDaemonSet) }}
|
||||
replicas: {{ .Values.replicaCount }}
|
||||
{{- end }}
|
||||
{{- if not .Values.useDaemonSet }}
|
||||
strategy:
|
||||
type: {{ .Values.updateStrategy.type }}
|
||||
{{- else }}
|
||||
updateStrategy:
|
||||
type: {{ .Values.updateStrategy.type }}
|
||||
{{- end }}
|
||||
selector:
|
||||
matchLabels:
|
||||
{{- include "aralez.selectorLabels" . | nindent 6 }}
|
||||
template:
|
||||
metadata:
|
||||
{{- with .Values.podAnnotations }}
|
||||
annotations:
|
||||
{{- toYaml . | nindent 8 }}
|
||||
{{- end }}
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 8 }}
|
||||
{{- with .Values.podLabels }}
|
||||
{{- toYaml . | nindent 8 }}
|
||||
{{- end }}
|
||||
annotations:
|
||||
{{- if .Values.upstreams }}
|
||||
checksum/upstreams: {{ toJson .Values.upstreams | sha256sum }}
|
||||
{{- end }}
|
||||
spec:
|
||||
enableServiceLinks: false
|
||||
{{- if and .Values.hostNetwork .Values.useDaemonSet }}
|
||||
hostNetwork: {{ .Values.hostNetwork }}
|
||||
dnsPolicy: "ClusterFirstWithHostNet"
|
||||
{{- end }}
|
||||
{{- if .Values.priorityClassName }}
|
||||
priorityClassName: {{ .Values.priorityClassName }}
|
||||
{{- end }}
|
||||
{{- with .Values.imagePullSecrets }}
|
||||
imagePullSecrets:
|
||||
{{- toYaml . | nindent 8 }}
|
||||
{{- end }}
|
||||
serviceAccountName: {{ include "aralez.serviceAccountName" . }}
|
||||
securityContext:
|
||||
{{- toYaml .Values.podSecurityContext | nindent 8 }}
|
||||
{{- if .Values.terminationGracePeriodSeconds }}
|
||||
terminationGracePeriodSeconds: {{ .Values.terminationGracePeriodSeconds }}
|
||||
{{- end }}
|
||||
containers:
|
||||
- name: {{ .Chart.Name }}
|
||||
securityContext:
|
||||
{{- toYaml .Values.securityContext | nindent 12 }}
|
||||
image: "{{ .Values.image.repository }}:{{ .Values.image.tag | default .Chart.AppVersion }}"
|
||||
imagePullPolicy: {{ .Values.image.pullPolicy }}
|
||||
command: ["aralez"]
|
||||
args:
|
||||
- --conf=/etc/aralez/aralez.yaml
|
||||
{{- range $value := .Values.args }}
|
||||
- {{ $value }}
|
||||
{{- end }}
|
||||
env:
|
||||
{{- with .Values.env }}
|
||||
{{- . | toYaml | nindent 12 }}
|
||||
{{- end }}
|
||||
ports:
|
||||
{{- if .Values.hostPort.ports.http }}
|
||||
- name: http
|
||||
containerPort: {{ .Values.hostPort.ports.http }}
|
||||
protocol: TCP
|
||||
{{- end }}
|
||||
{{- if .Values.hostPort.ports.https }}
|
||||
- name: https
|
||||
containerPort: {{ .Values.hostPort.ports.https }}
|
||||
protocol: TCP
|
||||
{{- end }}
|
||||
# readinessProbe:
|
||||
# httpGet:
|
||||
# path: /status
|
||||
# port: 3000
|
||||
# initialDelaySeconds: 30
|
||||
# timeoutSeconds: 5
|
||||
resources:
|
||||
{{- toYaml .Values.resources | nindent 12 }}
|
||||
volumeMounts:
|
||||
- name: config
|
||||
mountPath: /etc/aralez
|
||||
- name: tlscerts
|
||||
mountPath: /etc/aralez-proxy/certificates
|
||||
{{- with .Values.volumeMounts }}
|
||||
{{- toYaml . | nindent 12 }}
|
||||
{{- end }}
|
||||
volumes:
|
||||
- name: config
|
||||
configMap:
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
- name: tlscerts
|
||||
secret:
|
||||
secretName: {{ include "aralez.fullname" . }}-tls
|
||||
defaultMode: 256
|
||||
items:
|
||||
- key: tls.crt
|
||||
path: tls.crt
|
||||
- key: tls.key
|
||||
path: tls.key
|
||||
{{- with .Values.volumes }}
|
||||
{{- toYaml . | nindent 8 }}
|
||||
{{- end }}
|
||||
{{- with .Values.nodeSelector }}
|
||||
nodeSelector:
|
||||
{{- toYaml . | nindent 8 }}
|
||||
{{- end }}
|
||||
affinity:
|
||||
{{- include "affinities.pods" . | nindent 8 }}
|
||||
{{- with .Values.affinity }}
|
||||
{{- toYaml . | nindent 8 }}
|
||||
{{- end }}
|
||||
{{- with .Values.tolerations }}
|
||||
tolerations:
|
||||
{{- toYaml . | nindent 8 }}
|
||||
{{- end }}
|
||||
@@ -0,0 +1,24 @@
|
||||
{{- if and .Values.autoscaling.enabled (not .Values.useDaemonSet) }}
|
||||
apiVersion: autoscaling/v2
|
||||
kind: HorizontalPodAutoscaler
|
||||
metadata:
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
spec:
|
||||
scaleTargetRef:
|
||||
apiVersion: apps/v1
|
||||
kind: Deployment
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
minReplicas: {{ .Values.autoscaling.minReplicas }}
|
||||
maxReplicas: {{ .Values.autoscaling.maxReplicas }}
|
||||
metrics:
|
||||
{{- if .Values.autoscaling.targetCPUUtilizationPercentage }}
|
||||
- type: Resource
|
||||
resource:
|
||||
name: cpu
|
||||
target:
|
||||
type: Utilization
|
||||
averageUtilization: {{ .Values.autoscaling.targetCPUUtilizationPercentage }}
|
||||
{{- end }}
|
||||
{{- end }}
|
||||
@@ -0,0 +1,10 @@
|
||||
{{- if .Values.ingressClassResource.enabled -}}
|
||||
apiVersion: networking.k8s.io/v1
|
||||
kind: IngressClass
|
||||
metadata:
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
name: {{ .Values.ingressClass }}
|
||||
spec:
|
||||
controller: {{ .Values.ingressClassResource.controllerValue }}
|
||||
{{- end }}
|
||||
@@ -0,0 +1,41 @@
|
||||
apiVersion: v1
|
||||
kind: Service
|
||||
metadata:
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
{{- with .Values.service.annotations }}
|
||||
annotations:
|
||||
{{- toYaml . | nindent 4 }}
|
||||
{{- end }}
|
||||
spec:
|
||||
type: {{ .Values.service.type }}
|
||||
{{- if eq .Values.service.type "NodePort" }}
|
||||
externalTrafficPolicy: Local
|
||||
{{- end }}
|
||||
{{- with .Values.service.ipFamilies }}
|
||||
ipFamilies:
|
||||
{{- toYaml . | nindent 4 }}
|
||||
{{- end }}
|
||||
ipFamilyPolicy: {{ if eq (len .Values.service.ipFamilies) 2 }}PreferDualStack{{ else }}SingleStack{{ end }}
|
||||
ports:
|
||||
{{- if .Values.hostPort.ports.http }}
|
||||
- port: 80
|
||||
targetPort: http
|
||||
protocol: TCP
|
||||
name: http
|
||||
{{- if .Values.hostPort.enabled }}
|
||||
nodePort: {{ .Values.hostPort.ports.http }}
|
||||
{{- end }}
|
||||
{{- end }}
|
||||
{{- if .Values.hostPort.ports.https }}
|
||||
- port: 443
|
||||
targetPort: https
|
||||
protocol: TCP
|
||||
name: https
|
||||
{{- if .Values.hostPort.enabled }}
|
||||
nodePort: {{ .Values.hostPort.ports.https }}
|
||||
{{- end }}
|
||||
{{- end }}
|
||||
selector:
|
||||
{{- include "aralez.selectorLabels" . | nindent 4 }}
|
||||
@@ -0,0 +1,52 @@
|
||||
{{- if .Values.serviceAccount.create -}}
|
||||
apiVersion: v1
|
||||
kind: ServiceAccount
|
||||
metadata:
|
||||
name: {{ include "aralez.serviceAccountName" . }}
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
{{- with .Values.serviceAccount.annotations }}
|
||||
annotations:
|
||||
{{- toYaml . | nindent 4 }}
|
||||
{{- end }}
|
||||
automountServiceAccountToken: true
|
||||
{{- end }}
|
||||
---
|
||||
apiVersion: rbac.authorization.k8s.io/v1
|
||||
kind: ClusterRole
|
||||
metadata:
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
rules:
|
||||
- apiGroups: ["networking.k8s.io"]
|
||||
resources: ["ingresses", "ingressclasses"]
|
||||
verbs: ["get", "list", "watch"]
|
||||
- apiGroups: ["networking.k8s.io"]
|
||||
resources: ["ingresses/status"]
|
||||
verbs: ["get", "update", "patch"]
|
||||
- apiGroups: [""]
|
||||
resources: ["secrets"]
|
||||
verbs: ["get", "list", "watch"]
|
||||
- apiGroups: [""]
|
||||
resources: ["nodes", "services", "endpoints"]
|
||||
verbs: ["get", "list", "watch"]
|
||||
- apiGroups: ["discovery.k8s.io"]
|
||||
resources: ["endpointslices"]
|
||||
verbs: ["get", "list", "watch"]
|
||||
|
||||
---
|
||||
apiVersion: rbac.authorization.k8s.io/v1
|
||||
kind: ClusterRoleBinding
|
||||
metadata:
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
labels:
|
||||
{{- include "aralez.labels" . | nindent 4 }}
|
||||
roleRef:
|
||||
apiGroup: rbac.authorization.k8s.io
|
||||
kind: ClusterRole
|
||||
name: {{ include "aralez.fullname" . }}
|
||||
subjects:
|
||||
- kind: ServiceAccount
|
||||
name: {{ include "aralez.serviceAccountName" . }}
|
||||
namespace: {{ .Release.Namespace }}
|
||||
@@ -0,0 +1,164 @@
|
||||
# Default values for aralez.
|
||||
# This is a YAML-formatted file.
|
||||
# Declare variables to be passed into your templates.
|
||||
|
||||
replicaCount: 1
|
||||
|
||||
image:
|
||||
repository: ghcr.io/sadoyan/aralez
|
||||
pullPolicy: IfNotPresent
|
||||
# Overrides the image tag whose default is the chart appVersion.
|
||||
tag: ""
|
||||
|
||||
imagePullSecrets: []
|
||||
nameOverride: ""
|
||||
fullnameOverride: ""
|
||||
|
||||
# -- Environment variables
|
||||
env: []
|
||||
|
||||
# -- Aralez arguments
|
||||
args: []
|
||||
|
||||
# -- Aralez upstreams file body
|
||||
# refs: https://aralez.rs/docs/kubernetes/
|
||||
upstreams:
|
||||
rate_limit: 500000
|
||||
x4xx_limit: 100000
|
||||
to_https: true
|
||||
server_headers:
|
||||
- "X-Forwarded-Proto:https"
|
||||
- "X-Forwarded-Port:443"
|
||||
|
||||
serviceAccount:
|
||||
# Specifies whether a service account should be created
|
||||
create: true
|
||||
# Annotations to add to the service account
|
||||
annotations: {}
|
||||
# The name of the service account to use.
|
||||
# If not set and create is true, a name is generated using the fullname template
|
||||
name: ""
|
||||
|
||||
# -- Annotations for pod.
|
||||
# ref: https://kubernetes.io/docs/concepts/overview/working-with-objects/annotations/
|
||||
podAnnotations: {}
|
||||
# cluster-autoscaler.kubernetes.io/safe-to-evict: "false"
|
||||
|
||||
# -- Extra labels for pod.
|
||||
# ref: https://kubernetes.io/docs/concepts/overview/working-with-objects/labels/
|
||||
podLabels: {}
|
||||
|
||||
# -- Pod Security Context.
|
||||
# ref: https://kubernetes.io/docs/tasks/configure-pod-container/security-context/#set-the-security-context-for-a-pod
|
||||
podSecurityContext:
|
||||
runAsNonRoot: true
|
||||
runAsUser: 9999
|
||||
runAsGroup: 9999
|
||||
fsGroup: 9999
|
||||
fsGroupChangePolicy: "OnRootMismatch"
|
||||
|
||||
# -- Container Security Context.
|
||||
# ref: https://kubernetes.io/docs/tasks/configure-pod-container/security-context/#set-the-security-context-for-a-pod
|
||||
securityContext:
|
||||
seccompProfile:
|
||||
type: RuntimeDefault
|
||||
allowPrivilegeEscalation: false
|
||||
capabilities:
|
||||
drop:
|
||||
- ALL
|
||||
|
||||
# -- Pod host network
|
||||
# Use it only for performance reason
|
||||
hostNetwork: false
|
||||
|
||||
# -- Service node port
|
||||
# refs: https://kubernetes.io/docs/concepts/services-networking/service/#type-nodeport
|
||||
hostPort:
|
||||
enabled: false
|
||||
ports:
|
||||
http: 8080
|
||||
https: 8443
|
||||
|
||||
ingressClass: aralez
|
||||
ingressClassResource:
|
||||
enabled: true
|
||||
controllerValue: aralez.proxy/ingress-controller
|
||||
|
||||
# -- Bitwarden service parameters
|
||||
# ref: https://kubernetes.io/docs/user-guide/services/
|
||||
service:
|
||||
# -- service type
|
||||
type: ClusterIP
|
||||
|
||||
annotations: {}
|
||||
|
||||
# -- IP families for service
|
||||
# possible values: IPv4, IPv6
|
||||
# ref: https://kubernetes.io/docs/concepts/services-networking/dual-stack/
|
||||
ipFamilies: [IPv4]
|
||||
|
||||
# -- Resource requests and limits.
|
||||
# ref: https://kubernetes.io/docs/user-guide/compute-resources/
|
||||
resources:
|
||||
limits:
|
||||
cpu: 1
|
||||
memory: 512Mi
|
||||
requests:
|
||||
cpu: 100m
|
||||
memory: 128Mi
|
||||
|
||||
# -- Horizontal and Vertical pod autoscaler.
|
||||
# ref: https://kubernetes.io/docs/tasks/run-application/horizontal-pod-autoscale/
|
||||
autoscaling:
|
||||
enabled: false
|
||||
|
||||
minReplicas: 1
|
||||
maxReplicas: 10
|
||||
targetCPUUtilizationPercentage: 80
|
||||
|
||||
# -- Use a daemonset instead of a deployment
|
||||
useDaemonSet: false
|
||||
|
||||
# -- The time in seconds that is allowed for a Aralez instance to gracefully shutdown
|
||||
# ref: https://kubernetes.io/docs/concepts/containers/container-lifecycle-hooks
|
||||
terminationGracePeriodSeconds: 120
|
||||
|
||||
## updateStrategy for PostgreSQL StatefulSet and its slaves StatefulSets
|
||||
## ref: https://kubernetes.io/docs/concepts/workloads/controllers/statefulset/#update-strategies
|
||||
updateStrategy:
|
||||
type: RollingUpdate
|
||||
rollingUpdate:
|
||||
maxUnavailable: 1
|
||||
|
||||
# -- Priority Class Name
|
||||
# ref: https://kubernetes.io/docs/concepts/configuration/pod-priority-preemption/#priorityclass
|
||||
priorityClassName: ""
|
||||
|
||||
# Additional volumes on the output Deployment definition.
|
||||
volumes: []
|
||||
# - name: foo
|
||||
# secret:
|
||||
# secretName: mysecret
|
||||
# optional: false
|
||||
|
||||
# Additional volumeMounts on the output Deployment definition.
|
||||
volumeMounts: []
|
||||
# - name: foo
|
||||
# mountPath: "/etc/foo"
|
||||
# readOnly: true
|
||||
|
||||
# -- Node labels for pod assignment.
|
||||
# ref: https://kubernetes.io/docs/user-guide/node-selection/
|
||||
nodeSelector: {}
|
||||
|
||||
# -- Tolerations for pod assignment.
|
||||
# ref: https://kubernetes.io/docs/concepts/configuration/taint-and-toleration/
|
||||
tolerations: []
|
||||
|
||||
# -- Pod Anti Affinity
|
||||
# soft/hard
|
||||
podAntiAffinityPreset: soft
|
||||
|
||||
# -- Affinity for pod assignment.
|
||||
# ref: https://kubernetes.io/docs/concepts/configuration/assign-pod-node/#affinity-and-anti-affinity
|
||||
affinity: {}
|
||||
@@ -0,0 +1,66 @@
|
||||
job "apache" {
|
||||
meta {
|
||||
uuid = uuidv4()
|
||||
}
|
||||
datacenters = ["eu-ams-1"]
|
||||
type = "service"
|
||||
constraint {
|
||||
attribute = node.unique.name
|
||||
operator = "regexp"
|
||||
value = "consul[0-9]"
|
||||
}
|
||||
update {
|
||||
max_parallel = 1
|
||||
min_healthy_time = "10s"
|
||||
healthy_deadline = "3m"
|
||||
progress_deadline = "10m"
|
||||
auto_revert = false
|
||||
canary = 0
|
||||
}
|
||||
migrate {
|
||||
max_parallel = 1
|
||||
health_check = "checks"
|
||||
min_healthy_time = "10s"
|
||||
healthy_deadline = "5m"
|
||||
}
|
||||
group "Apache" {
|
||||
network {
|
||||
port "apache" { to = 80 }
|
||||
}
|
||||
constraint {
|
||||
operator = "distinct_hosts"
|
||||
value = "true"
|
||||
}
|
||||
count = 3
|
||||
restart {
|
||||
attempts = 2
|
||||
interval = "30m"
|
||||
delay = "15s"
|
||||
mode = "fail"
|
||||
}
|
||||
task "health" {
|
||||
service {
|
||||
port = "apache"
|
||||
tags = [
|
||||
"aralez.service=yes",
|
||||
"aralez.host=apache.example.com",
|
||||
"aralez.path=/",
|
||||
"aralez.redirect=http://checkip.amazonaws.com"
|
||||
]
|
||||
check {
|
||||
type = "http"
|
||||
port = "apache"
|
||||
path = "/"
|
||||
interval = "5s"
|
||||
timeout = "2s"
|
||||
}
|
||||
}
|
||||
driver = "docker"
|
||||
config {
|
||||
image = "httpd:latest"
|
||||
force_pull = true
|
||||
ports = ["apache"]
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,70 @@
|
||||
job "echo" {
|
||||
meta {
|
||||
uuid = uuidv4()
|
||||
}
|
||||
datacenters = ["eu-ams-1"]
|
||||
type = "service"
|
||||
constraint {
|
||||
attribute = node.unique.name
|
||||
operator = "regexp"
|
||||
value = "consul[0-9]"
|
||||
}
|
||||
update {
|
||||
max_parallel = 1
|
||||
min_healthy_time = "10s"
|
||||
healthy_deadline = "3m"
|
||||
progress_deadline = "10m"
|
||||
auto_revert = false
|
||||
canary = 0
|
||||
}
|
||||
migrate {
|
||||
max_parallel = 1
|
||||
health_check = "checks"
|
||||
min_healthy_time = "10s"
|
||||
healthy_deadline = "5m"
|
||||
}
|
||||
group "Echo" {
|
||||
network {
|
||||
port "echo" { to = 80 }
|
||||
}
|
||||
constraint {
|
||||
operator = "distinct_hosts"
|
||||
value = "true"
|
||||
}
|
||||
count = 3
|
||||
restart {
|
||||
attempts = 2
|
||||
interval = "30m"
|
||||
delay = "15s"
|
||||
mode = "fail"
|
||||
}
|
||||
task "server" {
|
||||
service {
|
||||
port = "echo"
|
||||
tags = [
|
||||
"aralez.service=yes",
|
||||
"aralez.host=echo.example.com",
|
||||
"aralez.path=/",
|
||||
"aralez.rate=20",
|
||||
"aralez.4xx_rate=10",
|
||||
"aralez.to_https=true",
|
||||
"aralez.client_header=X-Client-Header:Some simple header",
|
||||
"aralez.server_header=X-Server-Header:Some simple header",
|
||||
]
|
||||
check {
|
||||
type = "http"
|
||||
port = "echo"
|
||||
path = "/"
|
||||
interval = "5s"
|
||||
timeout = "2s"
|
||||
}
|
||||
}
|
||||
driver = "docker"
|
||||
config {
|
||||
image = "ealen/echo-server:latest"
|
||||
force_pull = true
|
||||
ports = ["echo"]
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,72 @@
|
||||
job "nginx" {
|
||||
meta {
|
||||
uuid = uuidv4()
|
||||
}
|
||||
datacenters = ["eu-ams-1"]
|
||||
type = "service"
|
||||
constraint {
|
||||
attribute = node.unique.name
|
||||
operator = "regexp"
|
||||
value = "consul[0-9]"
|
||||
}
|
||||
update {
|
||||
max_parallel = 1
|
||||
min_healthy_time = "10s"
|
||||
healthy_deadline = "3m"
|
||||
progress_deadline = "10m"
|
||||
auto_revert = false
|
||||
canary = 0
|
||||
}
|
||||
migrate {
|
||||
max_parallel = 1
|
||||
health_check = "checks"
|
||||
min_healthy_time = "10s"
|
||||
healthy_deadline = "5m"
|
||||
}
|
||||
group "NginX" {
|
||||
network {
|
||||
port "nginx" { to = 80 }
|
||||
}
|
||||
constraint {
|
||||
operator = "distinct_hosts"
|
||||
value = "true"
|
||||
}
|
||||
count = 3
|
||||
restart {
|
||||
attempts = 2
|
||||
interval = "30m"
|
||||
delay = "15s"
|
||||
mode = "fail"
|
||||
}
|
||||
task "server" {
|
||||
service {
|
||||
port = "nginx"
|
||||
tags = [
|
||||
"aralez.service=yes",
|
||||
"aralez.host=nginx.example.com",
|
||||
"aralez.path=/",
|
||||
"aralez.rate=1",
|
||||
"aralez.4xx_rate=10",
|
||||
"aralez.to_https=true",
|
||||
"aralez.client_header=X-Some:Some Random Header",
|
||||
"aralez.client_header=X-Emos:Redaeh Modnar Emos",
|
||||
"aralez.server_header=X-From:Aralez & Consul",
|
||||
"aralez.server_header=X-Mrof: Lusnoc & Zelara",
|
||||
]
|
||||
check {
|
||||
type = "http"
|
||||
port = "nginx"
|
||||
path = "/"
|
||||
interval = "5s"
|
||||
timeout = "2s"
|
||||
}
|
||||
}
|
||||
driver = "docker"
|
||||
config {
|
||||
image = "nginx:latest"
|
||||
force_pull = true
|
||||
ports = ["nginx"]
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,8 @@
|
||||
# 1. Define the IngressClass so Kubernetes knows "aralez" is a valid controller
|
||||
apiVersion: networking.k8s.io/v1
|
||||
kind: IngressClass
|
||||
metadata:
|
||||
name: aralez
|
||||
namespace: upstreams
|
||||
spec:
|
||||
controller: aralez.proxy/ingress-controller
|
||||
@@ -0,0 +1,76 @@
|
||||
apiVersion: apps/v1
|
||||
kind: Deployment
|
||||
metadata:
|
||||
name: aralez
|
||||
namespace: aralez
|
||||
labels:
|
||||
app.kubernetes.io/name: aralez
|
||||
app.kubernetes.io/component: ingress-controller
|
||||
spec:
|
||||
replicas: 1
|
||||
selector:
|
||||
matchLabels:
|
||||
app: aralez
|
||||
template:
|
||||
metadata:
|
||||
labels:
|
||||
app: aralez
|
||||
spec:
|
||||
serviceAccountName: aralez-sa
|
||||
containers:
|
||||
- name: aralez
|
||||
#image: sadoyan/aralez:latest
|
||||
image: nginx:latest
|
||||
imagePullPolicy: IfNotPresent
|
||||
env:
|
||||
- name: ARALEZ_SERVICE_NAME
|
||||
value: "aralez-service"
|
||||
- name: ARALEZ_SERVICE_NAMESPACE
|
||||
value: "aralez"
|
||||
- name: ARALEZ_EXTERNAL_IP # Only for bare metal deployment, remove this in Cloud.
|
||||
value: "192.168.10.10" # Only for bare metal deployment, remove this in Cloud.
|
||||
|
||||
ports:
|
||||
- name: http
|
||||
containerPort: 80
|
||||
- name: https
|
||||
containerPort: 443
|
||||
readinessProbe:
|
||||
tcpSocket:
|
||||
port: 80
|
||||
initialDelaySeconds: 3
|
||||
periodSeconds: 5
|
||||
livenessProbe:
|
||||
tcpSocket:
|
||||
port: 80
|
||||
initialDelaySeconds: 10
|
||||
periodSeconds: 10
|
||||
resources:
|
||||
requests:
|
||||
cpu: "100m"
|
||||
memory: "128Mi"
|
||||
limits:
|
||||
cpu: "1"
|
||||
memory: "512Mi"
|
||||
volumeMounts:
|
||||
- name: main-config
|
||||
mountPath: /etc/aralez/main.yaml
|
||||
subPath: main.yaml
|
||||
readOnly: true
|
||||
- name: upstreams-config
|
||||
mountPath: /etc/aralez/upstreams.yml
|
||||
subPath: upstreams.yml
|
||||
readOnly: true
|
||||
- name: tls-certs
|
||||
mountPath: /etc/aralez/certificates
|
||||
readOnly: true
|
||||
volumes:
|
||||
- name: main-config
|
||||
configMap:
|
||||
name: aralez-main-config
|
||||
- name: upstreams-config
|
||||
configMap:
|
||||
name: aralez-upstreams-config
|
||||
- name: tls-certs
|
||||
secret:
|
||||
secretName: aralez-tls
|
||||
@@ -0,0 +1,17 @@
|
||||
apiVersion: v1
|
||||
kind: Service
|
||||
metadata:
|
||||
name: aralez-service
|
||||
namespace: aralez
|
||||
spec:
|
||||
type: NodePort
|
||||
selector:
|
||||
app: aralez
|
||||
ports:
|
||||
- name: http
|
||||
port: 80
|
||||
targetPort: 80
|
||||
- name: https
|
||||
port: 443
|
||||
targetPort: 443
|
||||
|
||||
@@ -0,0 +1,9 @@
|
||||
apiVersion: v1
|
||||
kind: Secret
|
||||
metadata:
|
||||
name: aralez-tls
|
||||
namespace: aralez
|
||||
type: kubernetes.io/tls
|
||||
data:
|
||||
tls.crt: LS0tLS1CRUdJTiBDRVJUSUZJQ0FURS0tLS0tCk1JSUY3ekNDQTllZ0F3SUJBZ0lVUm12YytSU25LS01HNXVaV1JNS3NtS2dwU1drd0RRWUpLb1pJaHZjTkFRRUwKQlFBd2dZWXhDekFKQmdOVkJBWVRBbGhZTVJJd0VBWURWUVFJREFsVGRHRjBaVTVoYldVeEVUQVBCZ05WQkFjTQpDRU5wZEhsT1lXMWxNUlF3RWdZRFZRUUtEQXREYjIxd1lXNTVUbUZ0WlRFYk1Ca0dBMVVFQ3d3U1EyOXRjR0Z1CmVWTmxZM1JwYjI1T1lXMWxNUjB3R3dZRFZRUUREQlJEYjIxdGIyNU9ZVzFsVDNKSWIzTjBibUZ0WlRBZUZ3MHkKTmpBNE1UZ3hOREkwTVRKYUZ3MHpOakE0TVRVeE5ESTBNVEphTUlHR01Rc3dDUVlEVlFRR0V3SllXREVTTUJBRwpBMVVFQ0F3SlUzUmhkR1ZPWVcxbE1SRXdEd1lEVlFRSERBaERhWFI1VG1GdFpURVVNQklHQTFVRUNnd0xRMjl0CmNHRnVlVTVoYldVeEd6QVpCZ05WQkFzTUVrTnZiWEJoYm5sVFpXTjBhVzl1VG1GdFpURWRNQnNHQTFVRUF3d1UKUTI5dGJXOXVUbUZ0WlU5eVNHOXpkRzVoYldVd2dnSWlNQTBHQ1NxR1NJYjNEUUVCQVFVQUE0SUNEd0F3Z2dJSwpBb0lDQVFEQklZejBUNDRnVnZWdTBPMlA3NEV3NzE1c3FDekZuWHhTRDE4RnNCRHE2L1NadW1qYmpvTXBjWFZhCkVVQVQwMXpxRW9JZm5waHY3VExNWmtNNmZ6WTFNVGdOcXVqeHVXUGNVMTBES2VQa0Y1K1RPbWdoUUE1ODRCV1gKcmZrMlp5NXpGT012ODZUZXFCOGRyUVh2SWpHNTZhMW5DMFMwSFlnTnJ6R2srVXdrNWpDZTlaYURnc3Q5VlkrcApRYlZyUVdwR2V6RDl3WVE2bU41MkRGRERYbnp6WUVwRWVVekwwNkpNSlE5M2d5ZDVtbWd4aWlpbU1QMS9UTG5BClo2cWlYQ05UVGQvMERiL2tVWW9tK1hkTm11em83Qm1qaDY4ZzVTYUtYWkJXM25BQnhoaUVkZHoyaUViTGx2UFIKcXltcjVzazgyYlZQTWlWUC82alFLaTk0anBxVDc4ZVZZRG81dmhyMDQvczhVZk9xWVBEY0NLTGFzOEpBdTRvUwpoTnRjYm5GbGJjOG1Qcm00bnY2NlhKUUpIV1cwU1Rqc1pZWVRTRTllM3lMV2JqRlpUQTBIb3lQV1dDS1ZXSS82CnExa09IcnhJWitzOStHajB3aUJhdUpsbWk2by9oZE5qWUhsY2sxbnFTM2l6UXZ2WFpuSWtwTWkrU2pQRzhBZ0MKdEFqSWVPNlFOZVFFM3p3d3ZJb09tRnVTMC8zWkJFSkZuaWdxV0xuKzRidnV4eTNReW5JWHNsY250dDRXbjdMTAp0MWZtMTU3a2x6TUNHeHBWVXFqT1FwVnVuVnVmMDdURHdWbGxxek96TXlxZWdYSHlYODJxVlV2czdidCtpZFdOCngrdks1RUtrQUhidU9QV3lGRkJJci91aE93OWZsOEUxR1ZUYzg1OG5pM0NrWWtGeEpRSURBUUFCbzFNd1VUQWQKQmdOVkhRNEVGZ1FVQkFya1htNXZ2dDhmNVRGdkI0YmJNVS9EcEc4d0h3WURWUjBqQkJnd0ZvQVVCQXJrWG01dgp2dDhmNVRGdkI0YmJNVS9EcEc4d0R3WURWUjBUQVFIL0JBVXdBd0VCL3pBTkJna3Foa2lHOXcwQkFRc0ZBQU9DCkFnRUFYdGJ3TVpkOElrTkxwWGFHeTRleGR6OVN0dVpjYnBhWjVWeURTdTJBdFZERm1BeXNSM0hHaEhWend5a0cKOGtibGdQQ3B3OEhWeGdMd0xmNHFuTWhvdUNHQ3ZiMVd2UjM5VW45NmVOWFA5cHFDTWhRTzFMU0JCSy80UllsUwp4ajhyRlBub3p5OHdFTzRwR1VaejN3LzJIdXgyTGovVHIxRXY5cklsa0hMZ3plazc1clpHTUIxUHhsRU1zUGNsCmtGY3NacGZ5TE5LM0FydUMzbmVGbldSODh5UHFVU3FwVEJ1OVRubjZUQ002TXVEZHlaRTZXYVlGU01zNzBJOU8KN3c5SkdreDc0UlAraTBQeUZUOFNhbUdncTUxWmtrUFZnK3ZZSUhTbGszdGlxZFN0MEYzMnVNaHNDZXZCcVUzQQp2M3lUOW9UUlpRZE9XKzQySDZjVTJ4Q2FCTVBRdnpaZWRtYno1eTNpS1NjMDBQUy8vMDI4YjIzbHpGQVZjbURHCnlOaUcraUJUVkRydHgwZC9qdGhqdzV4cllqNFBnNXl6emM2R3hkaC9VWGpUN1dqSUpweThnR3V2MHhMWVNQTDYKMmROUkYyVDl1TDQ0Z1J2K09ndTRRaHNacGg3WWxNZVp0aVpoT1IvTC8yUWdnZDMrNEhpeXBNNFpiWkUrMVg2TQoyNEtVdG5wZU53dE0wR1huU01aY2dkUm5LMWg0WDQ2T1lMYW9vSTdERkhSUWJSclJQSWl1eXZ2NXpPQzF5NTFFCm9rY0tvMVREQThRcXVHMlBRay9kMEZ0LzNiOEJoOHJCcTR1V3lKWHYyYTJJUmt1Q05MN0Myck5Rem92ekF0aW4KZnB5ejVKb1NHc1dUSVhSYlNucnpocWxFeUJCRGxQQ3AxTW1zM2xzZkFROThIQmM9Ci0tLS0tRU5EIENFUlRJRklDQVRFLS0tLS0K
|
||||
tls.key: LS0tLS1CRUdJTiBQUklWQVRFIEtFWS0tLS0tCk1JSUpRUUlCQURBTkJna3Foa2lHOXcwQkFRRUZBQVNDQ1Nzd2dna25BZ0VBQW9JQ0FRREJJWXowVDQ0Z1Z2VnUKME8yUDc0RXc3MTVzcUN6Rm5YeFNEMThGc0JEcTYvU1p1bWpiam9NcGNYVmFFVUFUMDF6cUVvSWZucGh2N1RMTQpaa002ZnpZMU1UZ05xdWp4dVdQY1UxMERLZVBrRjUrVE9tZ2hRQTU4NEJXWHJmazJaeTV6Rk9Ndjg2VGVxQjhkCnJRWHZJakc1NmExbkMwUzBIWWdOcnpHaytVd2s1akNlOVphRGdzdDlWWStwUWJWclFXcEdlekQ5d1lRNm1ONTIKREZERFhuenpZRXBFZVV6TDA2Sk1KUTkzZ3lkNW1tZ3hpaWltTVAxL1RMbkFaNnFpWENOVFRkLzBEYi9rVVlvbQorWGRObXV6bzdCbWpoNjhnNVNhS1haQlczbkFCeGhpRWRkejJpRWJMbHZQUnF5bXI1c2s4MmJWUE1pVlAvNmpRCktpOTRqcHFUNzhlVllEbzV2aHIwNC9zOFVmT3FZUERjQ0tMYXM4SkF1NG9TaE50Y2JuRmxiYzhtUHJtNG52NjYKWEpRSkhXVzBTVGpzWllZVFNFOWUzeUxXYmpGWlRBMEhveVBXV0NLVldJLzZxMWtPSHJ4SVorczkrR2owd2lCYQp1SmxtaTZvL2hkTmpZSGxjazFucVMzaXpRdnZYWm5Ja3BNaStTalBHOEFnQ3RBakllTzZRTmVRRTN6d3d2SW9PCm1GdVMwLzNaQkVKRm5pZ3FXTG4rNGJ2dXh5M1F5bklYc2xjbnR0NFduN0xMdDFmbTE1N2tsek1DR3hwVlVxak8KUXBWdW5WdWYwN1REd1ZsbHF6T3pNeXFlZ1hIeVg4MnFWVXZzN2J0K2lkV054K3ZLNUVLa0FIYnVPUFd5RkZCSQpyL3VoT3c5Zmw4RTFHVlRjODU4bmkzQ2tZa0Z4SlFJREFRQUJBb0lDQUNjaHhDeXdmZXpCa2VOTlJBVlpFd1UyClN4eWJDczlUdEovdjYySDhwY0RqNUdETnEzZHBMZHhVMStGVEEzZkE2TitvdG1MdndKVlZLMmpOQTZ3em9Ha3cKdXRuU0duYjRDR3JaSFV5SnpWb25DemRLcTFTcFpRWWFaV1doWTVDSllaa0J6M0trM0hBZEFva0J5T1VHT2FzZwoxUGkvQ01HeUJpSTNzRWhzRnVpWEY1enR4L3lIb1BHWlI0MlUrY3hzcWJyME5SNEZldVJnbXhxeUxoOFg0eHR4CkZEdEJsTFRzQWNPSjh0TlZhTWN6NlE2NG5ybmx6VWRnNVhZOXl3NHd1eHVpK05DN2hIa2ZxRzF6T0tBcDF2enUKOGRiM3BCMTNNTkx5V0UreHJHSS9vREllcTVIc1ZPUGxoeXVoa2NUNTh5WjRPa3Q4cnFEQi9aT0lLS3cxd000RQp1S1h3VnhmMEZzZ09pSjhCME1iY1g4OTdEdUJrV29DeHorbVlwVzByTW9EWTlhcEI3ZllZZkN2ZVJXVWt3RmJnCkdhWDZPRndwWkU5cHBOOXR4YUpKYVgrdXowT3ZySWh4c1FPamtSdTA1cXl5NjcvTG04aFpoRkVMMm1PMjBOUGMKVWpVUHpoenF1M3NHaHltR01Kb21aa3VQR1FyYnlYR2lSVjl2dWhWSHlVa3EyWXJ5ZTJpeEpUMWgreDFBZXJHbgo2ZzQxWFA5UzVTNDUzTU8wUVFDcVQ2aG9ZUnBpbUxkYlpmZjJOTmt1ZFFINS9UVjZqTGN0SjZua212ZDVTbGhPCm9YSHdkcW9jVlkrUEVZZHRyVzE5OGxhVG9JVFZQZFBBOHdwL0pmb2pGK0hSM1owQmlBMUFsWjhzL0RsM0xLWVoKb2xHUUVnQ3kwQ2xVazFZa0FiYzFBb0lCQVFEZnNiZWlwOTNrNitjSGJHdTk2eE53b1RHMEdWVnkzWDBzeVhWSAppSERvdnpTNGtzY0c0SEpteHc2S2N0ZDR5eEIvaDRuZHZ2VkV0M3RqTFQ3VGxqOTlhNWJVaTZOS3ZyNll0ZGsxCk50elFTaXJjeG81M3dNUlRSeFVNZnVPQW1Ia3VKWXduZWVFMHcxdnRBZloyR0RnVTBGbGZicThkRFc2TlFZQ0gKS01wNUtWNnJyenE2Y1g1cGNWcWRZckp6Y2REbk5YeXUyUXBDT3FSZFhFQ3RnYmxWdmF6UTh2c0t0K3Awd1NpcgpCdmFqY3c1YW1iZ2x4Zm1uWWhNY2ZkWjRqR3NrVVJmWE5JMGZUcHRwMEdNVlFYZEFkL3BScThjKzljQU1LY3p6Ck9OL0NzVjVpbHpjUDBJZzB0bU50a0tVV3dKTGRKbkp1Z1Vud200SFFtUzJWNUUwL0FvSUJBUURkQmQ4Y0NUbUgKYmJUbmVjcHJnNkd4ZUN3aW95dnVkZVJZS2NCcGdvcW5uUVdEMm9LQmVDWC9HL1lJNVIwcWxLdXZBRlEvWEd3ZAp3N1pwYlZsbUcvQTBBRjNQeW5MMlFHSWhDN1Z6cHNrSFRPOU5VOTJjS0Fhd2Erbk9nZVJSbzBhOEhucGJpcktmCjlEdzkvcjhxTWVmdzhRS3JmMDVwMEVjVVJlTTR2WlJ1cGs5bVZac0x0QmxIMjhEYXE4YnJBYlNXUjNKN1RsZEkKMHZaZE9Cd0xxWkZVTWVOR09rUjN6azAvWDNXOWVIT3RmTkZYQzU3N1Bvby9vTDNobERDcnVXalZodkM0dUttdQpLTU5CMTM2ZnFuanZ6QXcrVTdMbkhHYTlQSHp5aUhFN1B3TVNiSGlBcXpFNXdBaDlLOWJGdEttUE0wN1FudTNSClBWMVlDNk1tMGxTYkFvSUJBQkFRRU9Hck1ESGFCckx2eENUVkZvWkY3TzNEeS9EOW1wbDJ0ZWMzRXZTRGxtT1MKbHB3VnplRTNkZ0hYRVVYcFB2d0pYWXNBeFZmejNQWllMMlMrS3p6MFZ0WllXSmRyYndCRVBwNmxtK0dSRWRiYwpveXBTTzBiSG1lbFZ5enhXdG96cndVNnNYOUdNSGJPOUtsZDhrYnBjNDY0SW9xWnhhbmpXTlVaL1ZWcXg3OHhnClB0VlloUDFKV0hwb3RldTRSb256dTBwSzU0T3Q5bE9GNWxjUE02SEdodnhTRmxqRXNCOUdKNGR3YnBGNkY1UEYKNmdVOFhCcjYzZWh6Mk15N09JNVpERjgxdE5TRXJvQkFxSHpFUUszdWI1a2h2cUwwdnArZytNaVdVdXNHRllMNgozTWRUOEJQbzdPYlhOaU9XSEhXbzV4cXNTZ1R2QmJsVzVvRVc3YjBDZ2dFQWZFOWRHT3VuUzZCTWF4UjQ0TmQ4CkRkREZJZ1ljSTFaelE1TFlBWC9HZEZkQVR0U0xLajVsUUlKOWNxdEtLRFRPQ3ZOb2J1cVFkSDByRDBqTlN6elQKY0t2MEYzYUtDaTVVQXJvUEtDamFVQnpaU3Vpc2I3T2piMzZDVmYrQVp0b3FZb3ZSemNMSWpHWlZxNWluOUJkMQptSEkxU2plajVxZWFFckRzQjNHNUZqSzczWmF3U1hqVjd6Q04yMjlaeGJ1RDBqSUZGWTBPVW9zMHZXRmRoTUd1ClYyaG5wNHdHRGt3ZDdsTEdhZlpoT1daR1oyckYxQkZzdURTMEZ6ZTkyQmZEK3JTV2w0NWxBT3MwUnNmcEUreFIKY0syWEJVY1dEQjVST29YVzBLSWs3V21YVkxsbFhSanI2c3N5K3hPNURDRjhiR296SGVzRlh2WGdsakNWWnJSTgptUUtDQVFCQ044M21FMllMVWtlUTUrWVVoS1kyYktQcS9GVnA2NWNPVXZ2R2RCNGxQUTlDU01xWUc0SHR5VFJUCmdzaEdvdjRrYk5NQ2JsdnlkWkttU1RKZk16bnJhdlYrbDVJekRFZWpEUXQrUzMxdWh5OXdiMVlIaFBRNStXZ2sKbnVMcUhzWE9WKzZuWmdyMzJvUVFxeVdlTjFkUW1XTUVoYWVOVVlwamxpTFNlUm55UjVNazBCbm55clJEZGV2NQpLekpyZmdYZG5CSGdJY3M4VmxoWXZoYlFDQmpNT2FIcXp1dXJ3M21VSVJxNlNWWVR5eHprZElEM2tna0VxbDdrCnEwL3RBbkhrNHZIS1JhSU1nSmdGOVVBRG50MHVpTFdVcTZBbCsyRU5sQW16VGhmQlAxOUVPSlFuNC85L0tnOXEKTXV3ZGxLSTl5MWRpQlBmdk00R3RIcGlYaEZnVQotLS0tLUVORCBQUklWQVRFIEtFWS0tLS0tCg==
|
||||
@@ -0,0 +1,73 @@
|
||||
# Define your Ingress resource targeting Aralez
|
||||
apiVersion: networking.k8s.io/v1
|
||||
kind: Ingress
|
||||
metadata:
|
||||
name: api-service-v2
|
||||
namespace: upstreams
|
||||
annotations:
|
||||
# Custom annotations parsed by Aralez
|
||||
aralez.rs/rate_limit: "100"
|
||||
aralez.rs/x4xx_limit: "20"
|
||||
aralez.rs/client_headers: '["X-Proxy-From:Aralezzzzzzzzzzz", "X-Hopar-From:Hopaaaaaaaaaaaar"]'
|
||||
aralez.rs/server_headers: '["X-Proxy-Version:Aralez", "X-Po-From:Kung Fu Panda"]'
|
||||
spec:
|
||||
ingressClassName: aralez # Matches the IngressClass metadata.name above
|
||||
rules:
|
||||
- host: api-service-v2.blabla.com
|
||||
http:
|
||||
paths:
|
||||
- path: /
|
||||
pathType: Prefix
|
||||
backend:
|
||||
service:
|
||||
name: api-service-v2
|
||||
port:
|
||||
number: 80
|
||||
---
|
||||
# Define your Ingress resource targeting Aralez
|
||||
apiVersion: networking.k8s.io/v1
|
||||
kind: Ingress
|
||||
metadata:
|
||||
name: wss-service-v2
|
||||
namespace: upstreams
|
||||
annotations:
|
||||
# Custom annotations parsed by Aralez
|
||||
aralez.rs/rate_limit: "50"
|
||||
aralez.rs/x4xx_limit: "10"
|
||||
aralez.rs/client_headers: '["X-Hors-Arev:Naturi", "X-Grand-Master:Oogway"]'
|
||||
aralez.rs/server_headers: '["X-Mors-Arev:Hastat", "X-Shifu-Master:Shifu"]'
|
||||
spec:
|
||||
ingressClassName: aralez # Matches the IngressClass metadata.name above
|
||||
rules:
|
||||
- host: wss-service-v2.blabla.com
|
||||
http:
|
||||
paths:
|
||||
- path: /
|
||||
pathType: Prefix
|
||||
backend:
|
||||
service:
|
||||
name: svc-nginx
|
||||
port:
|
||||
number: 80
|
||||
|
||||
---
|
||||
# Define your Ingress resource targeting Aralez
|
||||
apiVersion: networking.k8s.io/v1
|
||||
kind: Ingress
|
||||
metadata:
|
||||
name: joj-service-v2
|
||||
namespace: upstreams
|
||||
spec:
|
||||
ingressClassName: aralez # Matches the IngressClass metadata.name above
|
||||
rules:
|
||||
- host: joj-service-v2.blabla.com
|
||||
http:
|
||||
paths:
|
||||
- path: /
|
||||
pathType: Prefix
|
||||
backend:
|
||||
service:
|
||||
name: svc-nginx
|
||||
port:
|
||||
number: 80
|
||||
|
||||
@@ -0,0 +1,16 @@
|
||||
threads: 12
|
||||
daemon: false
|
||||
upstream_keepalive_pool_size: 500
|
||||
pid_file: /tmp/aralez.pid
|
||||
error_log: /tmp/aralez_err.log
|
||||
upgrade_sock: /tmp/aralez.sock
|
||||
config_api_enabled: false
|
||||
config_address: 127.0.0.1:3000
|
||||
proxy_address_http: 0.0.0.0:80
|
||||
proxy_address_tls: 0.0.0.0:443
|
||||
proxy_configs: /etc/aralez
|
||||
proxy_tls_grade: high
|
||||
upstreams_conf: /etc/aralez/upstreams.yml
|
||||
log_level: info
|
||||
hc_method: HEAD
|
||||
hc_interval: 2
|
||||
@@ -0,0 +1,22 @@
|
||||
apiVersion: apps/v1
|
||||
kind: Deployment
|
||||
metadata:
|
||||
name: svc-nginx
|
||||
namespace: upstreams
|
||||
labels:
|
||||
app: svc-nginx
|
||||
spec:
|
||||
selector:
|
||||
matchLabels:
|
||||
app: svc-nginx
|
||||
replicas: 3
|
||||
template:
|
||||
metadata:
|
||||
labels:
|
||||
app: svc-nginx
|
||||
spec:
|
||||
containers:
|
||||
- name: svc-nginx
|
||||
image: nginx:latest
|
||||
ports:
|
||||
- containerPort: 80
|
||||
@@ -0,0 +1,12 @@
|
||||
apiVersion: v1
|
||||
kind: Service
|
||||
metadata:
|
||||
name: svc-nginx
|
||||
namespace: upstreams
|
||||
spec:
|
||||
selector:
|
||||
app: svc-nginx
|
||||
ports:
|
||||
- protocol: TCP
|
||||
port: 80
|
||||
targetPort: 80
|
||||
@@ -0,0 +1,12 @@
|
||||
apiVersion: v1
|
||||
kind: Service
|
||||
metadata:
|
||||
name: api-service-v2
|
||||
namespace: upstreams
|
||||
spec:
|
||||
selector:
|
||||
app: svc-nginx
|
||||
ports:
|
||||
- protocol: TCP
|
||||
port: 80
|
||||
targetPort: 80
|
||||
@@ -0,0 +1,40 @@
|
||||
apiVersion: v1
|
||||
kind: ServiceAccount
|
||||
metadata:
|
||||
name: aralez-sa
|
||||
namespace: aralez
|
||||
---
|
||||
apiVersion: rbac.authorization.k8s.io/v1
|
||||
kind: ClusterRole
|
||||
metadata:
|
||||
name: aralez-role
|
||||
rules:
|
||||
# Watch Ingresses and IngressClasses across all namespaces
|
||||
- apiGroups: ["networking.k8s.io"]
|
||||
resources: ["ingresses", "ingressclasses"]
|
||||
verbs: ["get", "list", "watch"]
|
||||
# Update Ingress status (for setting load balancer IPs)
|
||||
- apiGroups: ["networking.k8s.io"]
|
||||
resources: ["ingresses/status"]
|
||||
verbs: ["update", "patch"]
|
||||
# Watch Services and Endpoints across all namespaces
|
||||
- apiGroups: [""]
|
||||
resources: ["services", "endpoints"]
|
||||
verbs: ["get", "list", "watch"]
|
||||
# Watch EndpointSlices across all namespaces
|
||||
- apiGroups: ["discovery.k8s.io"]
|
||||
resources: ["endpointslices"]
|
||||
verbs: ["get", "list", "watch"]
|
||||
---
|
||||
apiVersion: rbac.authorization.k8s.io/v1
|
||||
kind: ClusterRoleBinding
|
||||
metadata:
|
||||
name: aralez-ingress
|
||||
subjects:
|
||||
- kind: ServiceAccount
|
||||
name: aralez-sa
|
||||
namespace: aralez # <--- MUST match where Aralez is deployed
|
||||
roleRef:
|
||||
kind: ClusterRole
|
||||
name: aralez-role
|
||||
apiGroup: rbac.authorization.k8s.io
|
||||
@@ -0,0 +1,16 @@
|
||||
provider: "kubernetes"
|
||||
to_https: false
|
||||
sticky_sessions: 86000
|
||||
rate_limit: 100
|
||||
x4xx_limit: 100
|
||||
headers:
|
||||
- "Access-Control-Allow-Origin:*"
|
||||
- "Access-Control-Allow-Methods:POST, GET, OPTIONS"
|
||||
- "Access-Control-Max-Age:86400"
|
||||
- "Strict-Transport-Security:max-age=31536000; includeSubDomains; preload"
|
||||
kubernetes:
|
||||
services:
|
||||
- hostname: "svc-nginx"
|
||||
upstream: "svc-nginx"
|
||||
path: "/"
|
||||
tokenpath: "/var/run/secrets/kubernetes.io/serviceaccount/token"
|
||||
+15
-10
@@ -2,21 +2,26 @@
|
||||
threads: 12 # Number of daemon threads default setting
|
||||
runuser: aralez # Username for running aralez after dropping root privileges, requires program to start as root
|
||||
rungroup: aralez # Group for running aralez after dropping root privileges, requires program to start as root
|
||||
daemon: false # Run in background
|
||||
upstream_keepalive_pool_size: 500 # Pool size for upstream keepalive connections
|
||||
pid_file: /tmp/aralez.pid # Path to PID file
|
||||
error_log: /tmp/aralez_err.log # Path to error log
|
||||
upgrade_sock: /tmp/aralez.sock # Path to socket file
|
||||
config_api_enabled: true # Boolean to enable/disable remote config push capability.
|
||||
config_address: 0.0.0.0:3000 # HTTP API address for pushing upstreams.yaml from remote location
|
||||
proxy_address_http: 0.0.0.0:6193 # Proxy HTTP bind address
|
||||
proxy_address_tls: 0.0.0.0:6194 # Optional, Proxy TLS bind address
|
||||
proxy_configs: /opt/aralez/etc # Mandatory if proxy_address_tls set, should contain a certificate and key files strictly in a format {NAME}.crt, {NAME}.key.
|
||||
proxy_tls_grade: a+ # Grade of TLS suite for proxy (a+, a, b, c, unsafe), matching grades of Qualys SSL Labs
|
||||
config_address: 127.0.0.1:3000 # HTTP API address for pushing upstreams.yaml from remote location
|
||||
proxy_address_http: 0.0.0.0:80 # Proxy HTTP bind address
|
||||
proxy_address_tls: 0.0.0.0:443 # Optional, Proxy TLS bind address
|
||||
proxy_configs: /opt/aralez/asyncweb/etc # Mandatory if proxy_address_tls set, should contain a certificate and key files strictly in a format {NAME}.crt, {NAME}.key.
|
||||
proxy_tls_grade: high # Grade of TLS suite for proxy (high, medium, unsafe), matching grades of Qualys SSL Labs
|
||||
upstreams_conf: /opt/aralez/etc/upstreams.yaml # the location of upstreams file
|
||||
file_server_folder: /opt/storage # Optional, local folder to serve
|
||||
file_server_address: 127.0.0.1:3002 # Optional, Local address for file server. Can set as upstream for public access.
|
||||
file_server_folder: /opt/aralez/public # Optional, local folder to serve
|
||||
file_server_address: 0.0.0.0:3002 # Optional, Local address for file server. Can set as upstream for public access.
|
||||
log_level: info # info, warn, error, debug, trace, off
|
||||
log_file: /tmp/aralez.log, 20, 5, compress # Optional, the location of log file, file size in megabytes, number of log files to keep, compress files .valueas are separated by comma.
|
||||
access_log: error # all, error, (Off if commented)
|
||||
hc_method: HEAD # Healthcheck method (HEAD, GET, POST are supported) UPPERCASE
|
||||
hc_interval: 2 #Interval for health checks in seconds
|
||||
master_key: 910517d9-f9a1-48de-8826-dbadacbd84af-cb6f830e-ab16-47ec-9d8f-0090de732774 # Mater key for working with API server and JWT Secret
|
||||
tcp_keepalive_idle: 60 # Seconds of inactivity before the kernel starts sending keepalive probes to a downstream client
|
||||
tcp_keepalive_interval: 10 # Seconds between individual keepalive probes if the client does not respond
|
||||
tcp_keepalive_count: 5 # Number of unanswered probes before the kernel declares the connection dead and closes it
|
||||
cache_size_mb: 50 # Optional. Enable internal cache with size in megabytes of value. Cache is entirely disabled when this line is commented out
|
||||
cache_ttl: 120 # Optional. Set Default TTL in seconds for cached items, works if cache control headers are not set via upstream. Defaults to 60 if cache_size_mb is set
|
||||
|
||||
|
||||
@@ -1,19 +0,0 @@
|
||||
provider: "file"
|
||||
globals:
|
||||
headers:
|
||||
- "Access-Control-Allow-Origin:*"
|
||||
- "Access-Control-Allow-Methods:POST, GET, OPTIONS"
|
||||
- "Access-Control-Max-Age:86400"
|
||||
- "X-Custom-Header:Something Special"
|
||||
upstreams:
|
||||
myip.netangels.net:
|
||||
paths:
|
||||
"/":
|
||||
ssl: false
|
||||
headers:
|
||||
- "X-Proxy-From:Aralez"
|
||||
servers:
|
||||
- "192.168.221.213:8000"
|
||||
- "192.168.221.214:8000"
|
||||
- "192.168.221.210:8000"
|
||||
- "192.168.221.212:8000"
|
||||
+84
-66
@@ -1,48 +1,44 @@
|
||||
# The file under watch and hot reload, changes are applied immediately, no need to restart or reload.
|
||||
provider: "file" # "file" "consul" "kubernetes"
|
||||
sticky_sessions: false
|
||||
sticky_sessions: 172000
|
||||
to_https: false
|
||||
rate_limit: 100
|
||||
rate_limit: 500000
|
||||
x4xx_limit: 100000
|
||||
server_headers:
|
||||
- "X-Forwarded-Proto:https"
|
||||
- "X-Forwarded-Port:443"
|
||||
- "Y-Global-Something: Something For Servers"
|
||||
client_headers:
|
||||
- "Access-Control-Allow-Origin:*"
|
||||
- "Access-Control-Allow-Methods:POST, GET, OPTIONS"
|
||||
- "Access-Control-Max-Age:86400"
|
||||
- "X-Global-Something: Something For Clients"
|
||||
#authorization:
|
||||
# type: "jwt"
|
||||
# creds: "910517d9-f9a1-48de-8826-dbadacbd84af-cb6f830e-ab16-47ec-9d8f-0090de732774"
|
||||
# type: "basic"
|
||||
# creds: "username:Pa$$w0rd"
|
||||
# type: "apikey"
|
||||
# creds: "5ecbf799-1343-4e94-a9b5-e278af5cd313-56b45249-1839-4008-a450-a60dc76d2bae"
|
||||
# data: "root:toor"
|
||||
# type: "jwt"
|
||||
# data: "910517d9-f9a1-48de-8826-dbadacbd84af-cb6f830e-ab16-47ec-9d8f-0090de732774"
|
||||
# type: "apikey"
|
||||
# data: "5ecbf799-1343-4e94-a9b5-e278af5cd313-56b45249-1839-4008-a450-a60dc76d2bae"
|
||||
consul:
|
||||
servers:
|
||||
- "http://192.168.1.199:8500"
|
||||
- "http://192.168.1.200:8500"
|
||||
- "http://192.168.1.201:8500"
|
||||
- "http://consul1:8500"
|
||||
services: # hostname: The hostname to access the proxy server, upstream : The real service name in Consul database.
|
||||
- hostname: "webapi-service"
|
||||
upstream: "webapi-service-health"
|
||||
- hostname: "nconsul"
|
||||
upstream: "nginx-consul-NginX-health"
|
||||
path: "/one"
|
||||
client_headers:
|
||||
- "X-Some-Thing:Yaaaaaaaaaaaaaaa"
|
||||
- "X-Proxy-From:Aralez"
|
||||
rate_limit: 1
|
||||
to_https: false
|
||||
- hostname: "webapi-service"
|
||||
upstream: "webapi-service-health"
|
||||
- hostname: "nconsul"
|
||||
upstream: "nginx-consul-NginX-health"
|
||||
path: "/"
|
||||
token: "8e2db809-845b-45e1-8b47-2c8356a09da0-a4370955-18c2-4d6e-a8f8-ffcc0b47be81" # Consul server access token, If Consul auth is enabled
|
||||
kubernetes:
|
||||
servers:
|
||||
- "192.168.1.55:443" #For testing only, overrides with KUBERNETES_SERVICE_HOST : KUBERNETES_SERVICE_PORT_HTTPS env variables.
|
||||
- "172.16.0.11:5443" # Gets KUBERNETES_SERVICE_HOST : KUBERNETES_SERVICE_PORT_HTTPS env variables.
|
||||
services:
|
||||
- hostname: "webapi-service"
|
||||
- hostname: "api-service"
|
||||
upstream: "api-service"
|
||||
path: "/"
|
||||
upstream: "webapi-service"
|
||||
- hostname: "webapi-service"
|
||||
- hostname: "api-service"
|
||||
upstream: "console-service"
|
||||
path: "/one"
|
||||
client_headers:
|
||||
@@ -50,70 +46,92 @@ kubernetes:
|
||||
- "X-Proxy-From:Aralez"
|
||||
rate_limit: 100
|
||||
to_https: false
|
||||
- hostname: "webapi-service"
|
||||
upstream: "rambul-service"
|
||||
- hostname: "api-service"
|
||||
upstream: "feed-fanout-service"
|
||||
path: "/two"
|
||||
- hostname: "websocket-service"
|
||||
upstream: "websocket-service"
|
||||
path: "/"
|
||||
tokenpath: "/path/to/kubetoken.txt" #If not set, will default to /var/run/secrets/kubernetes.io/serviceaccount/token
|
||||
tokenpath: "/opt/Rust/Projects/asyncweb/etc/kubetoken.txt" # Defaults to /var/run/secrets/kubernetes.io/serviceaccount/token
|
||||
upstreams:
|
||||
myip.mydomain.com:
|
||||
www.example.com:
|
||||
paths:
|
||||
"/":
|
||||
rate_limit: 200
|
||||
rate_limit: 50
|
||||
x4xx_limit: 100
|
||||
to_https: false
|
||||
client_headers:
|
||||
- "X-Proxy-From:Aralez"
|
||||
servers:
|
||||
- "127.0.0.1:8000"
|
||||
- "127.0.0.2:8000"
|
||||
- "127.0.0.3:8000"
|
||||
- "127.0.0.4:8000"
|
||||
- "127.0.0.5:8000"
|
||||
"/ping":
|
||||
authorization: # Will be ignored if global authentication is enabled.
|
||||
authorization:
|
||||
type: "basic"
|
||||
creds: "admin:admin"
|
||||
to_https: false
|
||||
data: "root:toor"
|
||||
server_headers:
|
||||
- "X-Forwarded-Proto:https"
|
||||
- "X-Forwarded-Port:443"
|
||||
- "Y-Proxy-Server-Some:Yaaaaaaaaaaaaaaa"
|
||||
- "Y-Proxy-Server-From:Aralez"
|
||||
- "Y-Proxy-Server-Vers:Aralez v-xxx"
|
||||
client_headers:
|
||||
- "X-Some-Thing:Yaaaaaaaaaaaaaaa"
|
||||
- "X-Proxy-From:Aralez"
|
||||
- "Access-Control-Allow-Origin:*"
|
||||
- "Access-Control-Allow-Methods:POST, GET, OPTIONS"
|
||||
- "Access-Control-Max-Age:86400"
|
||||
- "Strict-Transport-Security:max-age=31536000; includeSubDomains; preload"
|
||||
servers:
|
||||
- "127.0.0.1:8000"
|
||||
- "127.0.0.2:8000"
|
||||
"/draw":
|
||||
servers:
|
||||
- "192.168.1.1:8000"
|
||||
polo.mydomain.com:
|
||||
paths:
|
||||
"/":
|
||||
to_https: false
|
||||
client_headers:
|
||||
- "X-Some-Thing:Yaaaaaaaaaaaaaaa"
|
||||
servers:
|
||||
- "192.168.1.1:8000"
|
||||
- "192.168.1.10:8000"
|
||||
- "127.0.0.1:8000"
|
||||
- "127.0.0.2:8000"
|
||||
- "127.0.0.3:8000"
|
||||
- "127.0.0.4:8000"
|
||||
apt.mydomain.com:
|
||||
"/ping":
|
||||
to_https: true
|
||||
client_headers:
|
||||
- "X-Some-Thing:Something Else"
|
||||
- "Access-Control-Allow-Origin:*"
|
||||
- "Access-Control-Allow-Methods:POST, GET, OPTIONS"
|
||||
- "Access-Control-Max-Age:86400"
|
||||
- "Strict-Transport-Security:max-age=31536000; includeSubDomains; preload"
|
||||
servers:
|
||||
- "127.0.0.1:8000"
|
||||
"/secret":
|
||||
authorization:
|
||||
type: "forward"
|
||||
data: "http://127.0.0.1:8899/admin/login"
|
||||
servers:
|
||||
- "127.0.0.10:8000"
|
||||
example.com:
|
||||
paths:
|
||||
"/":
|
||||
redirect_to: "https://www.example.com:443"
|
||||
servers:
|
||||
- "192.168.1.10:443"
|
||||
- "127.0.0.1:80"
|
||||
h2.example.com:
|
||||
paths:
|
||||
"/":
|
||||
server_headers:
|
||||
- "Y-Global-Something: Yes this is something"
|
||||
client_headers:
|
||||
- "Access-Control-Allow-Methods:POST, GET, OPTIONS"
|
||||
rate_limit: 60
|
||||
x4xx_limit: 30
|
||||
authorization:
|
||||
type: "jwt"
|
||||
servers:
|
||||
- "127.0.0.1:8000"
|
||||
- "127.0.0.2:8000"
|
||||
"/.well-known/acme-challenge":
|
||||
healthcheck: false
|
||||
servers:
|
||||
- "127.0.0.1:8001"
|
||||
rdr.mydomain.com:
|
||||
paths:
|
||||
"/":
|
||||
redirect_to: "https://som.other.domain:6194"
|
||||
"/400":
|
||||
rate_limit: 4
|
||||
x4xx_limit: 2
|
||||
servers:
|
||||
- "127.0.0.1:8899"
|
||||
"/500":
|
||||
healthcheck: false
|
||||
servers:
|
||||
- "127.0.0.1:8080"
|
||||
- "127.0.0.1:8899"
|
||||
DEFAULT:
|
||||
paths:
|
||||
"/":
|
||||
healthcheck: false
|
||||
servers:
|
||||
- "127.0.0.1:3000"
|
||||
"/.well-known/acme-challenge":
|
||||
healthcheck: false
|
||||
servers:
|
||||
- "127.0.0.1:3000"
|
||||
|
||||
@@ -7,5 +7,10 @@ static GLOBAL: mimalloc::MiMalloc = mimalloc::MiMalloc;
|
||||
// pub static A: CountingAllocator = CountingAllocator;
|
||||
|
||||
fn main() {
|
||||
if std::env::args().any(|a| a == "--version" || a == "-v") {
|
||||
println!("aralez {}", env!("CARGO_PKG_VERSION"));
|
||||
std::process::exit(0);
|
||||
}
|
||||
|
||||
web::start::run();
|
||||
}
|
||||
|
||||
@@ -1,17 +1,14 @@
|
||||
use crate::tls::acme::account::get_account;
|
||||
use crate::utils::lazylock::CHALLENGES;
|
||||
use crate::utils::parceyaml::DOMAINS;
|
||||
use instant_acme::{ChallengeType, Identifier, NewOrder, RetryPolicy};
|
||||
use log::{error, info};
|
||||
use pingora::prelude::sleep;
|
||||
use rcgen::{CertificateParams, DistinguishedName, KeyPair};
|
||||
use std::collections::HashMap;
|
||||
use std::fs;
|
||||
use std::sync::{LazyLock, RwLock};
|
||||
use std::time::Duration;
|
||||
use x509_parser::prelude::*;
|
||||
|
||||
pub static CHALLENGES: LazyLock<RwLock<HashMap<String, String>>> = LazyLock::new(|| RwLock::new(HashMap::new()));
|
||||
|
||||
pub async fn refresh_order(certs_dir: String, autoconf_dir: String) {
|
||||
let credsfile = autoconf_dir + "/acme_credentials.json";
|
||||
loop {
|
||||
|
||||
+6
-1
@@ -1,14 +1,19 @@
|
||||
pub mod auth;
|
||||
pub mod consul;
|
||||
pub mod discovery;
|
||||
mod filewatch;
|
||||
pub mod fordebug;
|
||||
pub mod grpc;
|
||||
pub mod hcclient;
|
||||
pub mod healthcheck;
|
||||
pub mod httpclient;
|
||||
pub mod jwt;
|
||||
pub mod kuberconsul;
|
||||
pub mod kubernetes;
|
||||
pub mod kubewatcher;
|
||||
pub mod lazylock;
|
||||
pub mod metrics;
|
||||
pub mod parceyaml;
|
||||
pub mod state;
|
||||
pub mod structs;
|
||||
pub mod tools;
|
||||
// pub mod watchksecret;
|
||||
|
||||
+20
-19
@@ -1,5 +1,6 @@
|
||||
use crate::utils::jwt::{check_jwt, JWT_TOKEN};
|
||||
use crate::utils::structs::InnerAuth;
|
||||
pub(crate) use crate::utils::tools::split_host_port;
|
||||
use axum::http::StatusCode;
|
||||
use base64::engine::general_purpose::STANDARD;
|
||||
use base64::Engine;
|
||||
@@ -224,22 +225,22 @@ pub fn get_query_param(session: &mut Session, key: &str) -> Option<String> {
|
||||
params.get(key).and_then(|v| decode(v).ok()).map(|s| s.to_string())
|
||||
}
|
||||
|
||||
#[allow(clippy::needless_return)]
|
||||
fn split_host_port(addr: &str, tls: bool) -> Option<(&str, u16, bool, &str)> {
|
||||
match addr.split_once(':') {
|
||||
Some((h, p)) => match p.parse::<u16>() {
|
||||
Ok(port) => return Some((h, port, tls, h)),
|
||||
Err(_) => {
|
||||
log::warn!("ForwardAuth: invalid port in {}", addr);
|
||||
return None;
|
||||
}
|
||||
},
|
||||
None => {
|
||||
if tls {
|
||||
return Some((addr, 443u16, tls, addr));
|
||||
} else {
|
||||
return Some((addr, 80u16, tls, addr));
|
||||
}
|
||||
}
|
||||
};
|
||||
}
|
||||
// #[allow(clippy::needless_return)]
|
||||
// pub fn split_host_port(addr: &str, tls: bool) -> Option<(&str, u16, bool, &str)> {
|
||||
// match addr.split_once(':') {
|
||||
// Some((h, p)) => match p.parse::<u16>() {
|
||||
// Ok(port) => return Some((h, port, tls, h)),
|
||||
// Err(_) => {
|
||||
// log::warn!("ForwardAuth: invalid port in {}", addr);
|
||||
// return None;
|
||||
// }
|
||||
// },
|
||||
// None => {
|
||||
// if tls {
|
||||
// return Some((addr, 443u16, tls, addr));
|
||||
// } else {
|
||||
// return Some((addr, 80u16, tls, addr));
|
||||
// }
|
||||
// }
|
||||
// };
|
||||
// }
|
||||
|
||||
@@ -0,0 +1,91 @@
|
||||
use crate::utils::httpclient;
|
||||
use crate::utils::kuberconsul::{list_to_upstreams, ServiceDiscovery};
|
||||
use crate::utils::parceyaml::build_headers;
|
||||
use crate::utils::structs::{Configuration, GlobalServiceMapping, UpstreamsDashMap};
|
||||
use async_trait::async_trait;
|
||||
use dashmap::DashMap;
|
||||
use pingora::prelude::sleep;
|
||||
use rand::RngExt;
|
||||
use serde::Deserialize;
|
||||
use std::env;
|
||||
use std::sync::Arc;
|
||||
use std::time::Duration;
|
||||
use tokio::sync::mpsc::Sender;
|
||||
|
||||
#[derive(Debug, Deserialize)]
|
||||
pub struct ConsulService {
|
||||
#[serde(rename = "Address")]
|
||||
pub address: String,
|
||||
#[serde(rename = "ServicePort")]
|
||||
pub port: u16,
|
||||
}
|
||||
pub struct ConsulDiscovery;
|
||||
|
||||
#[async_trait]
|
||||
impl ServiceDiscovery for ConsulDiscovery {
|
||||
async fn fetch_upstreams(&self, config: Arc<Configuration>, toreturn: Sender<Configuration>) {
|
||||
loop {
|
||||
let upstreams = UpstreamsDashMap::new();
|
||||
|
||||
if let Some(consul) = config.consul.clone() {
|
||||
let servers = consul.servers.unwrap_or_else(|| {
|
||||
vec![format!(
|
||||
"{}:{}",
|
||||
env::var("CONSUL_SERVICE_HOST").unwrap_or_else(|_| "0.0.0.0".to_string()),
|
||||
env::var("CONSUL_SERVICE_PORT").unwrap_or_else(|_| "0".to_string())
|
||||
)]
|
||||
});
|
||||
let end = servers.len().saturating_sub(1);
|
||||
let num = if end > 0 { rand::rng().random_range(0..end) } else { 0 };
|
||||
let consul_data = servers.get(num).unwrap().to_string();
|
||||
let ss = format!("{}/v1/catalog/service/", consul_data);
|
||||
let dc = format!("{}/v1/catalog/services?filter=%22aralez.service=yes%22+in+ServiceTags", consul_data);
|
||||
|
||||
if let Some(infolist) = httpclient::for_consul_list(dc.as_str(), consul.token.clone()).await {
|
||||
for (k, v) in infolist {
|
||||
let client_header_map: DashMap<Arc<str>, Vec<(String, Arc<str>)>> = DashMap::new();
|
||||
let mut client_header_list = Vec::new();
|
||||
build_headers(&v.client_headers, config.as_ref(), &mut client_header_list);
|
||||
|
||||
let sever_header_map: DashMap<Arc<str>, Vec<(String, Arc<str>)>> = DashMap::new();
|
||||
let mut server_header_list = Vec::new();
|
||||
build_headers(&v.server_headers, config.as_ref(), &mut server_header_list);
|
||||
|
||||
if !client_header_list.is_empty() {
|
||||
let path_key = v.path.clone();
|
||||
client_header_map.insert(Arc::from(path_key), client_header_list);
|
||||
config.client_headers.insert(Arc::from(v.host.clone()), client_header_map);
|
||||
}
|
||||
if !server_header_list.is_empty() {
|
||||
let path_key = v.path.clone();
|
||||
sever_header_map.insert(Arc::from(path_key), server_header_list);
|
||||
config.server_headers.insert(Arc::from(v.host.clone()), sever_header_map);
|
||||
}
|
||||
let pref = format!("{}{}", ss, k);
|
||||
let gsm = &GlobalServiceMapping {
|
||||
upstream: k.clone(),
|
||||
hostname: v.host.clone(),
|
||||
path: Some(v.path),
|
||||
to_https: v.to_https,
|
||||
redirect_to: v.redirect,
|
||||
authorization: v.auth,
|
||||
rate_limit: v.rate,
|
||||
x4xx_limit: v.xrate,
|
||||
client_headers: v.client_headers,
|
||||
server_headers: v.server_headers,
|
||||
};
|
||||
|
||||
let list = httpclient::for_consul(pref.as_str(), consul.token.clone(), gsm).await;
|
||||
list_to_upstreams(list, &upstreams, gsm);
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
if let Some(lt) = crate::utils::kuberconsul::clone_compare(&upstreams, &config).await {
|
||||
let _ = toreturn.send(lt).await;
|
||||
}
|
||||
|
||||
sleep(Duration::from_secs(5)).await;
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -1,10 +1,12 @@
|
||||
use crate::utils::consul::ConsulDiscovery;
|
||||
use crate::utils::filewatch;
|
||||
use crate::utils::kuberconsul::{ConsulDiscovery, KubernetesDiscovery, ServiceDiscovery};
|
||||
use crate::utils::kuberconsul::ServiceDiscovery;
|
||||
use crate::utils::kubernetes::KubernetesDiscovery;
|
||||
use crate::utils::structs::{Configuration, UpstreamsDashMap};
|
||||
use crate::web::webserver;
|
||||
use async_trait::async_trait;
|
||||
use futures::channel::mpsc::Sender;
|
||||
use std::sync::Arc;
|
||||
use tokio::sync::mpsc::Sender;
|
||||
|
||||
pub struct APIUpstreamProvider {
|
||||
pub config_api_enabled: bool,
|
||||
@@ -46,7 +48,7 @@ impl Discovery for APIUpstreamProvider {
|
||||
#[async_trait]
|
||||
impl Discovery for FromFileProvider {
|
||||
async fn start(&self, tx: Sender<Configuration>) {
|
||||
tokio::spawn(filewatch::start(self.path.clone(), tx.clone()));
|
||||
tokio::spawn(filewatch::start(self.path.clone(), tx));
|
||||
}
|
||||
}
|
||||
|
||||
|
||||
@@ -1,16 +1,15 @@
|
||||
use crate::utils::parceyaml::load_configuration;
|
||||
use crate::utils::structs::Configuration;
|
||||
use futures::channel::mpsc::Sender;
|
||||
use futures::SinkExt;
|
||||
use log::error;
|
||||
use notify::event::ModifyKind;
|
||||
use notify::{Config, Event, EventKind, RecommendedWatcher, RecursiveMode, Watcher};
|
||||
use pingora::prelude::sleep;
|
||||
use std::path::Path;
|
||||
use std::time::{Duration, Instant};
|
||||
use tokio::sync::mpsc::Sender;
|
||||
use tokio::task;
|
||||
|
||||
pub async fn start(fp: String, mut toreturn: Sender<Configuration>) {
|
||||
pub async fn start(fp: String, toreturn: Sender<Configuration>) {
|
||||
sleep(Duration::from_millis(50)).await; // For having nice logs :-)
|
||||
let file_path = fp.as_str();
|
||||
let parent_dir = Path::new(file_path).parent().unwrap();
|
||||
@@ -37,9 +36,8 @@ pub async fn start(fp: String, mut toreturn: Sender<Configuration>) {
|
||||
match event {
|
||||
Ok(e) => match e.kind {
|
||||
EventKind::Modify(ModifyKind::Data(_)) | EventKind::Create(..) | EventKind::Remove(..) => {
|
||||
if e.paths[0].to_str().unwrap().ends_with("yaml") && start.elapsed() > Duration::from_secs(2) {
|
||||
if start.elapsed() > Duration::from_secs(2) {
|
||||
start = Instant::now();
|
||||
// info!("Config File changed :=> {:?}", e);
|
||||
let snd = load_configuration(file_path, "filepath").await.0;
|
||||
if let Some(snd) = snd {
|
||||
toreturn.send(snd).await.unwrap();
|
||||
|
||||
@@ -0,0 +1,23 @@
|
||||
use bytes::Bytes;
|
||||
use http_body_util::Full;
|
||||
use hyper::Request;
|
||||
use hyper_util::client::legacy::connect::HttpConnector;
|
||||
use hyper_util::client::legacy::Client;
|
||||
use hyper_util::rt::TokioExecutor;
|
||||
|
||||
pub async fn ping_grpc(addr: &str) -> bool {
|
||||
let connector = HttpConnector::new();
|
||||
let client = Client::builder(TokioExecutor::new()).http2_only(true).build(connector);
|
||||
let uri = format!("{}{}", addr, "/aralez.Probe/Ping");
|
||||
let body = Full::new(Bytes::from(vec![0, 0, 0, 0, 0]));
|
||||
let request = Request::post(uri).header("content-type", "application/grpc").header("te", "trailers").body(body).unwrap();
|
||||
match client.request(request).await {
|
||||
Ok(resp) => resp
|
||||
.headers()
|
||||
.get("content-type")
|
||||
.and_then(|v| v.to_str().ok())
|
||||
.map(|v| v.starts_with("application/grpc"))
|
||||
.unwrap_or(false),
|
||||
Err(_) => false,
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,95 @@
|
||||
use crate::utils::grpc::ping_grpc;
|
||||
use bytes::Bytes;
|
||||
use pingora_core::connectors::http::Connector;
|
||||
use pingora_core::listeners::ALPN;
|
||||
use pingora_core::prelude::HttpPeer;
|
||||
use pingora_http::RequestHeader;
|
||||
use std::sync::LazyLock;
|
||||
use std::time::Duration;
|
||||
|
||||
pub static HC_CONNECTOR: LazyLock<Connector> = LazyLock::new(|| Connector::new(None));
|
||||
|
||||
pub async fn httpclient(method: &str, tls: bool, host: &str, path: &str, address: &str, port: u16, url: String) -> (bool, bool) {
|
||||
let method = match method {
|
||||
"HEAD" => "HEAD",
|
||||
"GET" => "GET",
|
||||
"POST" => "POST",
|
||||
_ => "GET",
|
||||
};
|
||||
|
||||
let mut peer = HttpPeer::new((address, port), tls, host.to_string());
|
||||
|
||||
if tls {
|
||||
peer.options.verify_cert = false;
|
||||
peer.options.verify_hostname = false;
|
||||
}
|
||||
|
||||
let mut is_h2 = false;
|
||||
peer.options.total_connection_timeout = Option::from(Duration::from_secs(5));
|
||||
peer.options.alpn = ALPN::H2H1;
|
||||
let (mut http_session, _) = match HC_CONNECTOR.get_http_session(&peer).await {
|
||||
Ok(s) => s,
|
||||
Err(e) => {
|
||||
if let Some(msg) = e.context {
|
||||
log::warn!("{}, type: {}", msg.as_str(), e.etype.as_str());
|
||||
} else {
|
||||
log::warn!("Fail to connect to addr: {}, tls {}, host {}", address, tls, host);
|
||||
}
|
||||
return (false, false);
|
||||
}
|
||||
};
|
||||
|
||||
match http_session.as_http2() {
|
||||
Some(_) => {
|
||||
peer.options.alpn = ALPN::H2;
|
||||
is_h2 = true;
|
||||
}
|
||||
None => {
|
||||
if ping_grpc(url.as_str()).await {
|
||||
return (true, true);
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
let mut req = match RequestHeader::build(method, path.as_bytes(), None) {
|
||||
Ok(r) => r,
|
||||
Err(e) => {
|
||||
log::warn!("Failed to build request: {}", e);
|
||||
return (false, false);
|
||||
}
|
||||
};
|
||||
|
||||
req.insert_header("Host", host).ok();
|
||||
|
||||
if let Err(e) = http_session.write_request_header(Box::new(req)).await {
|
||||
log::warn!("Write header failed: {}", e);
|
||||
return (false, false);
|
||||
}
|
||||
|
||||
let status = if is_h2 {
|
||||
if let Err(e) = http_session.write_request_body(Bytes::new(), true).await {
|
||||
log::warn!("Write body failed: {}", e);
|
||||
return (false, false);
|
||||
}
|
||||
match http_session.read_response_header().await {
|
||||
Ok(_) => http_session.response_header().map(|r| r.status.as_u16()).unwrap_or(500),
|
||||
Err(e) => {
|
||||
if ping_grpc(url.as_str()).await {
|
||||
return (true, true);
|
||||
}
|
||||
log::warn!("Health Check H2 read failed: {} - {}", host, e);
|
||||
return (false, false);
|
||||
}
|
||||
}
|
||||
} else {
|
||||
match http_session.read_response_header().await {
|
||||
Ok(_) => http_session.response_header().map(|r| r.status.as_u16()).unwrap_or(500),
|
||||
Err(e) => {
|
||||
log::warn!("Health Check H1 read failed: {} - {}", e, host);
|
||||
return (false, false);
|
||||
}
|
||||
}
|
||||
};
|
||||
HC_CONNECTOR.release_http_session(http_session, &peer, None).await;
|
||||
((200..500).contains(&status), is_h2)
|
||||
}
|
||||
+35
-81
@@ -1,47 +1,36 @@
|
||||
use crate::utils::hcclient::httpclient;
|
||||
use crate::utils::lazylock::REVERSE_STORE;
|
||||
use crate::utils::structs::{InnerMap, UpstreamsDashMap, UpstreamsIdMap};
|
||||
use crate::utils::tools::*;
|
||||
use dashmap::DashMap;
|
||||
use log::{error, warn};
|
||||
use reqwest::{Client, Version};
|
||||
use std::sync::atomic::AtomicUsize;
|
||||
use std::sync::Arc;
|
||||
use std::time::Duration;
|
||||
use tokio::time::interval;
|
||||
use tonic::transport::Endpoint;
|
||||
use tokio::net::TcpStream;
|
||||
use tokio::time::{interval, timeout};
|
||||
use tokio_native_tls::native_tls::TlsConnector;
|
||||
|
||||
pub async fn hc2(upslist: Arc<UpstreamsDashMap>, fullist: Arc<UpstreamsDashMap>, idlist: Arc<UpstreamsIdMap>, params: (&str, u64)) {
|
||||
let mut period = interval(Duration::from_secs(params.1));
|
||||
let client = Client::builder().timeout(Duration::from_secs(params.1)).danger_accept_invalid_certs(true).build().unwrap();
|
||||
loop {
|
||||
tokio::select! {
|
||||
_ = period.tick() => {
|
||||
// populate_upstreams(&upslist, &fullist, &idlist, params, &client).await;
|
||||
let totest = build_upstreams(&fullist, params.0, &client).await;
|
||||
let totest = build_upstreams(&fullist, params.0).await;
|
||||
if !compare_dashmaps(&totest, &upslist) {
|
||||
clone_dashmap_into(&totest, &upslist);
|
||||
clone_idmap_into(&totest, &idlist);
|
||||
REVERSE_STORE.clear();
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
/*
|
||||
pub async fn populate_upstreams(upslist: &Arc<UpstreamsDashMap>, fullist: &Arc<UpstreamsDashMap>, idlist: &Arc<UpstreamsIdMap>, params: (&str, u64), client: &Client) {
|
||||
let totest = build_upstreams(fullist, params.0, client).await;
|
||||
if !compare_dashmaps(&totest, upslist) {
|
||||
clone_dashmap_into(&totest, upslist);
|
||||
clone_idmap_into(&totest, idlist);
|
||||
}
|
||||
}
|
||||
*/
|
||||
|
||||
pub async fn initiate_upstreams(fullist: UpstreamsDashMap) -> UpstreamsDashMap {
|
||||
let client = Client::builder().timeout(Duration::from_secs(2)).danger_accept_invalid_certs(true).build().unwrap();
|
||||
build_upstreams(&fullist, "HEAD", &client).await
|
||||
build_upstreams(&fullist, "HEAD").await
|
||||
}
|
||||
|
||||
async fn build_upstreams(fullist: &UpstreamsDashMap, method: &str, client: &Client) -> UpstreamsDashMap {
|
||||
async fn build_upstreams(fullist: &UpstreamsDashMap, method: &str) -> UpstreamsDashMap {
|
||||
let totest: UpstreamsDashMap = DashMap::new();
|
||||
let fclone = clone_dashmap(fullist);
|
||||
for val in fclone.iter() {
|
||||
@@ -53,20 +42,16 @@ async fn build_upstreams(fullist: &UpstreamsDashMap, method: &str, client: &Clie
|
||||
let mut innervec = Vec::new();
|
||||
|
||||
for upstream in path_entry.value().0.iter() {
|
||||
let tls = detect_tls(upstream.address.as_ref(), &upstream.port, client).await;
|
||||
let is_h2 = matches!(tls.1, Some(Version::HTTP_2));
|
||||
|
||||
let link = if tls.0 {
|
||||
format!("https://{}:{}{}", upstream.address, upstream.port, path)
|
||||
let tls = if upstream.healthcheck.unwrap_or(true) {
|
||||
detect_tls(upstream.address.as_ref(), &upstream.port, host).await
|
||||
} else {
|
||||
format!("http://{}:{}{}", upstream.address, upstream.port, path)
|
||||
false
|
||||
};
|
||||
|
||||
let mut scheme = InnerMap {
|
||||
address: upstream.address.clone(),
|
||||
port: upstream.port,
|
||||
is_ssl: tls.0,
|
||||
is_http2: is_h2,
|
||||
is_ssl: tls,
|
||||
is_http2: false,
|
||||
to_https: upstream.to_https,
|
||||
rate_limit: upstream.rate_limit,
|
||||
x4xx_limit: upstream.x4xx_limit,
|
||||
@@ -76,14 +61,17 @@ async fn build_upstreams(fullist: &UpstreamsDashMap, method: &str, client: &Clie
|
||||
};
|
||||
|
||||
if scheme.healthcheck.unwrap_or(true) {
|
||||
let resp = http_request(&link, method, "", client).await;
|
||||
let link = if tls {
|
||||
format!("https://{}:{}{}", upstream.address, upstream.port, path)
|
||||
} else {
|
||||
format!("http://{}:{}{}", upstream.address, upstream.port, path)
|
||||
};
|
||||
let resp = httpclient(method, tls, host, path, upstream.address.as_ref(), upstream.port, link).await;
|
||||
if resp.0 {
|
||||
if resp.1 {
|
||||
scheme.is_http2 = is_h2; // could be adjusted further
|
||||
scheme.is_http2 = resp.1;
|
||||
}
|
||||
innervec.push(Arc::from(scheme));
|
||||
} else {
|
||||
warn!("Dead Upstream : {}", link);
|
||||
}
|
||||
} else {
|
||||
innervec.push(Arc::from(scheme));
|
||||
@@ -96,54 +84,20 @@ async fn build_upstreams(fullist: &UpstreamsDashMap, method: &str, client: &Clie
|
||||
totest
|
||||
}
|
||||
|
||||
async fn http_request(url: &str, method: &str, payload: &str, client: &Client) -> (bool, bool) {
|
||||
if !["POST", "GET", "HEAD"].contains(&method) {
|
||||
error!("Method {} not supported. Only GET|POST|HEAD are supported ", method);
|
||||
return (false, false);
|
||||
}
|
||||
async fn send_request(client: &Client, method: &str, url: &str, payload: &str) -> Option<reqwest::Response> {
|
||||
match method {
|
||||
"POST" => client.post(url).body(payload.to_owned()).send().await.ok(),
|
||||
"GET" => client.get(url).send().await.ok(),
|
||||
"HEAD" => client.head(url).send().await.ok(),
|
||||
_ => None,
|
||||
}
|
||||
}
|
||||
|
||||
match send_request(client, method, url, payload).await {
|
||||
Some(response) => {
|
||||
let status = response.status().as_u16();
|
||||
((99..499).contains(&status), false)
|
||||
}
|
||||
None => (ping_grpc(url).await, true),
|
||||
}
|
||||
}
|
||||
|
||||
pub async fn ping_grpc(addr: &str) -> bool {
|
||||
let endpoint = match Endpoint::from_shared(addr.to_owned()) {
|
||||
Ok(e) => e.timeout(Duration::from_secs(2)),
|
||||
async fn detect_tls(ip: &str, port: &u16, sni: &str) -> bool {
|
||||
let addr = format!("{ip}:{port}");
|
||||
let timeout_duration = Duration::from_secs(2); // THINK !!!
|
||||
let stream = match timeout(timeout_duration, TcpStream::connect(&addr)).await {
|
||||
Ok(Ok(s)) => s,
|
||||
Ok(Err(_)) => return false,
|
||||
Err(_) => return false,
|
||||
};
|
||||
tokio::time::timeout(Duration::from_secs(3), endpoint.connect()).await.ok().and_then(Result::ok).is_some()
|
||||
}
|
||||
|
||||
async fn detect_tls(ip: &str, port: &u16, client: &Client) -> (bool, Option<Version>) {
|
||||
let https_url = format!("https://{}:{}", ip, port);
|
||||
if let Ok(response) = client.get(&https_url).send().await {
|
||||
return (true, Some(response.version()));
|
||||
}
|
||||
let http_url = format!("http://{}:{}", ip, port);
|
||||
match client.get(&http_url).send().await {
|
||||
Ok(response) => {
|
||||
// println!("{} => {:?} (HTTP)", http_url, response.version());
|
||||
(false, Some(response.version()))
|
||||
}
|
||||
Err(_) => {
|
||||
if ping_grpc(&http_url).await {
|
||||
(false, Some(Version::HTTP_2))
|
||||
} else {
|
||||
(false, None)
|
||||
}
|
||||
}
|
||||
}
|
||||
let connector = tokio_native_tls::TlsConnector::from(
|
||||
TlsConnector::builder()
|
||||
.danger_accept_invalid_certs(true)
|
||||
.danger_accept_invalid_hostnames(true)
|
||||
.build()
|
||||
.unwrap(),
|
||||
);
|
||||
connector.connect(sni, stream).await.is_ok()
|
||||
}
|
||||
|
||||
+226
-67
@@ -1,85 +1,244 @@
|
||||
use crate::utils::kuberconsul::{match_path, ConsulService, KubeEndpoints};
|
||||
use crate::utils::consul::ConsulService;
|
||||
use crate::utils::kuberconsul::match_path;
|
||||
use crate::utils::kubernetes::KubeEndpointSliceList;
|
||||
use crate::utils::structs::{GlobalServiceMapping, InnerMap};
|
||||
use axum::http::{HeaderMap, HeaderValue};
|
||||
use ahash::HashMap;
|
||||
use dashmap::DashMap;
|
||||
use reqwest::Client;
|
||||
use pingora_core::connectors::http::Connector;
|
||||
use pingora_core::listeners::ALPN;
|
||||
use pingora_core::prelude::HttpPeer;
|
||||
use pingora_http::RequestHeader;
|
||||
use serde::{Deserialize, Serialize};
|
||||
use std::sync::atomic::AtomicUsize;
|
||||
use std::sync::Arc;
|
||||
use std::sync::{Arc, LazyLock};
|
||||
use std::time::Duration;
|
||||
|
||||
pub async fn for_consul(url: String, token: Option<String>, conf: &GlobalServiceMapping) -> Option<DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)>> {
|
||||
let client = Client::builder().timeout(Duration::from_secs(2)).danger_accept_invalid_certs(true).build().ok()?;
|
||||
let mut headers = HeaderMap::new();
|
||||
if let Some(token) = token {
|
||||
headers.insert("X-Consul-Token", HeaderValue::from_str(&token).unwrap());
|
||||
}
|
||||
let to = Duration::from_secs(1);
|
||||
let resp = client.get(url).timeout(to).send().await.ok()?;
|
||||
if !resp.status().is_success() {
|
||||
eprintln!("Consul API returned status: {}", resp.status());
|
||||
pub static CONNECTOR: LazyLock<Connector> = LazyLock::new(|| Connector::new(None));
|
||||
|
||||
#[derive(Debug, Default, Serialize, Deserialize, Clone)]
|
||||
pub struct ConsulServicesInternal {
|
||||
#[serde(rename = "aralez.host")]
|
||||
pub host: String,
|
||||
#[serde(rename = "aralez.path")]
|
||||
pub path: String,
|
||||
#[serde(rename = "aralez.auth")]
|
||||
pub auth: Option<String>,
|
||||
#[serde(rename = "aralez.redirect")]
|
||||
pub redirect: Option<String>,
|
||||
#[serde(rename = "aralez.rate")]
|
||||
pub rate: Option<isize>,
|
||||
#[serde(rename = "aralez.4xx_rate")]
|
||||
pub xrate: Option<u32>,
|
||||
#[serde(rename = "aralez.client_headers")]
|
||||
pub client_headers: Option<Vec<String>>,
|
||||
#[serde(rename = "aralez.server_headers")]
|
||||
pub server_headers: Option<Vec<String>>,
|
||||
#[serde(rename = "aralez.to_https")]
|
||||
pub to_https: Option<bool>,
|
||||
}
|
||||
|
||||
pub type ConsulServices = HashMap<String, ConsulServicesInternal>;
|
||||
|
||||
pub async fn for_consul_list(url: &str, token: Option<String>) -> Option<ConsulServices> {
|
||||
if let Some(data) = getfromapi(url, token, "consul").await {
|
||||
let yo = parse_services(data);
|
||||
if let Ok(y) = yo {
|
||||
return Some(y);
|
||||
}
|
||||
return None;
|
||||
}
|
||||
let mut inner_vec = Vec::new();
|
||||
let upstreams: DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)> = DashMap::new();
|
||||
let endpoints: Vec<ConsulService> = resp.json().await.ok()?;
|
||||
for subsets in endpoints {
|
||||
let addr = subsets.tagged_addresses.get("lan_ipv4").unwrap().address.clone();
|
||||
let prt = subsets.tagged_addresses.get("lan_ipv4").unwrap().port;
|
||||
let to_add = Arc::from(InnerMap {
|
||||
address: Arc::from(&*addr),
|
||||
port: prt,
|
||||
is_ssl: false,
|
||||
is_http2: false,
|
||||
to_https: conf.to_https.unwrap_or(false),
|
||||
rate_limit: conf.rate_limit,
|
||||
x4xx_limit: conf.x4xx_limit,
|
||||
redirect_to: None,
|
||||
healthcheck: None,
|
||||
authorization: None,
|
||||
});
|
||||
inner_vec.push(to_add);
|
||||
}
|
||||
match_path(conf, &upstreams, inner_vec);
|
||||
Some(upstreams)
|
||||
None
|
||||
}
|
||||
|
||||
fn parse_services(json: Vec<u8>) -> Result<ConsulServices, serde_json::Error> {
|
||||
let raw: HashMap<String, Vec<String>> = serde_json::from_slice(&json)?;
|
||||
Ok(raw
|
||||
.into_iter()
|
||||
.map(|(service, tags)| {
|
||||
let mut internal = ConsulServicesInternal::default();
|
||||
for tag in tags {
|
||||
if let Some((key, value)) = tag.split_once('=') {
|
||||
match key {
|
||||
"aralez.host" => internal.host = value.to_string(),
|
||||
"aralez.path" => internal.path = value.to_string(),
|
||||
"aralez.rate" => internal.rate = value.parse::<isize>().ok(),
|
||||
"aralez.4xx_rate" => internal.xrate = value.parse::<u32>().ok(),
|
||||
"aralez.to_https" => internal.to_https = value.parse::<bool>().ok(),
|
||||
"aralez.auth" => internal.auth = Option::from(value.to_string()),
|
||||
"aralez.redirect" => internal.redirect = Option::from(value.to_string()),
|
||||
"aralez.client_header" => internal.client_headers.get_or_insert_default().push(value.to_string()),
|
||||
"aralez.server_header" => internal.server_headers.get_or_insert_default().push(value.to_string()),
|
||||
_ => {}
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
(service, internal)
|
||||
})
|
||||
.collect())
|
||||
}
|
||||
|
||||
pub async fn for_consul(url: &str, token: Option<String>, conf: &GlobalServiceMapping) -> Option<DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)>> {
|
||||
if let Some(data) = getfromapi(url, token, "consul").await {
|
||||
let endpoints: Vec<ConsulService> = serde_json::from_slice(&data).ok()?;
|
||||
let mut inner_vec = Vec::new();
|
||||
let upstreams: DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)> = DashMap::new();
|
||||
for subsets in endpoints {
|
||||
let to_add = Arc::from(InnerMap {
|
||||
address: Arc::from(&*subsets.address),
|
||||
port: subsets.port,
|
||||
is_ssl: false,
|
||||
is_http2: false,
|
||||
to_https: conf.to_https.unwrap_or(false),
|
||||
rate_limit: conf.rate_limit,
|
||||
x4xx_limit: conf.x4xx_limit,
|
||||
redirect_to: conf.redirect_to.clone().map(Arc::<str>::from),
|
||||
healthcheck: None,
|
||||
authorization: None,
|
||||
});
|
||||
inner_vec.push(to_add);
|
||||
}
|
||||
match_path(conf, &upstreams, inner_vec);
|
||||
return Some(upstreams);
|
||||
};
|
||||
None
|
||||
}
|
||||
|
||||
pub async fn for_kuber(url: &str, token: &str, conf: &GlobalServiceMapping) -> Option<DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)>> {
|
||||
let to = Duration::from_secs(10);
|
||||
let client = Client::builder().timeout(Duration::from_secs(10)).danger_accept_invalid_certs(true).build().ok()?;
|
||||
let resp = client.get(url).timeout(to).bearer_auth(token).send().await.ok()?;
|
||||
if !resp.status().is_success() {
|
||||
eprintln!("Kubernetes API returned status: {}", resp.status());
|
||||
return None;
|
||||
}
|
||||
let endpoints: KubeEndpoints = resp.json().await.ok()?;
|
||||
if let Some(data) = getfromapi(url, Some(token.to_string()), "kubernetes").await {
|
||||
let slice_list: KubeEndpointSliceList = serde_json::from_slice(&data).ok()?;
|
||||
let upstreams: DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)> = DashMap::new();
|
||||
let mut inner_vec = Vec::new();
|
||||
|
||||
let upstreams: DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)> = DashMap::new();
|
||||
for slice in slice_list.items {
|
||||
let ports = match &slice.ports {
|
||||
Some(p) if !p.is_empty() => p,
|
||||
_ => continue,
|
||||
};
|
||||
|
||||
if let Some(subsets) = endpoints.subsets {
|
||||
for subset in subsets {
|
||||
if let (Some(addresses), Some(ports)) = (subset.addresses, subset.ports) {
|
||||
let mut inner_vec = Vec::new();
|
||||
for addr in addresses {
|
||||
for port in &ports {
|
||||
// let redirect_link = conf.redirect_to.as_ref().map(|www| Arc::from(www.as_str()));
|
||||
let to_add = Arc::from(InnerMap {
|
||||
address: Arc::from(addr.ip.clone()),
|
||||
port: port.port,
|
||||
is_ssl: false,
|
||||
is_http2: false,
|
||||
to_https: conf.to_https.unwrap_or(false),
|
||||
rate_limit: conf.rate_limit,
|
||||
x4xx_limit: conf.x4xx_limit,
|
||||
healthcheck: None,
|
||||
redirect_to: None,
|
||||
authorization: None,
|
||||
});
|
||||
inner_vec.push(to_add);
|
||||
for ep in &slice.endpoints {
|
||||
let is_ready = ep.conditions.as_ref().and_then(|c| c.ready).unwrap_or(true);
|
||||
|
||||
if !is_ready {
|
||||
continue;
|
||||
}
|
||||
|
||||
for addr in &ep.addresses {
|
||||
for port in ports {
|
||||
if let Some(port_num) = port.port {
|
||||
let to_add = Arc::from(InnerMap {
|
||||
address: Arc::from(addr.as_str()),
|
||||
port: port_num,
|
||||
is_ssl: false,
|
||||
is_http2: false,
|
||||
to_https: conf.to_https.unwrap_or(false),
|
||||
rate_limit: conf.rate_limit,
|
||||
x4xx_limit: conf.x4xx_limit,
|
||||
healthcheck: None,
|
||||
redirect_to: None,
|
||||
authorization: None,
|
||||
});
|
||||
inner_vec.push(to_add);
|
||||
}
|
||||
}
|
||||
}
|
||||
match_path(conf, &upstreams, inner_vec.clone());
|
||||
}
|
||||
}
|
||||
|
||||
if !inner_vec.is_empty() {
|
||||
match_path(conf, &upstreams, inner_vec);
|
||||
return Some(upstreams);
|
||||
}
|
||||
}
|
||||
Some(upstreams)
|
||||
None
|
||||
}
|
||||
|
||||
pub async fn getfromapi(url: &str, token: Option<String>, provider: &str) -> Option<Vec<u8>> {
|
||||
let (host, port, path, is_tls) = parse_url(&url).ok()?;
|
||||
|
||||
let mut peer = HttpPeer::new((host, port), is_tls, host.to_string());
|
||||
peer.options.total_connection_timeout = Some(Duration::from_secs(5));
|
||||
peer.options.read_timeout = Some(Duration::from_secs(5));
|
||||
|
||||
if is_tls {
|
||||
peer.options.verify_cert = false;
|
||||
peer.options.verify_hostname = false;
|
||||
peer.options.alpn = ALPN::H2H1;
|
||||
}
|
||||
|
||||
let mut http_session = CONNECTOR.get_http_session(&peer).await.ok()?;
|
||||
let mut req = RequestHeader::build("GET", path.as_bytes(), None).ok()?;
|
||||
|
||||
let host_header = if (is_tls && port == 443) || (!is_tls && port == 80) {
|
||||
host.to_string()
|
||||
} else {
|
||||
format!("{}:{}", host, port)
|
||||
};
|
||||
req.insert_header("Host", host_header).ok()?;
|
||||
req.insert_header("Accept", "application/json").ok()?;
|
||||
|
||||
match provider {
|
||||
"consul" => {
|
||||
if let Some(token) = token {
|
||||
req.insert_header("X-Consul-Token", token).ok()?;
|
||||
}
|
||||
}
|
||||
"kubernetes" => {
|
||||
if let Some(token) = token {
|
||||
req.insert_header("Authorization", format!("Bearer {}", token)).ok()?;
|
||||
}
|
||||
}
|
||||
_ => {}
|
||||
}
|
||||
|
||||
if http_session.0.write_request_header(Box::new(req)).await.is_err() {
|
||||
CONNECTOR.release_http_session(http_session.0, &peer, None).await;
|
||||
return None;
|
||||
}
|
||||
|
||||
let status = match http_session.0.read_response_header().await {
|
||||
Ok(_) => http_session.0.response_header().map(|r| r.status.as_u16()).unwrap_or(500),
|
||||
Err(e) => {
|
||||
log::warn!("API call failed to read response header for {}: {}", url, e);
|
||||
500
|
||||
}
|
||||
};
|
||||
|
||||
let mut body_bytes = Vec::new();
|
||||
if status == 200 {
|
||||
while let Ok(Some(chunk)) = http_session.0.read_response_body().await {
|
||||
body_bytes.extend_from_slice(&chunk);
|
||||
}
|
||||
}
|
||||
|
||||
CONNECTOR.release_http_session(http_session.0, &peer, None).await;
|
||||
|
||||
if status == 200 && !body_bytes.is_empty() {
|
||||
Some(body_bytes)
|
||||
} else {
|
||||
None
|
||||
}
|
||||
}
|
||||
|
||||
fn parse_url(url: &str) -> Result<(&str, u16, &str, bool), &'static str> {
|
||||
let is_https = url.starts_with("https://");
|
||||
let default_port = if is_https { 443 } else { 80 };
|
||||
|
||||
let no_scheme = url.split_once("://").map_or(url, |(_, rest)| rest);
|
||||
|
||||
let (authority, uri) = no_scheme.find('/').map_or((no_scheme, "/"), |i| (&no_scheme[..i], &no_scheme[i..]));
|
||||
|
||||
let (host, port) = match authority.split_once(':') {
|
||||
Some((h, p)) => {
|
||||
let port_num = p.parse::<u16>().map_err(|_| "Invalid port number")?;
|
||||
(h, port_num)
|
||||
}
|
||||
None => (authority, default_port),
|
||||
};
|
||||
|
||||
if host.is_empty() {
|
||||
return Err("Empty host in URL");
|
||||
}
|
||||
|
||||
Ok((host, port, uri, is_https))
|
||||
}
|
||||
|
||||
+16
-182
@@ -1,217 +1,50 @@
|
||||
use crate::utils::httpclient;
|
||||
use crate::utils::parceyaml::build_headers;
|
||||
use crate::utils::structs::{Configuration, GlobalServiceMapping, InnerMap, UpstreamsDashMap};
|
||||
use crate::utils::tools::{clone_dashmap_into, compare_dashmaps, print_upstreams};
|
||||
use async_trait::async_trait;
|
||||
use dashmap::DashMap;
|
||||
use futures::channel::mpsc::Sender;
|
||||
use futures::SinkExt;
|
||||
use pingora::prelude::sleep;
|
||||
use rand::RngExt;
|
||||
use serde::Deserialize;
|
||||
use std::collections::HashMap;
|
||||
use std::env;
|
||||
use std::fs;
|
||||
use std::path::Path;
|
||||
use std::sync::atomic::AtomicUsize;
|
||||
use std::sync::Arc;
|
||||
use std::time::Duration;
|
||||
use tokio::fs::File;
|
||||
use tokio::io::AsyncReadExt;
|
||||
use tokio::sync::mpsc::Sender;
|
||||
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
pub struct KubeEndpoints {
|
||||
pub subsets: Option<Vec<KubeSubset>>,
|
||||
}
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
pub struct KubeSubset {
|
||||
pub addresses: Option<Vec<KubeAddress>>,
|
||||
pub ports: Option<Vec<KubePort>>,
|
||||
}
|
||||
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
pub struct KubeAddress {
|
||||
pub ip: String,
|
||||
}
|
||||
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
pub struct KubePort {
|
||||
pub port: u16,
|
||||
}
|
||||
|
||||
#[derive(Debug, Deserialize)]
|
||||
pub struct ConsulService {
|
||||
#[serde(rename = "ServiceTaggedAddresses")]
|
||||
pub tagged_addresses: HashMap<String, ConsulTaggedAddress>,
|
||||
}
|
||||
|
||||
#[derive(Debug, Deserialize)]
|
||||
pub struct ConsulTaggedAddress {
|
||||
#[serde(rename = "Address")]
|
||||
pub address: String,
|
||||
#[serde(rename = "Port")]
|
||||
pub port: u16,
|
||||
}
|
||||
#[allow(clippy::type_complexity)]
|
||||
pub fn list_to_upstreams(lt: Option<DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)>>, upstreams: &UpstreamsDashMap, i: &GlobalServiceMapping) {
|
||||
if let Some(list) = lt {
|
||||
match upstreams.get(&*i.hostname.clone()) {
|
||||
let key: Arc<str> = Arc::from(i.hostname.as_str());
|
||||
match upstreams.get(&key) {
|
||||
Some(upstr) => {
|
||||
for (k, v) in list {
|
||||
upstr.value().insert(k.to_owned(), v);
|
||||
upstr.value().insert(k, v);
|
||||
}
|
||||
}
|
||||
None => {
|
||||
upstreams.insert(Arc::from(i.hostname.clone()), list);
|
||||
upstreams.insert(key, list);
|
||||
}
|
||||
};
|
||||
}
|
||||
}
|
||||
|
||||
pub fn match_path(conf: &GlobalServiceMapping, upstreams: &DashMap<Arc<str>, (Vec<Arc<InnerMap>>, AtomicUsize)>, values: Vec<Arc<InnerMap>>) {
|
||||
match conf.path {
|
||||
Some(ref p) => {
|
||||
upstreams.insert(Arc::from(p.clone()), (values, AtomicUsize::new(0)));
|
||||
}
|
||||
None => {
|
||||
upstreams.insert(Arc::from("/"), (values, AtomicUsize::new(0)));
|
||||
}
|
||||
}
|
||||
let path = conf.path.as_deref().unwrap_or("/");
|
||||
upstreams.insert(Arc::from(path), (values, AtomicUsize::new(0)));
|
||||
}
|
||||
|
||||
async fn read_token(path: &str) -> String {
|
||||
pub async fn read_token(path: &str) -> String {
|
||||
let mut file = File::open(path).await.unwrap();
|
||||
let mut contents = String::new();
|
||||
file.read_to_string(&mut contents).await.unwrap();
|
||||
contents.trim().to_string()
|
||||
}
|
||||
|
||||
#[async_trait]
|
||||
pub trait ServiceDiscovery {
|
||||
async fn fetch_upstreams(&self, config: Arc<Configuration>, toreturn: Sender<Configuration>);
|
||||
}
|
||||
|
||||
pub struct KubernetesDiscovery;
|
||||
pub struct ConsulDiscovery;
|
||||
|
||||
#[async_trait]
|
||||
impl ServiceDiscovery for KubernetesDiscovery {
|
||||
async fn fetch_upstreams(&self, config: Arc<Configuration>, mut toreturn: Sender<Configuration>) {
|
||||
let prev_upstreams = UpstreamsDashMap::new();
|
||||
|
||||
if let Some(kuber) = config.kubernetes.clone() {
|
||||
let servers = kuber.servers.unwrap_or(vec![format!(
|
||||
"{}:{}",
|
||||
env::var("KUBERNETES_SERVICE_HOST").unwrap_or("0.0.0.0".to_string()),
|
||||
env::var("KUBERNETES_SERVICE_PORT_HTTPS").unwrap_or("0".to_string())
|
||||
)]);
|
||||
|
||||
let end = servers.len().saturating_sub(1);
|
||||
let num = if end > 0 { rand::rng().random_range(0..end) } else { 0 };
|
||||
let server = servers.get(num).unwrap().to_string();
|
||||
let path = kuber.tokenpath.unwrap_or("/var/run/secrets/kubernetes.io/serviceaccount/token".to_string());
|
||||
let namespace = get_current_namespace().unwrap_or_else(|| "default".to_string());
|
||||
let token = read_token(path.as_str()).await;
|
||||
loop {
|
||||
let upstreams = UpstreamsDashMap::new();
|
||||
if let Some(kuber) = config.kubernetes.clone() {
|
||||
if let Some(svc) = kuber.services {
|
||||
for service in svc {
|
||||
let header_list: DashMap<Arc<str>, Vec<(String, Arc<str>)>> = DashMap::new();
|
||||
let mut hl = Vec::new();
|
||||
build_headers(&service.client_headers, config.as_ref(), &mut hl);
|
||||
if !hl.is_empty() {
|
||||
match service.path.clone() {
|
||||
Some(path) => {
|
||||
header_list.insert(Arc::from(path.as_str()), hl);
|
||||
}
|
||||
None => {
|
||||
header_list.insert(Arc::from("/"), hl);
|
||||
}
|
||||
}
|
||||
|
||||
// header_list.insert(Arc::from(path.as_str()), hl);
|
||||
// header_list.insert(Arc::from(i.path).unwrap_or(Arc::from("/")).as_str(), hl);
|
||||
config.client_headers.insert(Arc::from(service.hostname.clone()), header_list);
|
||||
}
|
||||
let url = format!("https://{}/api/v1/namespaces/{}/endpoints/{}", server, namespace, service.hostname);
|
||||
// let url = format!("https://{}/api/v1/namespaces/{}/endpoints?labelSelector=app", server, namespace);
|
||||
let list = httpclient::for_kuber(&url, &token, &service).await;
|
||||
// println!("{:?}", list);
|
||||
list_to_upstreams(list, &upstreams, &service);
|
||||
}
|
||||
}
|
||||
if let Some(lt) = clone_compare(&upstreams, &prev_upstreams, &config).await {
|
||||
toreturn.send(lt).await.unwrap();
|
||||
}
|
||||
}
|
||||
sleep(Duration::from_secs(5)).await;
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
fn get_current_namespace() -> Option<String> {
|
||||
let ns_path = "/var/run/secrets/kubernetes.io/serviceaccount/namespace";
|
||||
if Path::new(ns_path).exists() {
|
||||
if let Ok(contents) = fs::read_to_string(ns_path) {
|
||||
return Some(contents.trim().to_string());
|
||||
}
|
||||
}
|
||||
std::env::var("POD_NAMESPACE").ok()
|
||||
}
|
||||
|
||||
#[async_trait]
|
||||
impl ServiceDiscovery for ConsulDiscovery {
|
||||
async fn fetch_upstreams(&self, config: Arc<Configuration>, mut toreturn: Sender<Configuration>) {
|
||||
let prev_upstreams = UpstreamsDashMap::new();
|
||||
loop {
|
||||
let upstreams = UpstreamsDashMap::new();
|
||||
|
||||
if let Some(consul) = config.consul.clone() {
|
||||
let servers = consul.servers.unwrap_or(vec![format!(
|
||||
"{}:{}",
|
||||
env::var("CONSUL_SERVICE_HOST").unwrap_or("0.0.0.0".to_string()),
|
||||
env::var("CONSUL_SERVICE_PORT").unwrap_or("0".to_string())
|
||||
)]);
|
||||
let end = servers.len().saturating_sub(1);
|
||||
let num = if end > 0 { rand::rng().random_range(0..end) } else { 0 };
|
||||
let consul_data = servers.get(num).unwrap().to_string();
|
||||
let ss = consul_data + "/v1/catalog/service/";
|
||||
|
||||
if let Some(svc) = consul.services {
|
||||
for i in svc {
|
||||
let header_list = DashMap::new();
|
||||
let mut hl = Vec::new();
|
||||
build_headers(&i.client_headers, config.as_ref(), &mut hl);
|
||||
if !hl.is_empty() {
|
||||
match i.path.clone() {
|
||||
Some(path) => {
|
||||
header_list.insert(Arc::from(path.as_str()), hl);
|
||||
}
|
||||
None => {
|
||||
header_list.insert(Arc::from("/"), hl);
|
||||
}
|
||||
}
|
||||
// header_list.insert(i.path.clone().unwrap_or("/".to_string()), hl);
|
||||
config.client_headers.insert(Arc::from(i.hostname.clone()), header_list);
|
||||
}
|
||||
|
||||
let pref = ss.clone() + &i.upstream;
|
||||
let list = httpclient::for_consul(pref, consul.token.clone(), &i).await;
|
||||
list_to_upstreams(list, &upstreams, &i);
|
||||
}
|
||||
}
|
||||
}
|
||||
if let Some(lt) = clone_compare(&upstreams, &prev_upstreams, &config).await {
|
||||
toreturn.send(lt).await.unwrap();
|
||||
}
|
||||
sleep(Duration::from_secs(5)).await;
|
||||
}
|
||||
}
|
||||
}
|
||||
async fn clone_compare(upstreams: &UpstreamsDashMap, prev_upstreams: &UpstreamsDashMap, config: &Arc<Configuration>) -> Option<Configuration> {
|
||||
if !compare_dashmaps(upstreams, prev_upstreams) {
|
||||
let tosend: Configuration = Configuration {
|
||||
pub async fn clone_compare(upstreams: &UpstreamsDashMap, config: &Arc<Configuration>) -> Option<Configuration> {
|
||||
if !compare_dashmaps(upstreams, &config.upstreams) {
|
||||
let tosend = Configuration {
|
||||
upstreams: Default::default(),
|
||||
client_headers: config.client_headers.clone(),
|
||||
server_headers: config.server_headers.clone(),
|
||||
@@ -220,10 +53,11 @@ async fn clone_compare(upstreams: &UpstreamsDashMap, prev_upstreams: &UpstreamsD
|
||||
typecfg: config.typecfg.clone(),
|
||||
extraparams: config.extraparams.clone(),
|
||||
};
|
||||
clone_dashmap_into(upstreams, prev_upstreams);
|
||||
clone_dashmap_into(upstreams, &config.upstreams);
|
||||
clone_dashmap_into(upstreams, &tosend.upstreams);
|
||||
print_upstreams(&tosend.upstreams);
|
||||
|
||||
print_upstreams(&tosend.upstreams, &tosend.extraparams);
|
||||
return Some(tosend);
|
||||
};
|
||||
}
|
||||
None
|
||||
}
|
||||
|
||||
@@ -0,0 +1,163 @@
|
||||
use crate::utils::httpclient;
|
||||
use crate::utils::kubewatcher::{start_ingress_watcher_with_config, AralezRouteUpdate};
|
||||
use crate::utils::parceyaml::build_headers;
|
||||
use crate::utils::structs::{Configuration, GlobalServiceMapping, UpstreamsDashMap};
|
||||
use async_trait::async_trait;
|
||||
use dashmap::DashMap;
|
||||
use log::error;
|
||||
use rand::RngExt;
|
||||
use std::env;
|
||||
use std::sync::Arc;
|
||||
|
||||
use crate::utils::kuberconsul::{clone_compare, list_to_upstreams, ServiceDiscovery};
|
||||
use rustls::crypto::ring::default_provider;
|
||||
use rustls::crypto::CryptoProvider;
|
||||
use tokio::sync::mpsc::Sender;
|
||||
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
#[serde(rename_all = "camelCase")]
|
||||
pub struct KubeEndpointSliceList {
|
||||
#[serde(default)]
|
||||
pub items: Vec<KubeEndpointSlice>,
|
||||
}
|
||||
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
#[serde(rename_all = "camelCase")]
|
||||
pub struct KubeEndpointSlice {
|
||||
pub ports: Option<Vec<KubePort>>,
|
||||
#[serde(default)]
|
||||
pub endpoints: Vec<KubeEndpoint>,
|
||||
}
|
||||
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
#[serde(rename_all = "camelCase")]
|
||||
pub struct KubeEndpoint {
|
||||
#[serde(default)]
|
||||
pub addresses: Vec<String>,
|
||||
pub conditions: Option<KubeConditions>,
|
||||
}
|
||||
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
#[serde(rename_all = "camelCase")]
|
||||
pub struct KubeConditions {
|
||||
pub ready: Option<bool>,
|
||||
}
|
||||
|
||||
#[derive(Debug, serde::Deserialize)]
|
||||
#[serde(rename_all = "camelCase")]
|
||||
pub struct KubePort {
|
||||
pub port: Option<u16>,
|
||||
}
|
||||
|
||||
pub struct KubernetesDiscovery;
|
||||
|
||||
#[async_trait]
|
||||
impl ServiceDiscovery for KubernetesDiscovery {
|
||||
async fn fetch_upstreams(&self, config: Arc<Configuration>, toreturn: Sender<Configuration>) {
|
||||
if let Some(kuber) = config.kubernetes.clone() {
|
||||
let servers = kuber.servers.unwrap_or_else(|| {
|
||||
vec![format!(
|
||||
"{}:{}",
|
||||
env::var("KUBERNETES_SERVICE_HOST").unwrap_or_else(|_| "0.0.0.0".to_string()),
|
||||
env::var("KUBERNETES_SERVICE_PORT_HTTPS").unwrap_or_else(|_| "0".to_string())
|
||||
)]
|
||||
});
|
||||
|
||||
let end = servers.len().saturating_sub(1);
|
||||
let num = if end > 0 { rand::rng().random_range(0..end) } else { 0 };
|
||||
let server = servers.get(num).unwrap().to_string();
|
||||
let path = kuber.tokenpath.unwrap_or_else(|| "/var/run/secrets/kubernetes.io/serviceaccount/token".to_string());
|
||||
let token = crate::utils::kuberconsul::read_token(path.as_str()).await;
|
||||
|
||||
if CryptoProvider::get_default().is_none() {
|
||||
default_provider().install_default().expect("Failed to install rustls crypto provider");
|
||||
}
|
||||
|
||||
let (tx, mut rx) = tokio::sync::mpsc::channel::<AralezRouteUpdate>(100);
|
||||
let srv = server.clone();
|
||||
let tok = token.clone();
|
||||
tokio::spawn(async move {
|
||||
if let Err(e) = start_ingress_watcher_with_config(srv.as_str(), tok.as_str(), tx, "aralez").await {
|
||||
error!("Fatal watcher error: {:?}", e);
|
||||
}
|
||||
});
|
||||
|
||||
let upstreams = UpstreamsDashMap::new();
|
||||
|
||||
while let Some(update) = rx.recv().await {
|
||||
let host_key: Arc<str> = Arc::from(update.host.as_str());
|
||||
|
||||
if update.is_deleted {
|
||||
upstreams.remove(&host_key);
|
||||
config.client_headers.remove(&host_key);
|
||||
} else {
|
||||
let service = GlobalServiceMapping {
|
||||
upstream: update.service_name.clone(),
|
||||
hostname: update.host.clone(),
|
||||
path: Some(update.path.clone()),
|
||||
to_https: None,
|
||||
redirect_to: None,
|
||||
authorization: None,
|
||||
rate_limit: update.rate_limit,
|
||||
x4xx_limit: update.x4xx_limit,
|
||||
client_headers: None,
|
||||
server_headers: None,
|
||||
};
|
||||
|
||||
let cheader_list: DashMap<Arc<str>, Vec<(String, Arc<str>)>> = DashMap::new();
|
||||
let sheader_list: DashMap<Arc<str>, Vec<(String, Arc<str>)>> = DashMap::new();
|
||||
|
||||
let mut client_headers_list = Vec::new();
|
||||
let mut server_headers_list = Vec::new();
|
||||
|
||||
let mut chl: Option<Vec<String>> = None;
|
||||
let mut shl: Option<Vec<String>> = None;
|
||||
|
||||
if let Some(hdr) = service.client_headers.as_ref() {
|
||||
chl.get_or_insert_with(Vec::new).extend(hdr.iter().cloned());
|
||||
}
|
||||
if let Some(hdr) = service.server_headers.as_ref() {
|
||||
shl.get_or_insert_with(Vec::new).extend(hdr.iter().cloned());
|
||||
}
|
||||
|
||||
if let Some(ch) = update.client_headers {
|
||||
chl.get_or_insert_with(Vec::new).extend(ch);
|
||||
}
|
||||
if let Some(hdr) = update.server_headers.as_ref() {
|
||||
shl.get_or_insert_with(Vec::new).extend(hdr.iter().cloned());
|
||||
}
|
||||
|
||||
build_headers(&chl, config.as_ref(), &mut client_headers_list);
|
||||
if !client_headers_list.is_empty() {
|
||||
let path_key = service.path.as_deref().unwrap_or("/");
|
||||
cheader_list.insert(Arc::from(path_key), client_headers_list);
|
||||
config.client_headers.insert(host_key.clone(), cheader_list);
|
||||
}
|
||||
|
||||
build_headers(&shl, config.as_ref(), &mut server_headers_list);
|
||||
if !server_headers_list.is_empty() {
|
||||
let path_key = service.path.as_deref().unwrap_or("/");
|
||||
sheader_list.insert(Arc::from(path_key), server_headers_list);
|
||||
config.server_headers.insert(host_key.clone(), sheader_list);
|
||||
}
|
||||
|
||||
let url = format!(
|
||||
"https://{}/apis/discovery.k8s.io/v1/namespaces/{}/endpointslices?labelSelector=kubernetes.io%2Fservice-name%3D{}",
|
||||
server, update.namespace, update.service_name
|
||||
);
|
||||
|
||||
let list = httpclient::for_kuber(&url, &token, &service).await;
|
||||
|
||||
if list.is_none() {
|
||||
error!("Endpoint URL: {} returned empty/invalid response", url);
|
||||
}
|
||||
|
||||
list_to_upstreams(list, &upstreams, &service);
|
||||
}
|
||||
if let Some(lt) = clone_compare(&upstreams, &config).await {
|
||||
let _ = toreturn.send(lt).await;
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,279 @@
|
||||
use dashmap::DashMap;
|
||||
use futures::StreamExt;
|
||||
use hyper::Uri;
|
||||
use k8s_openapi::api::core::v1::{Node, Service};
|
||||
use k8s_openapi::api::networking::v1::Ingress;
|
||||
use kube::api::{Patch, PatchParams};
|
||||
use kube::{
|
||||
api::Api,
|
||||
client::Client,
|
||||
config::{AuthInfo, Config},
|
||||
runtime::watcher::{self, Event},
|
||||
};
|
||||
use log::{error, info};
|
||||
use serde_json::json;
|
||||
use std::sync::Arc;
|
||||
use std::time::Duration;
|
||||
use tokio::sync::mpsc;
|
||||
|
||||
pub struct AralezRouteUpdate {
|
||||
pub host: String,
|
||||
pub path: String,
|
||||
pub namespace: String,
|
||||
pub service_name: String,
|
||||
pub is_deleted: bool,
|
||||
pub rate_limit: Option<isize>,
|
||||
pub x4xx_limit: Option<u32>,
|
||||
pub client_headers: Option<Vec<String>>,
|
||||
pub server_headers: Option<Vec<String>>,
|
||||
}
|
||||
|
||||
#[derive(Debug, Clone)]
|
||||
struct AralezAnnotation {
|
||||
rate_limit: Option<isize>,
|
||||
x4xx_limit: Option<u32>,
|
||||
namespace: String,
|
||||
client_headers: Option<Vec<String>>,
|
||||
server_headers: Option<Vec<String>>,
|
||||
}
|
||||
|
||||
lazy_static::lazy_static! {
|
||||
static ref PATCHED_INGRESSES: Arc<DashMap<String, String>> = Arc::new(DashMap::new());
|
||||
}
|
||||
pub async fn start_ingress_watcher_with_config(
|
||||
api_server: &str,
|
||||
token: &str,
|
||||
tx: mpsc::Sender<AralezRouteUpdate>,
|
||||
target_class: &'static str,
|
||||
) -> Result<(), Box<dyn std::error::Error>> {
|
||||
let client = create_custom_k8s_client(api_server, token, true).await?;
|
||||
let ingresses: Api<Ingress> = Api::all(client.clone());
|
||||
|
||||
let watcher_config = watcher::Config::default().any_semantic();
|
||||
let mut stream = watcher::watcher(ingresses, watcher_config).boxed();
|
||||
|
||||
while let Some(event) = stream.next().await {
|
||||
match event {
|
||||
Ok(Event::Apply(ing)) => {
|
||||
process_ingress_change(&client, &ing, target_class, false, &tx).await;
|
||||
}
|
||||
Ok(Event::Delete(ing)) => {
|
||||
process_ingress_change(&client, &ing, target_class, true, &tx).await;
|
||||
}
|
||||
Ok(Event::InitApply(ing)) => {
|
||||
process_ingress_change(&client, &ing, target_class, false, &tx).await;
|
||||
}
|
||||
Ok(Event::InitDone) => {
|
||||
info!("Ingress watcher initial sync complete");
|
||||
}
|
||||
Err(err) => {
|
||||
error!("Kubernetes Ingress watch error: {:?}", err);
|
||||
}
|
||||
_ => {}
|
||||
}
|
||||
}
|
||||
Ok(())
|
||||
}
|
||||
|
||||
async fn process_ingress_change(client: &Client, ing: &Ingress, target_class: &str, is_deleted: bool, tx: &mpsc::Sender<AralezRouteUpdate>) {
|
||||
let spec = match &ing.spec {
|
||||
Some(s) => s,
|
||||
None => return,
|
||||
};
|
||||
let class_name = spec.ingress_class_name.as_deref().unwrap_or_default();
|
||||
if class_name != target_class {
|
||||
return;
|
||||
}
|
||||
|
||||
if !is_deleted {
|
||||
if let (Some(name), Some(ns)) = (ing.metadata.name.as_deref(), ing.metadata.namespace.as_deref()) {
|
||||
let key = format!("{}/{}", ns, name);
|
||||
let external_ip = resolve_external_ip(client).await;
|
||||
let status_already_correct = ing
|
||||
.status
|
||||
.as_ref()
|
||||
.and_then(|s| s.load_balancer.as_ref())
|
||||
.and_then(|lb| lb.ingress.as_ref())
|
||||
.map(|list| list.iter().any(|i| i.ip.as_deref() == Some(&external_ip)))
|
||||
.unwrap_or(false);
|
||||
|
||||
if status_already_correct {
|
||||
PATCHED_INGRESSES.insert(key, external_ip);
|
||||
} else {
|
||||
PATCHED_INGRESSES.insert(key.clone(), external_ip.clone());
|
||||
let client_clone = client.clone();
|
||||
let name_clone = name.to_string();
|
||||
let ns_clone = ns.to_string();
|
||||
let key_clone = key.clone();
|
||||
tokio::spawn(async move {
|
||||
if let Err(e) = patch_ingress_status_address(&client_clone, &ns_clone, &name_clone, &external_ip).await {
|
||||
error!("Failed to patch ingress status address {}/{}: {}", &ns_clone, &name_clone, e);
|
||||
PATCHED_INGRESSES.remove(&key_clone);
|
||||
}
|
||||
});
|
||||
}
|
||||
}
|
||||
} else {
|
||||
if let (Some(name), Some(ns)) = (ing.metadata.name.as_deref(), ing.metadata.namespace.as_deref()) {
|
||||
PATCHED_INGRESSES.remove(&format!("{}/{}", ns, name));
|
||||
}
|
||||
}
|
||||
|
||||
if let Some(rules) = &spec.rules {
|
||||
for rule in rules {
|
||||
let host = rule.host.clone().unwrap_or_else(|| "*".to_string());
|
||||
|
||||
if let Some(http) = &rule.http {
|
||||
for path_entry in &http.paths {
|
||||
let path = path_entry.path.clone().unwrap_or_else(|| "/".to_string());
|
||||
if let Some(service) = &path_entry.backend.service {
|
||||
let service_name = service.name.clone();
|
||||
let annot = parse_ingress_config(ing);
|
||||
let update = AralezRouteUpdate {
|
||||
host: host.clone(),
|
||||
path,
|
||||
service_name,
|
||||
is_deleted,
|
||||
rate_limit: annot.rate_limit,
|
||||
x4xx_limit: annot.x4xx_limit,
|
||||
client_headers: annot.client_headers,
|
||||
server_headers: annot.server_headers,
|
||||
namespace: annot.namespace,
|
||||
};
|
||||
if let Err(e) = tx.send(update).await {
|
||||
error!("Failed to send route update to channel: {:?}", e);
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
pub async fn create_custom_k8s_client(api_server_url: &str, bearer_token: &str, insecure_tls: bool) -> Result<Client, Box<dyn std::error::Error>> {
|
||||
let full_url = if !api_server_url.starts_with("http://") && !api_server_url.starts_with("https://") {
|
||||
format!("https://{}", api_server_url)
|
||||
} else {
|
||||
api_server_url.to_string()
|
||||
};
|
||||
let uri: Uri = full_url.parse()?;
|
||||
let mut config = Config::new(uri);
|
||||
config.auth_info = AuthInfo {
|
||||
token: Some(bearer_token.trim().to_string().into()),
|
||||
..Default::default()
|
||||
};
|
||||
config.connect_timeout = Some(Duration::from_secs(10));
|
||||
config.read_timeout = None;
|
||||
if insecure_tls {
|
||||
config.accept_invalid_certs = true;
|
||||
}
|
||||
let client = Client::try_from(config)?;
|
||||
Ok(client)
|
||||
}
|
||||
|
||||
fn parse_ingress_config(ing: &Ingress) -> AralezAnnotation {
|
||||
let namespace = ing.metadata.namespace.clone().unwrap_or_else(|| "default".to_string());
|
||||
let annotations = ing.metadata.annotations.as_ref();
|
||||
|
||||
let client_headers = annotations.and_then(|a| a.get("aralez.rs/client_headers")).and_then(|ch| serde_json::from_str(ch).ok());
|
||||
|
||||
let server_headers = annotations.and_then(|a| a.get("aralez.rs/server_headers")).and_then(|sh| serde_json::from_str(sh).ok());
|
||||
|
||||
AralezAnnotation {
|
||||
rate_limit: annotations.and_then(|a| a.get("aralez.rs/rate_limit")).and_then(|v| v.parse().ok()),
|
||||
x4xx_limit: annotations.and_then(|a| a.get("aralez.rs/x4xx_limit")).and_then(|v| v.parse().ok()),
|
||||
client_headers,
|
||||
server_headers,
|
||||
namespace,
|
||||
}
|
||||
}
|
||||
|
||||
pub async fn patch_ingress_status_address(client: &Client, namespace: &str, name: &str, external_ip: &str) -> Result<(), kube::Error> {
|
||||
let ingresses: Api<Ingress> = Api::namespaced(client.clone(), namespace);
|
||||
let patch = json!({
|
||||
"status": {
|
||||
"loadBalancer": {
|
||||
"ingress": [
|
||||
{
|
||||
"ip": external_ip
|
||||
}
|
||||
]
|
||||
}
|
||||
}
|
||||
});
|
||||
let params = PatchParams::default();
|
||||
|
||||
match ingresses.patch_status(name, ¶ms, &Patch::Strategic(patch)).await {
|
||||
Ok(_) => {
|
||||
info!("Successfully patched Ingress {}/{} ADDRESS to {}", namespace, name, external_ip);
|
||||
Ok(())
|
||||
}
|
||||
Err(e) => {
|
||||
error!("Failed to patch status for Ingress {}/{}: {:?}", namespace, name, e);
|
||||
Err(e)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
pub async fn discover_node_ip(client: &Client) -> Option<String> {
|
||||
let nodes: Api<Node> = Api::all(client.clone());
|
||||
if let Ok(node_list) = nodes.list(&Default::default()).await {
|
||||
for node in node_list {
|
||||
if let Some(status) = node.status {
|
||||
if let Some(addresses) = status.addresses {
|
||||
for addr in &addresses {
|
||||
if addr.type_ == "ExternalIP" {
|
||||
return Some(addr.address.clone());
|
||||
}
|
||||
}
|
||||
for addr in &addresses {
|
||||
if addr.type_ == "InternalIP" {
|
||||
return Some(addr.address.clone());
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
None
|
||||
}
|
||||
pub async fn discover_controller_ip(client: &Client, namespace: &str, service_name: &str) -> Option<String> {
|
||||
let services: Api<Service> = Api::namespaced(client.clone(), namespace);
|
||||
if let Ok(svc) = services.get(service_name).await {
|
||||
if let Some(status) = svc.status {
|
||||
if let Some(lb) = status.load_balancer {
|
||||
if let Some(ingress_list) = lb.ingress {
|
||||
for ing in ingress_list {
|
||||
if let Some(ip) = ing.ip {
|
||||
return Some(ip);
|
||||
}
|
||||
if let Some(hostname) = ing.hostname {
|
||||
return Some(hostname);
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
None
|
||||
}
|
||||
|
||||
pub async fn resolve_external_ip(client: &Client) -> String {
|
||||
if let Ok(ip) = std::env::var("ARALEZ_EXTERNAL_IP") {
|
||||
let trimmed = ip.trim();
|
||||
if !trimmed.is_empty() {
|
||||
return trimmed.to_string();
|
||||
}
|
||||
}
|
||||
let svc_name = std::env::var("ARALEZ_SERVICE_NAME").unwrap_or_else(|_| "aralez-service".to_string());
|
||||
let svc_ns = std::env::var("ARALEZ_SERVICE_NAMESPACE").unwrap_or_else(|_| "aralez".to_string());
|
||||
|
||||
if let Some(ip) = discover_controller_ip(client, &svc_ns, &svc_name).await {
|
||||
return ip;
|
||||
}
|
||||
if let Some(ip) = discover_node_ip(client).await {
|
||||
return ip;
|
||||
}
|
||||
|
||||
"127.0.0.1".to_string()
|
||||
}
|
||||
@@ -0,0 +1,21 @@
|
||||
use dashmap::DashMap;
|
||||
use moka::sync::Cache;
|
||||
use pingora_cache::eviction::simple_lru::Manager;
|
||||
use pingora_cache::lock::CacheLock;
|
||||
use pingora_cache::MemCache;
|
||||
use pingora_limits::rate::Rate;
|
||||
use std::collections::HashMap;
|
||||
use std::net::IpAddr;
|
||||
use std::sync::{Arc, LazyLock};
|
||||
use std::sync::{OnceLock, RwLock};
|
||||
use std::time::Duration;
|
||||
|
||||
pub static REVERSE_STORE: LazyLock<DashMap<String, String>> = LazyLock::new(DashMap::new);
|
||||
pub static RATE_LIMITER: LazyLock<Rate> = LazyLock::new(|| Rate::new(Duration::from_secs(1)));
|
||||
pub static REQUESTS_4XX: LazyLock<Cache<IpAddr, u32>> = LazyLock::new(|| Cache::builder().time_to_live(Duration::from_secs(1)).build());
|
||||
pub static LOCALHOST: LazyLock<Arc<str>> = LazyLock::new(|| Arc::from("localhost"));
|
||||
pub static MEM_CACHE: LazyLock<MemCache> = LazyLock::new(MemCache::new);
|
||||
pub static CACHE_LOCK: LazyLock<CacheLock> = LazyLock::new(|| CacheLock::new(Duration::from_secs(30)));
|
||||
pub static EVICTION: OnceLock<Manager> = OnceLock::new();
|
||||
pub static CACHE_TTL: OnceLock<u64> = OnceLock::new();
|
||||
pub static CHALLENGES: LazyLock<RwLock<HashMap<String, String>>> = LazyLock::new(|| RwLock::new(HashMap::new()));
|
||||
+111
-11
@@ -1,3 +1,5 @@
|
||||
use crate::utils::lazylock::EVICTION;
|
||||
use pingora_cache::eviction::EvictionManager;
|
||||
use pingora_http::Method;
|
||||
use pingora_http::StatusCode;
|
||||
use pingora_http::Version;
|
||||
@@ -14,10 +16,17 @@ pub struct MetricTypes {
|
||||
pub version: Version,
|
||||
}
|
||||
|
||||
pub static OPEN_FILES: LazyLock<IntGauge> = LazyLock::new(|| register_int_gauge!("aralez_open_files", "Number of open file descriptors").unwrap());
|
||||
pub static LOGGING_ERRORS: LazyLock<IntGauge> = LazyLock::new(|| register_int_gauge!("aralez_logging_errors", "Number of log errors").unwrap());
|
||||
pub static MEMORY_USAGE: LazyLock<IntGauge> = LazyLock::new(|| register_int_gauge!("aralez_memory_bytes", "Total memory allocated in bytes").unwrap());
|
||||
pub static ACTIVE_SESSIONS: LazyLock<IntGauge> = LazyLock::new(|| register_int_gauge!("aralez_active_sessions", "Current number of active sessions").unwrap());
|
||||
|
||||
pub static REQUEST_COUNT: LazyLock<IntCounter> = LazyLock::new(|| register_int_counter!("aralez_requests_total", "Total number of requests handled by Aralez").unwrap());
|
||||
|
||||
pub static CACHE_SIZE_BYTES: LazyLock<IntGauge> = LazyLock::new(|| register_int_gauge!("aralez_cache_size_bytes", "Current cache size in bytes").unwrap());
|
||||
pub static CACHE_ITEMS: LazyLock<IntGauge> = LazyLock::new(|| register_int_gauge!("aralez_cache_items", "Current number of cached objects").unwrap());
|
||||
pub static CACHE_EVICTED_BYTES: LazyLock<IntGauge> = LazyLock::new(|| register_int_gauge!("aralez_cache_evicted_bytes_total", "Total bytes evicted from cache").unwrap());
|
||||
|
||||
pub static CACHE_EVICTED_ITEMS: LazyLock<IntGauge> = LazyLock::new(|| register_int_gauge!("aralez_cache_evicted_items_total", "Total cache items evicted").unwrap());
|
||||
pub static RESPONSE_CODES: LazyLock<IntCounterVec> =
|
||||
LazyLock::new(|| register_int_counter_vec!("aralez_responses_total", "Responses grouped by status code", &["status"]).unwrap());
|
||||
|
||||
@@ -25,7 +34,7 @@ pub static RESPONSE_LATENCY: LazyLock<Histogram> = LazyLock::new(|| {
|
||||
register_histogram!(
|
||||
"aralez_response_latency_seconds",
|
||||
"Response latency in seconds",
|
||||
vec![0.01, 0.05, 0.1, 0.25, 0.5, 1.0, 2.0, 5.0]
|
||||
vec![0.001, 0.005, 0.01, 0.025, 0.05, 0.075, 0.1, 0.25, 0.5, 1.0, 2.0, 5.0]
|
||||
)
|
||||
.unwrap()
|
||||
});
|
||||
@@ -38,19 +47,110 @@ pub static REQUESTS_BY_UPSTREAM: LazyLock<IntCounterVec> =
|
||||
|
||||
pub static REQUESTS_BY_VERSION: LazyLock<IntCounterVec> =
|
||||
LazyLock::new(|| register_int_counter_vec!("aralez_requests_by_version_total", "Number of requests by HTTP versions", &["version"]).unwrap());
|
||||
pub static HTTP_11_COUNT: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_VERSION.with_label_values(&["HTTP/1.1"]));
|
||||
pub static HTTP_20_COUNT: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_VERSION.with_label_values(&["HTTP/2.0"]));
|
||||
pub static HTTP_30_COUNT: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_VERSION.with_label_values(&["HTTP/3.0"]));
|
||||
pub static HTTP_10_COUNT: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_VERSION.with_label_values(&["HTTP/1.0"]));
|
||||
pub static HTTP_UNK_COUNT: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_VERSION.with_label_values(&["Unknown"]));
|
||||
|
||||
pub static METHOD_GET: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_METHOD.with_label_values(&["GET"]));
|
||||
pub static METHOD_POST: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_METHOD.with_label_values(&["POST"]));
|
||||
pub static METHOD_PUT: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_METHOD.with_label_values(&["PUT"]));
|
||||
pub static METHOD_DELETE: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_METHOD.with_label_values(&["DELETE"]));
|
||||
pub static METHOD_HEAD: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_METHOD.with_label_values(&["HEAD"]));
|
||||
pub static METHOD_OPTIONS: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_METHOD.with_label_values(&["OPTIONS"]));
|
||||
pub static METHOD_PATCH: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_METHOD.with_label_values(&["PATCH"]));
|
||||
pub static METHOD_OTHER: LazyLock<IntCounter> = LazyLock::new(|| REQUESTS_BY_METHOD.with_label_values(&["OTHER"]));
|
||||
|
||||
pub static STATUS_100: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["100"]));
|
||||
pub static STATUS_101: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["101"]));
|
||||
pub static STATUS_200: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["200"]));
|
||||
pub static STATUS_204: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["204"]));
|
||||
pub static STATUS_301: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["301"]));
|
||||
pub static STATUS_302: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["302"]));
|
||||
pub static STATUS_304: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["304"]));
|
||||
pub static STATUS_400: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["400"]));
|
||||
pub static STATUS_403: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["403"]));
|
||||
pub static STATUS_404: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["404"]));
|
||||
pub static STATUS_500: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["500"]));
|
||||
pub static STATUS_501: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["501"]));
|
||||
pub static STATUS_502: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["502"]));
|
||||
pub static STATUS_503: LazyLock<IntCounter> = LazyLock::new(|| RESPONSE_CODES.with_label_values(&["503"]));
|
||||
|
||||
pub fn calc_metrics(metric_types: &MetricTypes) {
|
||||
REQUEST_COUNT.inc();
|
||||
let version_str = match metric_types.version {
|
||||
Version::HTTP_11 => "HTTP/1.1",
|
||||
Version::HTTP_2 => "HTTP/2.0",
|
||||
Version::HTTP_3 => "HTTP/3.0",
|
||||
Version::HTTP_10 => "HTTP/1.0",
|
||||
_ => "Unknown",
|
||||
match metric_types.version {
|
||||
Version::HTTP_11 => HTTP_11_COUNT.inc(),
|
||||
Version::HTTP_2 => HTTP_20_COUNT.inc(),
|
||||
Version::HTTP_3 => HTTP_30_COUNT.inc(),
|
||||
Version::HTTP_10 => HTTP_10_COUNT.inc(),
|
||||
_ => HTTP_UNK_COUNT.inc(),
|
||||
};
|
||||
REQUESTS_BY_VERSION.with_label_values(&[version_str]).inc();
|
||||
RESPONSE_CODES.with_label_values(&[metric_types.code.unwrap_or(StatusCode::GONE).as_str()]).inc();
|
||||
REQUESTS_BY_METHOD.with_label_values(&[metric_types.method.as_str()]).inc();
|
||||
match metric_types.method.as_str() {
|
||||
"GET" => METHOD_GET.inc(),
|
||||
"POST" => METHOD_POST.inc(),
|
||||
"PUT" => METHOD_PUT.inc(),
|
||||
"DELETE" => METHOD_DELETE.inc(),
|
||||
"HEAD" => METHOD_HEAD.inc(),
|
||||
"OPTIONS" => METHOD_OPTIONS.inc(),
|
||||
"PATCH" => METHOD_PATCH.inc(),
|
||||
_ => METHOD_OTHER.inc(),
|
||||
}
|
||||
let code = metric_types.code.unwrap_or(StatusCode::GONE);
|
||||
match code.as_u16() {
|
||||
100 => STATUS_100.inc(),
|
||||
101 => STATUS_101.inc(),
|
||||
200 => STATUS_200.inc(),
|
||||
204 => STATUS_204.inc(),
|
||||
301 => STATUS_301.inc(),
|
||||
302 => STATUS_302.inc(),
|
||||
304 => STATUS_304.inc(),
|
||||
400 => STATUS_400.inc(),
|
||||
403 => STATUS_403.inc(),
|
||||
404 => STATUS_404.inc(),
|
||||
500 => STATUS_500.inc(),
|
||||
501 => STATUS_501.inc(),
|
||||
502 => STATUS_502.inc(),
|
||||
503 => STATUS_503.inc(),
|
||||
_ => RESPONSE_CODES.with_label_values(&[code.as_str()]).inc(), // Fallback for rare status codes
|
||||
}
|
||||
|
||||
REQUESTS_BY_UPSTREAM.with_label_values(&[metric_types.upstream.as_ref()]).inc();
|
||||
RESPONSE_LATENCY.observe(metric_types.latency.as_secs_f64());
|
||||
|
||||
// if let Some(eviction) = EVICTION.get() {
|
||||
// CACHE_SIZE_BYTES.set(eviction.total_size() as i64);
|
||||
// CACHE_ITEMS.set(eviction.total_items() as i64);
|
||||
// CACHE_EVICTED_BYTES.set(eviction.evicted_size() as i64);
|
||||
// CACHE_EVICTED_ITEMS.set(eviction.evicted_items() as i64);
|
||||
// }
|
||||
}
|
||||
|
||||
pub(crate) fn get_memory_usage() -> usize {
|
||||
std::fs::read_to_string("/proc/self/status")
|
||||
.ok()
|
||||
.and_then(|s| {
|
||||
s.lines()
|
||||
.find(|l| l.starts_with("VmRSS:"))
|
||||
.and_then(|l| l.split_whitespace().nth(1))
|
||||
.and_then(|v| v.parse::<usize>().ok())
|
||||
})
|
||||
.unwrap_or(0)
|
||||
* 1024
|
||||
}
|
||||
|
||||
pub fn get_open_files() -> usize {
|
||||
std::fs::read_dir("/proc/self/fd").map(|dir| dir.count()).unwrap_or(0)
|
||||
}
|
||||
|
||||
pub async fn calc_cache_metrics() {
|
||||
loop {
|
||||
if let Some(eviction) = EVICTION.get() {
|
||||
CACHE_SIZE_BYTES.set(eviction.total_size() as i64);
|
||||
CACHE_ITEMS.set(eviction.total_items() as i64);
|
||||
CACHE_EVICTED_BYTES.set(eviction.evicted_size() as i64);
|
||||
CACHE_EVICTED_ITEMS.set(eviction.evicted_items() as i64);
|
||||
}
|
||||
tokio::time::sleep(std::time::Duration::from_secs(5)).await;
|
||||
}
|
||||
}
|
||||
|
||||
+81
-96
@@ -1,15 +1,11 @@
|
||||
use crate::utils::healthcheck;
|
||||
use crate::utils::lazylock::REVERSE_STORE;
|
||||
use crate::utils::state::{is_first_run, mark_not_first_run};
|
||||
use crate::utils::structs::*;
|
||||
use crate::utils::tools::{clone_dashmap, clone_dashmap_into, print_upstreams};
|
||||
use crate::web::logging::log_builder;
|
||||
use dashmap::DashMap;
|
||||
use log::LevelFilter;
|
||||
use log::{error, info, warn};
|
||||
use log4rs::{
|
||||
append::{console::ConsoleAppender, file::FileAppender},
|
||||
config::{Appender, Config as Log4rsConfig, Root},
|
||||
encode::pattern::PatternEncoder,
|
||||
};
|
||||
use std::collections::HashMap;
|
||||
use std::path::Path;
|
||||
use std::sync::atomic::AtomicUsize;
|
||||
@@ -21,57 +17,82 @@ pub static DOMAINS: LazyLock<DashMap<String, bool>> = LazyLock::new(DashMap::new
|
||||
pub async fn load_configuration(d: &str, kind: &str) -> (Option<Configuration>, String) {
|
||||
let mut conf_files = Vec::new();
|
||||
let yaml_data = match kind {
|
||||
"filepath" => match fs::read_to_string(d) {
|
||||
Ok(data) => {
|
||||
let mut confdir = Path::new(d).parent().unwrap().to_path_buf();
|
||||
let mut autocfg = Path::new(d).parent().unwrap().to_path_buf();
|
||||
|
||||
autocfg.push("autoconfigs");
|
||||
if fs::metadata(autocfg.clone()).is_err() {
|
||||
fs::create_dir_all(autocfg.clone()).ok();
|
||||
}
|
||||
autocfg.push("domains.json");
|
||||
if autocfg.exists() {
|
||||
let json: Option<Vec<String>> = fs::read_to_string(autocfg).ok().and_then(|s| serde_json::from_str(&s).ok());
|
||||
if let Some(domains) = json {
|
||||
for domain in domains {
|
||||
DOMAINS.insert(domain, true);
|
||||
"filepath" => {
|
||||
let mut data = String::new();
|
||||
let mut last_error = None;
|
||||
for _ in 0..5 {
|
||||
match fs::read_to_string(d) {
|
||||
Ok(content) => {
|
||||
if !content.trim().is_empty() {
|
||||
data = content;
|
||||
break;
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
confdir.push("conf.d");
|
||||
|
||||
if let Ok(entries) = fs::read_dir(&confdir) {
|
||||
let mut paths: Vec<_> = entries
|
||||
.flatten()
|
||||
.map(|e| e.path())
|
||||
.filter(|p| p.extension().and_then(|e| e.to_str()) == Some("yaml"))
|
||||
.collect();
|
||||
paths.sort();
|
||||
|
||||
for path in paths {
|
||||
let content = fs::read_to_string(&path);
|
||||
match content {
|
||||
Ok(content) => {
|
||||
conf_files.push(content);
|
||||
}
|
||||
Err(e) => {
|
||||
error!("Reading: {}: {:?}", path.display(), e)
|
||||
}
|
||||
};
|
||||
Err(e) => {
|
||||
error!("Config read failed, retrying...");
|
||||
last_error = Some(e);
|
||||
}
|
||||
}
|
||||
|
||||
info!("Reading upstreams from {}", d);
|
||||
data
|
||||
tokio::time::sleep(std::time::Duration::from_millis(10)).await;
|
||||
}
|
||||
Err(e) => {
|
||||
error!("Reading: {}: {:?}", d, e);
|
||||
if data.is_empty() {
|
||||
let err_msg = match last_error {
|
||||
Some(e) => {
|
||||
error!("Reading: {}: {:?}", d, e);
|
||||
e.to_string()
|
||||
}
|
||||
None => {
|
||||
error!("Reading: {}: File is empty after retries", d);
|
||||
"File is empty".to_string()
|
||||
}
|
||||
};
|
||||
warn!("Running with empty upstreams list, update it via API");
|
||||
return (None, e.to_string());
|
||||
return (None, err_msg);
|
||||
}
|
||||
},
|
||||
|
||||
let mut confdir = Path::new(d).parent().unwrap().to_path_buf();
|
||||
let mut autocfg = Path::new(d).parent().unwrap().to_path_buf();
|
||||
|
||||
autocfg.push("autoconfigs");
|
||||
if fs::metadata(autocfg.clone()).is_err() {
|
||||
fs::create_dir_all(autocfg.clone()).ok();
|
||||
}
|
||||
autocfg.push("domains.json");
|
||||
if autocfg.exists() {
|
||||
let json: Option<Vec<String>> = fs::read_to_string(autocfg).ok().and_then(|s| serde_json::from_str(&s).ok());
|
||||
if let Some(domains) = json {
|
||||
for domain in domains {
|
||||
DOMAINS.insert(domain, true);
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
confdir.push("conf.d");
|
||||
|
||||
if let Ok(entries) = fs::read_dir(&confdir) {
|
||||
let mut paths: Vec<_> = entries
|
||||
.flatten()
|
||||
.map(|e| e.path())
|
||||
.filter(|p| p.extension().and_then(|e| e.to_str()) == Some("yaml"))
|
||||
.collect();
|
||||
paths.sort();
|
||||
|
||||
for path in paths {
|
||||
let content = fs::read_to_string(&path);
|
||||
match content {
|
||||
Ok(content) => {
|
||||
conf_files.push(content);
|
||||
}
|
||||
Err(e) => {
|
||||
error!("Reading: {}: {:?}", path.display(), e)
|
||||
}
|
||||
};
|
||||
}
|
||||
}
|
||||
|
||||
info!("Reading upstreams from {}", d);
|
||||
data // [2606:4700:2ff9::1]:443
|
||||
}
|
||||
"content" => {
|
||||
info!("Reading upstreams from API post body");
|
||||
d.to_string()
|
||||
@@ -82,10 +103,9 @@ pub async fn load_configuration(d: &str, kind: &str) -> (Option<Configuration>,
|
||||
}
|
||||
};
|
||||
|
||||
let mut parsed: Config = match serde_yml::from_str(&yaml_data) {
|
||||
let mut parsed: Config = match noyalib::from_str(&yaml_data) {
|
||||
Ok(cfg) => cfg,
|
||||
Err(e) => {
|
||||
println!("================================================");
|
||||
error!("Failed to parse upstreams file: {}", e);
|
||||
return (None, e.to_string());
|
||||
}
|
||||
@@ -93,7 +113,7 @@ pub async fn load_configuration(d: &str, kind: &str) -> (Option<Configuration>,
|
||||
|
||||
if let Some(ref mut upstreams) = parsed.upstreams {
|
||||
for uconf in conf_files {
|
||||
let p: HashMap<String, HostConfig> = match serde_yml::from_str(&uconf) {
|
||||
let p: HashMap<String, HostConfig> = match noyalib::from_str(&uconf) {
|
||||
Ok(ucfg) => ucfg,
|
||||
Err(e) => {
|
||||
error!("Failed to parse upstreams file: {}", e);
|
||||
@@ -200,7 +220,8 @@ async fn populate_file_upstreams(config: &mut Configuration, parsed: &Config) {
|
||||
}
|
||||
|
||||
let redirect_link = path_config.redirect_to.as_ref().map(|www| Arc::from(www.as_str()));
|
||||
if let Some((ip, port_str)) = server.split_once(':') {
|
||||
|
||||
if let Some((ip, port_str)) = server.rsplit_once(':') {
|
||||
if let Ok(port) = port_str.parse::<u16>() {
|
||||
server_list.push(Arc::from(InnerMap {
|
||||
address: Arc::from(ip),
|
||||
@@ -233,36 +254,31 @@ async fn populate_file_upstreams(config: &mut Configuration, parsed: &Config) {
|
||||
clone_dashmap_into(&r, &config.upstreams);
|
||||
}
|
||||
info!("Upstream Config:");
|
||||
print_upstreams(&config.upstreams);
|
||||
REVERSE_STORE.clear();
|
||||
print_upstreams(&config.upstreams, &config.extraparams);
|
||||
}
|
||||
}
|
||||
pub fn parce_main_config(path: &str) -> AppConfig {
|
||||
let data = fs::read_to_string(path).unwrap();
|
||||
let reply = DashMap::new();
|
||||
let cfg: HashMap<String, String> = serde_yml::from_str(&data).expect("Failed to parse main config file");
|
||||
let mut cfo: AppConfig = serde_yml::from_str(&data).expect("Failed to parse main config file");
|
||||
|
||||
let mut cfo: AppConfig = noyalib::from_str(&data).expect("Failed to parse main config file");
|
||||
if let Ok(jwt_key) = env::var("JWT_KEY") {
|
||||
cfo.master_key = Some(jwt_key);
|
||||
};
|
||||
|
||||
log_builder(&cfo, &cfo.log_file);
|
||||
cfo.hc_method = cfo.hc_method.to_uppercase();
|
||||
for (k, v) in cfg {
|
||||
reply.insert(k.to_string(), v.to_string());
|
||||
}
|
||||
if let Some((ip, port_str)) = cfo.config_address.split_once(':') {
|
||||
if let Some((ip, port_str)) = cfo.config_address.rsplit_once(':') {
|
||||
if let Ok(port) = port_str.parse::<u16>() {
|
||||
cfo.local_server = Option::from((ip.to_string(), port));
|
||||
}
|
||||
}
|
||||
if let Some(tlsport_cfg) = cfo.proxy_address_tls.clone() {
|
||||
if let Some((_, port_str)) = tlsport_cfg.split_once(':') {
|
||||
if let Some((_, port_str)) = tlsport_cfg.rsplit_once(':') {
|
||||
cfo.proxy_port_tls = Some(port_str.to_string());
|
||||
}
|
||||
};
|
||||
|
||||
if let Some((_, port_str)) = cfo.proxy_address_http.split_once(':') {
|
||||
if let Some((_, port_str)) = cfo.proxy_address_http.rsplit_once(':') {
|
||||
cfo.proxy_port = Some(port_str.to_string());
|
||||
}
|
||||
|
||||
@@ -306,34 +322,3 @@ pub fn build_headers(path_config: &Option<Vec<String>>, _config: &Configuration,
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
fn log_builder(conf: &AppConfig, location: &Option<String>) {
|
||||
let log_level = match conf.log_level.as_str() {
|
||||
"info" => LevelFilter::Info,
|
||||
"error" => LevelFilter::Error,
|
||||
"warn" => LevelFilter::Warn,
|
||||
"debug" => LevelFilter::Debug,
|
||||
"trace" => LevelFilter::Trace,
|
||||
"off" => LevelFilter::Off,
|
||||
_ => {
|
||||
println!("Error reading log level, defaulting to: INFO");
|
||||
LevelFilter::Info
|
||||
}
|
||||
};
|
||||
let pattern = "{d(%Y-%m-%d %H:%M:%S)} {l} {t} - {m}{n}";
|
||||
if let Some(location) = location {
|
||||
let file = FileAppender::builder().encoder(Box::new(PatternEncoder::new(pattern))).build(location).unwrap();
|
||||
let config = Log4rsConfig::builder()
|
||||
.appender(Appender::builder().build("file", Box::new(file)))
|
||||
.build(Root::builder().appender("file").build(log_level))
|
||||
.unwrap();
|
||||
log4rs::init_config(config).unwrap();
|
||||
} else {
|
||||
let stdout = ConsoleAppender::builder().encoder(Box::new(PatternEncoder::new(pattern))).build();
|
||||
let config = Log4rsConfig::builder()
|
||||
.appender(Appender::builder().build("stdout", Box::new(stdout)))
|
||||
.build(Root::builder().appender("stdout").build(log_level))
|
||||
.unwrap();
|
||||
log4rs::init_config(config).unwrap();
|
||||
}
|
||||
}
|
||||
|
||||
@@ -16,14 +16,3 @@ pub fn is_first_run() -> bool {
|
||||
let state = GLOBAL_STATE.read().unwrap();
|
||||
state.first_run
|
||||
}
|
||||
|
||||
/*
|
||||
impl SharedState {
|
||||
pub fn mark_first_run(&mut self) {
|
||||
self.first_run = false;
|
||||
}
|
||||
pub fn is_first_run(&self) -> bool {
|
||||
self.first_run
|
||||
}
|
||||
}
|
||||
*/
|
||||
|
||||
@@ -8,8 +8,6 @@ pub type UpstreamsDashMap = DashMap<Arc<str>, DashMap<Arc<str>, (Vec<Arc<InnerMa
|
||||
|
||||
pub type UpstreamsIdMap = DashMap<String, Arc<InnerMap>>;
|
||||
pub type Headers = DashMap<Arc<str>, DashMap<Arc<str>, Vec<(String, Arc<str>)>>>;
|
||||
// pub type UpstreamsSerDde = Option<HashMap<String, HostConfig>>;
|
||||
// pub type UpstreamsSerDe = HashMap<String, HostConfig>;
|
||||
|
||||
#[derive(Clone, Debug, Default)]
|
||||
pub struct Extraparams {
|
||||
@@ -22,11 +20,12 @@ pub struct Extraparams {
|
||||
|
||||
#[derive(Debug, Default, Clone, Serialize, Deserialize)]
|
||||
pub struct GlobalServiceMapping {
|
||||
pub redirect_to: Option<String>,
|
||||
pub authorization: Option<String>,
|
||||
pub upstream: String,
|
||||
pub hostname: String,
|
||||
pub path: Option<String>,
|
||||
pub to_https: Option<bool>,
|
||||
pub sticky_sessions: Option<u64>,
|
||||
pub rate_limit: Option<isize>,
|
||||
pub x4xx_limit: Option<u32>,
|
||||
pub client_headers: Option<Vec<String>>,
|
||||
@@ -36,14 +35,12 @@ pub struct GlobalServiceMapping {
|
||||
#[derive(Clone, Default, Debug, Serialize, Deserialize)]
|
||||
pub struct Kubernetes {
|
||||
pub servers: Option<Vec<String>>,
|
||||
pub services: Option<Vec<GlobalServiceMapping>>,
|
||||
pub tokenpath: Option<String>,
|
||||
}
|
||||
|
||||
#[derive(Clone, Default, Debug, Serialize, Deserialize)]
|
||||
pub struct Consul {
|
||||
pub servers: Option<Vec<String>>,
|
||||
pub services: Option<Vec<GlobalServiceMapping>>,
|
||||
pub token: Option<String>,
|
||||
}
|
||||
#[derive(Debug, Default, Serialize, Deserialize)]
|
||||
@@ -112,6 +109,10 @@ pub struct AppConfig {
|
||||
pub hc_method: String,
|
||||
pub upstreams_conf: String,
|
||||
pub log_level: String,
|
||||
pub cache_size_mb: Option<usize>,
|
||||
pub cache_ttl: Option<u64>,
|
||||
pub access_log: Option<String>,
|
||||
pub pid_file: Option<String>,
|
||||
pub master_key: Option<String>,
|
||||
pub config_address: String,
|
||||
pub proxy_address_http: String,
|
||||
@@ -130,6 +131,9 @@ pub struct AppConfig {
|
||||
pub runuser: Option<String>,
|
||||
pub rungroup: Option<String>,
|
||||
pub log_file: Option<String>,
|
||||
pub tcp_keepalive_idle: Option<u64>,
|
||||
pub tcp_keepalive_interval: Option<u64>,
|
||||
pub tcp_keepalive_count: Option<usize>,
|
||||
}
|
||||
|
||||
#[derive(Debug, Default, Clone, PartialEq, Eq, Hash)]
|
||||
|
||||
+40
-23
@@ -1,6 +1,6 @@
|
||||
use crate::tls::load;
|
||||
use crate::tls::load::CertificateConfig;
|
||||
use crate::utils::structs::{InnerMap, InnerMapForJson, UpstreamSnapshotForJson, UpstreamsDashMap, UpstreamsIdMap};
|
||||
use crate::utils::structs::{Extraparams, InnerMapForJson, UpstreamSnapshotForJson, UpstreamsDashMap, UpstreamsIdMap};
|
||||
use dashmap::DashMap;
|
||||
use log::{error, info};
|
||||
use notify::{event::ModifyKind, Config, EventKind, RecommendedWatcher, RecursiveMode, Watcher};
|
||||
@@ -10,9 +10,12 @@ use sha2::{Digest, Sha256};
|
||||
use std::any::type_name;
|
||||
use std::collections::{HashMap, HashSet};
|
||||
use std::fmt::Write;
|
||||
use std::fs::OpenOptions;
|
||||
use std::io::Write as IoWrite;
|
||||
use std::net::SocketAddr;
|
||||
use std::net::TcpListener;
|
||||
use std::os::unix::fs::MetadataExt;
|
||||
use std::os::unix::fs::OpenOptionsExt;
|
||||
use std::str::FromStr;
|
||||
use std::sync::atomic::{AtomicUsize, Ordering};
|
||||
use std::sync::mpsc::{channel, Sender};
|
||||
@@ -20,7 +23,7 @@ use std::sync::Arc;
|
||||
use std::time::{Duration, Instant};
|
||||
use std::{fs, process, thread, time};
|
||||
|
||||
pub fn print_upstreams(upstreams: &UpstreamsDashMap) {
|
||||
pub fn print_upstreams(upstreams: &UpstreamsDashMap, extraparams: &Extraparams) {
|
||||
let mut out = String::new();
|
||||
for host_entry in upstreams.iter() {
|
||||
writeln!(out, "Hostname: {}", host_entry.key()).unwrap();
|
||||
@@ -35,8 +38,8 @@ pub fn print_upstreams(upstreams: &UpstreamsDashMap) {
|
||||
f.is_ssl,
|
||||
f.is_http2,
|
||||
f.to_https,
|
||||
f.rate_limit.unwrap_or(0),
|
||||
f.x4xx_limit.unwrap_or(0)
|
||||
f.rate_limit.unwrap_or(extraparams.rate_limit.unwrap_or(0)),
|
||||
f.x4xx_limit.unwrap_or(extraparams.x4xx_limit.unwrap_or(0))
|
||||
)
|
||||
.unwrap();
|
||||
}
|
||||
@@ -144,11 +147,8 @@ pub fn clone_idmap_into(original: &UpstreamsDashMap, cloned: &UpstreamsIdMap) {
|
||||
cloned.clear();
|
||||
for outer_entry in original.iter() {
|
||||
let inner_map = outer_entry.value();
|
||||
let new_inner_map = DashMap::new();
|
||||
for inner_entry in inner_map.iter() {
|
||||
let path = inner_entry.key();
|
||||
let (vec, _) = inner_entry.value();
|
||||
let new_vec = vec.clone();
|
||||
for x in vec.iter() {
|
||||
let mut id = String::new();
|
||||
write!(
|
||||
@@ -159,8 +159,8 @@ pub fn clone_idmap_into(original: &UpstreamsDashMap, cloned: &UpstreamsIdMap) {
|
||||
x.port,
|
||||
x.is_http2,
|
||||
x.to_https,
|
||||
x.rate_limit.unwrap_or_default(),
|
||||
x.x4xx_limit.unwrap_or_default(),
|
||||
x.rate_limit.unwrap_or_default(),
|
||||
x.healthcheck.unwrap_or_default(),
|
||||
x.authorization
|
||||
)
|
||||
@@ -172,22 +172,8 @@ pub fn clone_idmap_into(original: &UpstreamsDashMap, cloned: &UpstreamsIdMap) {
|
||||
let hash = hasher.finalize();
|
||||
let hex_hash = base16ct::lower::encode_string(&hash);
|
||||
let hh = hex_hash[0..50].to_string();
|
||||
let to_add = InnerMap {
|
||||
address: Arc::from("127.0.0.1"),
|
||||
port: 0,
|
||||
is_ssl: false,
|
||||
is_http2: false,
|
||||
to_https: false,
|
||||
rate_limit: None,
|
||||
x4xx_limit: None,
|
||||
healthcheck: None,
|
||||
redirect_to: None,
|
||||
authorization: None,
|
||||
};
|
||||
cloned.insert(id, Arc::from(to_add));
|
||||
cloned.insert(hh, x.to_owned());
|
||||
}
|
||||
new_inner_map.insert(path.clone(), new_vec);
|
||||
}
|
||||
}
|
||||
info!("Upstreams are fully populated. Ready to server requests");
|
||||
@@ -274,7 +260,7 @@ pub fn drop_priv(user: String, group: String, http_addr: String, tls_addr: Optio
|
||||
}
|
||||
|
||||
pub fn check_priv(addr: &str) {
|
||||
let port = SocketAddr::from_str(addr).map(|sa| sa.port()).unwrap();
|
||||
let port = SocketAddr::from_str(addr).map(|sa| sa.port()).expect("Failed to parse address port ");
|
||||
if port < 1024 {
|
||||
let meta = std::fs::metadata("/proc/self").map(|m| m.uid()).unwrap();
|
||||
if meta != 0 {
|
||||
@@ -380,3 +366,34 @@ pub fn prepend(prefix: &str, val: &Option<Arc<str>>, uri: &str, port: &str) -> O
|
||||
buf
|
||||
})
|
||||
}
|
||||
|
||||
pub fn write_pid_file(path: &str) -> std::io::Result<()> {
|
||||
let mut file = OpenOptions::new()
|
||||
.write(true)
|
||||
.create(true)
|
||||
.truncate(true)
|
||||
.custom_flags(libc::O_NOFOLLOW) // refuse to follow symlinks
|
||||
.open(path)?;
|
||||
file.write_all(process::id().to_string().as_bytes())?;
|
||||
Ok(())
|
||||
}
|
||||
|
||||
#[allow(clippy::needless_return)]
|
||||
pub fn split_host_port(addr: &str, tls: bool) -> Option<(&str, u16, bool, &str)> {
|
||||
match addr.split_once(':') {
|
||||
Some((h, p)) => match p.parse::<u16>() {
|
||||
Ok(port) => return Some((h, port, tls, h)),
|
||||
Err(_) => {
|
||||
log::warn!("ForwardAuth: invalid port in {}", addr);
|
||||
return None;
|
||||
}
|
||||
},
|
||||
None => {
|
||||
if tls {
|
||||
return Some((addr, 443u16, tls, addr));
|
||||
} else {
|
||||
return Some((addr, 80u16, tls, addr));
|
||||
}
|
||||
}
|
||||
};
|
||||
}
|
||||
|
||||
@@ -1,5 +1,7 @@
|
||||
pub mod acme;
|
||||
pub mod bgservice;
|
||||
pub mod gethosts;
|
||||
pub mod logging;
|
||||
pub mod proxyhttp;
|
||||
pub mod start;
|
||||
pub mod webserver;
|
||||
|
||||
@@ -0,0 +1,60 @@
|
||||
use crate::tls::acme::{account, order};
|
||||
use crate::utils::lazylock::CHALLENGES;
|
||||
use axum::body::Body;
|
||||
use axum::extract::State;
|
||||
use axum::http::{Response, StatusCode};
|
||||
use axum::response::IntoResponse;
|
||||
|
||||
#[allow(clippy::needless_return)]
|
||||
pub async fn acme_create(State(state): State<crate::web::webserver::AppState>) -> impl IntoResponse {
|
||||
match account::load_or_create(state.cert_creds.as_str()).await {
|
||||
Ok(txt) => {
|
||||
return Response::builder()
|
||||
.status(StatusCode::OK)
|
||||
.header("Content-Type", "text/plain")
|
||||
.body(Body::from(txt))
|
||||
.unwrap()
|
||||
}
|
||||
Err(e) => {
|
||||
return Response::builder()
|
||||
.status(StatusCode::INTERNAL_SERVER_ERROR)
|
||||
.body(Body::from(format!("Failed to create account: {}", e)))
|
||||
.unwrap()
|
||||
}
|
||||
};
|
||||
}
|
||||
#[allow(clippy::needless_return)]
|
||||
pub async fn acme_order(State(state): State<crate::web::webserver::AppState>, axum::extract::Path(domain): axum::extract::Path<String>) -> impl IntoResponse {
|
||||
let domain_clean = domain.trim_matches('/');
|
||||
match order::order(domain_clean, state.cert_creds.as_str(), state.certs_dir).await {
|
||||
Ok(txt) => {
|
||||
return Response::builder()
|
||||
.status(StatusCode::OK)
|
||||
.header("Content-Type", "text/plain")
|
||||
.body(Body::from(txt))
|
||||
.unwrap()
|
||||
}
|
||||
Err(e) => {
|
||||
return Response::builder()
|
||||
.status(StatusCode::INTERNAL_SERVER_ERROR)
|
||||
.body(Body::from(format!("Failed to order a certificate: {}", e)))
|
||||
.unwrap()
|
||||
}
|
||||
};
|
||||
}
|
||||
pub async fn http01_challenge(axum::extract::Path(token): axum::extract::Path<String>) -> impl IntoResponse {
|
||||
if let Ok(challenges) = CHALLENGES.read() {
|
||||
if let Some(key_authorization) = challenges.get(&token) {
|
||||
return Response::builder()
|
||||
.status(StatusCode::OK)
|
||||
.header("Content-Type", "text/plain")
|
||||
.body(Body::from(key_authorization.clone()))
|
||||
.unwrap();
|
||||
}
|
||||
}
|
||||
Response::builder()
|
||||
.status(StatusCode::NOT_FOUND)
|
||||
.header("Content-Type", "text/plain")
|
||||
.body(Body::from("Not found"))
|
||||
.unwrap()
|
||||
}
|
||||
+8
-11
@@ -1,24 +1,25 @@
|
||||
use crate::tls::acme::order::refresh_order;
|
||||
use crate::utils::discovery::{APIUpstreamProvider, ConsulProvider, Discovery, FromFileProvider, KubernetesProvider};
|
||||
use crate::utils::metrics::calc_cache_metrics;
|
||||
use crate::utils::parceyaml::load_configuration;
|
||||
use crate::utils::structs::Configuration;
|
||||
use crate::utils::tools::*;
|
||||
use crate::utils::*;
|
||||
use crate::web::logging::init_logging;
|
||||
use crate::web::proxyhttp::LB;
|
||||
use async_trait::async_trait;
|
||||
use dashmap::DashMap;
|
||||
use futures::channel::mpsc;
|
||||
use futures::{SinkExt, StreamExt};
|
||||
use log::{error, info};
|
||||
use pingora_core::server::ShutdownWatch;
|
||||
use pingora_core::services::background::BackgroundService;
|
||||
use std::sync::Arc;
|
||||
use tokio::sync::mpsc;
|
||||
|
||||
#[async_trait]
|
||||
impl BackgroundService for LB {
|
||||
async fn start(&self, mut shutdown: ShutdownWatch) {
|
||||
info!("Starting background service"); // tx: Sender<Configuration>
|
||||
let (mut tx, mut rx) = mpsc::channel::<Configuration>(1);
|
||||
let (tx, mut rx) = mpsc::channel::<Configuration>(1);
|
||||
let tx_api = tx.clone();
|
||||
let config = load_configuration(self.config.upstreams_conf.clone().as_str(), "filepath")
|
||||
.await
|
||||
@@ -60,19 +61,13 @@ impl BackgroundService for LB {
|
||||
masterkey: self.config.master_key.clone(),
|
||||
config_api_enabled: self.config.config_api_enabled,
|
||||
upstreams_file: self.config.upstreams_conf.clone(),
|
||||
// certs_dir: self.config.proxy_certificates.clone().unwrap_or_else(|| "/tmp".to_string()),
|
||||
config_dir: confdir.clone(),
|
||||
certs_dir: certdir.clone(),
|
||||
// tls_address: self.config.config_tls_address.clone(),
|
||||
// tls_certificate: self.config.config_tls_certificate.clone(),
|
||||
// tls_key_file: self.config.config_tls_key_file.clone(),
|
||||
file_server_address: self.config.file_server_address.clone(),
|
||||
file_server_folder: self.config.file_server_folder.clone(),
|
||||
current_upstreams: self.ump_upst.clone(),
|
||||
full_upstreams: self.ump_full.clone(),
|
||||
};
|
||||
// let crtdir = api_load.certs_dir.clone();
|
||||
// let tx_api = tx.clone();
|
||||
drop(tokio::spawn(async move { api_load.start(tx_api).await }));
|
||||
|
||||
let uu = self.ump_upst.clone();
|
||||
@@ -82,17 +77,19 @@ impl BackgroundService for LB {
|
||||
drop(tokio::spawn(async move {
|
||||
healthcheck::hc2(uu, ff, im, (&*hc_method.to_string(), hc_interval.to_string().parse().unwrap())).await
|
||||
}));
|
||||
drop(tokio::spawn(async move { calc_cache_metrics().await }));
|
||||
drop(tokio::spawn(async move { refresh_order(certdir, confdir).await }));
|
||||
|
||||
init_logging(self.config.access_log.clone());
|
||||
loop {
|
||||
tokio::select! {
|
||||
_ = shutdown.changed() => {
|
||||
break;
|
||||
}
|
||||
val = rx.next() => {
|
||||
val = rx.recv() => {
|
||||
if let Some(ss) = val {
|
||||
clone_dashmap_into(&ss.upstreams, &self.ump_full);
|
||||
clone_dashmap_into(&ss.upstreams, &self.ump_upst);
|
||||
clone_idmap_into(&ss.upstreams, &self.ump_byid);
|
||||
let current = self.extraparams.load_full();
|
||||
let mut new = (*current).clone();
|
||||
new.to_https = ss.extraparams.to_https;
|
||||
|
||||
+23
-17
@@ -1,7 +1,6 @@
|
||||
use crate::utils::structs::InnerMap;
|
||||
use crate::web::proxyhttp::LB;
|
||||
use async_trait::async_trait;
|
||||
use std::sync::atomic::Ordering;
|
||||
use std::sync::atomic::{AtomicUsize, Ordering};
|
||||
use std::sync::Arc;
|
||||
|
||||
#[derive(Debug, Clone)]
|
||||
@@ -10,30 +9,38 @@ pub struct GetHostsReturHeaders {
|
||||
pub server_headers: Option<Vec<(String, Arc<str>)>>,
|
||||
}
|
||||
|
||||
#[async_trait]
|
||||
pub trait GetHost {
|
||||
fn find_sticky_backend(&self, servers: &[Arc<InnerMap>], backend_id: Option<&str>) -> Option<Arc<InnerMap>>;
|
||||
fn pick_backend(&self, servers: &[Arc<InnerMap>], index: &AtomicUsize, backend_id: Option<&str>) -> Option<Arc<InnerMap>>;
|
||||
fn get_host(&self, peer: &str, path: &str, backend_id: Option<&str>) -> Option<Arc<InnerMap>>;
|
||||
|
||||
fn get_header(&self, peer: &str, path: &str) -> Option<GetHostsReturHeaders>;
|
||||
// fn get_upstreams(&self) -> Arc<UpstreamsDashMap>;
|
||||
}
|
||||
#[async_trait]
|
||||
impl GetHost for LB {
|
||||
fn get_host(&self, peer: &str, path: &str, backend_id: Option<&str>) -> Option<Arc<InnerMap>> {
|
||||
if let Some(b) = backend_id {
|
||||
if let Some(bb) = self.ump_byid.get(b) {
|
||||
return Some(bb.value().clone());
|
||||
}
|
||||
fn find_sticky_backend(&self, servers: &[Arc<InnerMap>], backend_id: Option<&str>) -> Option<Arc<InnerMap>> {
|
||||
let b = backend_id?;
|
||||
let bb = self.ump_byid.get(b)?;
|
||||
let target = bb.value();
|
||||
servers.iter().any(|s| s.address == target.address && s.port == target.port).then(|| target.clone())
|
||||
}
|
||||
fn pick_backend(&self, servers: &[Arc<InnerMap>], index: &AtomicUsize, backend_id: Option<&str>) -> Option<Arc<InnerMap>> {
|
||||
if servers.is_empty() {
|
||||
return None;
|
||||
}
|
||||
if let Some(target) = self.find_sticky_backend(servers, backend_id) {
|
||||
return Some(target);
|
||||
}
|
||||
let idx = index.fetch_add(1, Ordering::Relaxed) % servers.len();
|
||||
Some(servers[idx].clone())
|
||||
}
|
||||
fn get_host(&self, peer: &str, path: &str, backend_id: Option<&str>) -> Option<Arc<InnerMap>> {
|
||||
let host_entry = self.ump_upst.get(peer)?;
|
||||
let mut end = path.len();
|
||||
loop {
|
||||
let slice = &path[..end];
|
||||
if let Some(entry) = host_entry.get(slice) {
|
||||
let (servers, index) = entry.value();
|
||||
if !servers.is_empty() {
|
||||
let idx = index.fetch_add(1, Ordering::Relaxed) % servers.len();
|
||||
return Some(servers[idx].clone());
|
||||
if let Some(backend) = self.pick_backend(servers, index, backend_id) {
|
||||
return Some(backend);
|
||||
}
|
||||
}
|
||||
if let Some(pos) = slice.rfind('/') {
|
||||
@@ -44,9 +51,8 @@ impl GetHost for LB {
|
||||
}
|
||||
if let Some(entry) = host_entry.get("/") {
|
||||
let (servers, index) = entry.value();
|
||||
if !servers.is_empty() {
|
||||
let idx = index.fetch_add(1, Ordering::Relaxed) % servers.len();
|
||||
return Some(servers[idx].clone());
|
||||
if let Some(backend) = self.pick_backend(servers, index, backend_id) {
|
||||
return Some(backend);
|
||||
}
|
||||
}
|
||||
None
|
||||
|
||||
@@ -0,0 +1,176 @@
|
||||
use crate::utils::metrics::LOGGING_ERRORS;
|
||||
use crate::utils::structs::AppConfig;
|
||||
use log::{info, LevelFilter};
|
||||
use log4rs::append::rolling_file::policy::compound::roll::fixed_window::FixedWindowRoller;
|
||||
use log4rs::append::rolling_file::policy::compound::trigger::size::SizeTrigger;
|
||||
use log4rs::append::rolling_file::policy::compound::CompoundPolicy;
|
||||
use log4rs::append::rolling_file::RollingFileAppender;
|
||||
use log4rs::{
|
||||
append::console::ConsoleAppender,
|
||||
config::{Appender, Config as Log4rsConfig, Root},
|
||||
encode::pattern::PatternEncoder,
|
||||
};
|
||||
use pingora_cache::CachePhase;
|
||||
use pingora_http::Version;
|
||||
use pingora_proxy::Session;
|
||||
use std::net::{IpAddr, Ipv4Addr};
|
||||
use std::sync::OnceLock;
|
||||
use tokio::sync::mpsc;
|
||||
|
||||
#[derive(Debug)]
|
||||
pub struct LogMessage {
|
||||
pub response_code: u16,
|
||||
pub summary: String,
|
||||
pub client_ip: IpAddr,
|
||||
pub version: Version,
|
||||
pub user_agent: String,
|
||||
pub cache_status: CachePhase,
|
||||
}
|
||||
static LOG_SENDER: OnceLock<mpsc::Sender<LogMessage>> = OnceLock::new();
|
||||
static ACCESS_LOG: OnceLock<LogLevel> = OnceLock::new();
|
||||
const LOG_BUFFER: usize = 16384;
|
||||
|
||||
pub fn log_builder(conf: &AppConfig, location: &Option<String>) {
|
||||
let log_level = match conf.log_level.as_str() {
|
||||
"info" => LevelFilter::Info,
|
||||
"error" => LevelFilter::Error,
|
||||
"warn" => LevelFilter::Warn,
|
||||
"debug" => LevelFilter::Debug,
|
||||
"trace" => LevelFilter::Trace,
|
||||
"off" => LevelFilter::Off,
|
||||
_ => {
|
||||
println!("Error reading log level, defaulting to: INFO");
|
||||
LevelFilter::Info
|
||||
}
|
||||
};
|
||||
|
||||
let pattern = "{d(%Y-%m-%d %H:%M:%S)} {l} {t} - {m}\n";
|
||||
|
||||
if let Some(location) = location {
|
||||
let parts: Vec<&str> = location.splitn(4, ',').map(|s| s.trim()).collect();
|
||||
|
||||
let path = parts.get(0).expect("Syntax error, could not get path for log files");
|
||||
let compress = parts.get(3).unwrap_or(&"No");
|
||||
let size_mb: u64 = parts.get(1).and_then(|s| s.parse().ok()).unwrap_or(100);
|
||||
let keep: u32 = parts.get(2).and_then(|s| s.parse().ok()).unwrap_or(5);
|
||||
|
||||
let pattern_str = match compress {
|
||||
&"compress" => format!("{}.{{}}.gz", path),
|
||||
_ => format!("{}.{{}}", path),
|
||||
};
|
||||
|
||||
let roller = FixedWindowRoller::builder().build(pattern_str.as_str(), keep).unwrap();
|
||||
let trigger = SizeTrigger::new(size_mb * 1024 * 1024);
|
||||
let policy = CompoundPolicy::new(Box::new(trigger), Box::new(roller));
|
||||
|
||||
let file = RollingFileAppender::builder()
|
||||
.encoder(Box::new(PatternEncoder::new(pattern)))
|
||||
.build(path, Box::new(policy))
|
||||
.unwrap();
|
||||
|
||||
let config = Log4rsConfig::builder()
|
||||
.appender(Appender::builder().build("file", Box::new(file)))
|
||||
.build(Root::builder().appender("file").build(log_level))
|
||||
.unwrap();
|
||||
log4rs::init_config(config).unwrap();
|
||||
info!("Logging to: {}, Max file size: {}mb, Files to keep: {}, compression: {} ", path, size_mb, keep, compress);
|
||||
} else {
|
||||
let stdout = ConsoleAppender::builder().encoder(Box::new(PatternEncoder::new(pattern))).build();
|
||||
|
||||
let config = Log4rsConfig::builder()
|
||||
.appender(Appender::builder().build("stdout", Box::new(stdout)))
|
||||
.build(Root::builder().appender("stdout").build(log_level))
|
||||
.unwrap();
|
||||
log4rs::init_config(config).unwrap();
|
||||
info!("No files are configured, logging to stdout");
|
||||
}
|
||||
}
|
||||
|
||||
pub fn init_access_log(level_str: &str) {
|
||||
let level = LogLevel::from_str(level_str);
|
||||
let _ = ACCESS_LOG.set(level);
|
||||
}
|
||||
|
||||
#[derive(Debug)]
|
||||
pub enum LogLevel {
|
||||
Access,
|
||||
Error,
|
||||
None,
|
||||
}
|
||||
|
||||
impl LogLevel {
|
||||
pub fn from_str(s: &str) -> Self {
|
||||
match s {
|
||||
"all" => LogLevel::Access,
|
||||
"error" => LogLevel::Error,
|
||||
_ => LogLevel::None,
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
pub fn access_log(response_code: u16, summary: &str, session: &Session) {
|
||||
let level = ACCESS_LOG.get().unwrap_or(&LogLevel::None);
|
||||
|
||||
let should_log = match level {
|
||||
LogLevel::Access => true,
|
||||
LogLevel::None => false,
|
||||
LogLevel::Error => !(100..=399).contains(&response_code),
|
||||
};
|
||||
|
||||
if !should_log {
|
||||
return;
|
||||
}
|
||||
|
||||
let ip = session
|
||||
.client_addr()
|
||||
.and_then(|addr| addr.as_inet())
|
||||
.map(|addr| addr.ip())
|
||||
.unwrap_or(IpAddr::V4(Ipv4Addr::LOCALHOST));
|
||||
|
||||
let user_agent = session.req_header().headers.get("user-agent").and_then(|v| v.to_str().ok()).unwrap_or("-");
|
||||
// let cache_status = match session.cache.phase() {
|
||||
// CachePhase::Hit => "Hit",
|
||||
// CachePhase::Miss => "Miss",
|
||||
// CachePhase::Expired => "Expired",
|
||||
// _ => "Disabled",
|
||||
// };
|
||||
let log = LogMessage {
|
||||
response_code,
|
||||
summary: summary.to_owned(),
|
||||
client_ip: ip,
|
||||
version: session.req_header().version,
|
||||
user_agent: user_agent.to_owned(),
|
||||
cache_status: session.cache.phase(),
|
||||
};
|
||||
|
||||
if let Some(sender) = LOG_SENDER.get() {
|
||||
let sender = sender;
|
||||
if let Err(_) = sender.try_send(log) {
|
||||
LOGGING_ERRORS.inc();
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
pub fn init_logging(enabled: Option<String>) {
|
||||
if let Some(_) = enabled {
|
||||
LOGGING_ERRORS.set(0);
|
||||
info!("Enabling {:?} log, with buffer of {} messages", ACCESS_LOG.get().unwrap_or(&LogLevel::None), LOG_BUFFER);
|
||||
let (ltx, lrx) = mpsc::channel(LOG_BUFFER);
|
||||
LOG_SENDER.set(ltx).unwrap();
|
||||
std::thread::spawn(move || log_receiver(lrx));
|
||||
}
|
||||
}
|
||||
|
||||
pub fn log_receiver(mut receiver: mpsc::Receiver<LogMessage>) {
|
||||
while let Some(msg) = receiver.blocking_recv() {
|
||||
info!(
|
||||
"{}, {}, {}, client: {}, version: {:?}, useragent: {}",
|
||||
msg.response_code,
|
||||
msg.cache_status.as_str(),
|
||||
msg.summary,
|
||||
msg.client_ip,
|
||||
msg.version,
|
||||
msg.user_agent,
|
||||
);
|
||||
}
|
||||
}
|
||||
+73
-37
@@ -1,34 +1,29 @@
|
||||
use crate::utils::auth::authenticate;
|
||||
use crate::utils::lazylock::{CACHE_LOCK, CACHE_TTL, EVICTION, LOCALHOST, MEM_CACHE, RATE_LIMITER, REQUESTS_4XX, REVERSE_STORE};
|
||||
use crate::utils::metrics::*;
|
||||
use crate::utils::structs::{AppConfig, Extraparams, Headers, InnerMap, UpstreamsDashMap, UpstreamsIdMap};
|
||||
use crate::web::gethosts::{GetHost, GetHostsReturHeaders};
|
||||
use crate::web::logging::access_log;
|
||||
use arc_swap::ArcSwap;
|
||||
use async_trait::async_trait;
|
||||
use axum::body::Bytes;
|
||||
use dashmap::DashMap;
|
||||
use log::{debug, error, warn};
|
||||
use moka::sync::Cache;
|
||||
use pingora::http::{RequestHeader, ResponseHeader, StatusCode};
|
||||
use log::error;
|
||||
use pingora::http::{Method, RequestHeader, ResponseHeader, StatusCode};
|
||||
use pingora::prelude::*;
|
||||
use pingora::ErrorSource::Upstream;
|
||||
use pingora_cache::cache_control::CacheControl;
|
||||
use pingora_cache::{CacheKey, CacheMetaDefaults, RespCacheable};
|
||||
use pingora_core::listeners::ALPN;
|
||||
use pingora_core::prelude::HttpPeer;
|
||||
use pingora_limits::rate::Rate;
|
||||
use pingora_proxy::{ProxyHttp, Session};
|
||||
use sha2::{Digest, Sha256};
|
||||
use std::cell::RefCell;
|
||||
use std::fmt::Write;
|
||||
use std::net::IpAddr;
|
||||
use std::sync::{Arc, LazyLock};
|
||||
use std::sync::Arc;
|
||||
use std::time::Duration;
|
||||
use tokio::time::Instant;
|
||||
|
||||
static REVERSE_STORE: LazyLock<DashMap<String, String>> = LazyLock::new(DashMap::new);
|
||||
thread_local! {static IP_BUFFER: RefCell<String> = RefCell::new(String::with_capacity(50));}
|
||||
pub static RATE_LIMITER: LazyLock<Rate> = LazyLock::new(|| Rate::new(Duration::from_secs(1)));
|
||||
pub static REQUESTS_4XX: LazyLock<Cache<IpAddr, u32>> = LazyLock::new(|| Cache::builder().time_to_live(Duration::from_secs(1)).build());
|
||||
pub static LOCALHOST: LazyLock<Arc<str>> = LazyLock::new(|| Arc::from("localhost"));
|
||||
|
||||
#[derive(Clone)]
|
||||
pub struct LB {
|
||||
pub ump_upst: Arc<UpstreamsDashMap>,
|
||||
@@ -38,6 +33,7 @@ pub struct LB {
|
||||
pub server_headers: Arc<Headers>,
|
||||
pub config: Arc<AppConfig>,
|
||||
pub extraparams: Arc<ArcSwap<Extraparams>>,
|
||||
pub cache_enabled: bool,
|
||||
}
|
||||
|
||||
pub struct Context {
|
||||
@@ -64,6 +60,34 @@ impl ProxyHttp for LB {
|
||||
x4xx_limit: None,
|
||||
}
|
||||
}
|
||||
|
||||
fn cache_key_callback(&self, session: &Session, _ctx: &mut Self::CTX) -> Result<CacheKey> {
|
||||
Ok(CacheKey::new(_ctx.hostname.clone().unwrap_or_default().as_ref(), session.req_header().uri.to_string(), ""))
|
||||
}
|
||||
fn request_cache_filter(&self, session: &mut Session, _ctx: &mut Self::CTX) -> Result<()> {
|
||||
if self.cache_enabled && session.req_header().method == Method::GET {
|
||||
if let Some(eviction) = EVICTION.get() {
|
||||
session.cache.enable(&*MEM_CACHE, Some(eviction), None, Some(&*CACHE_LOCK), None);
|
||||
}
|
||||
}
|
||||
Ok(())
|
||||
}
|
||||
fn response_cache_filter(&self, _session: &Session, resp: &ResponseHeader, _ctx: &mut Self::CTX) -> Result<RespCacheable> {
|
||||
let cc = CacheControl::from_resp_headers(resp);
|
||||
let defaults = CacheMetaDefaults::new(
|
||||
|status| {
|
||||
if status == StatusCode::OK {
|
||||
Some(Duration::from_secs(*CACHE_TTL.get().unwrap_or(&60)))
|
||||
} else {
|
||||
None
|
||||
}
|
||||
},
|
||||
0,
|
||||
0,
|
||||
);
|
||||
Ok(pingora_cache::filters::resp_cacheable(cc.as_ref(), resp.clone(), false, &defaults))
|
||||
}
|
||||
|
||||
async fn request_filter(&self, session: &mut Session, _ctx: &mut Self::CTX) -> Result<bool> {
|
||||
ACTIVE_SESSIONS.inc();
|
||||
let hostname = return_header_host_from_upstream(session, &self.ump_upst);
|
||||
@@ -90,7 +114,6 @@ impl ProxyHttp for LB {
|
||||
if let Some(auth) = _ctx.extraparams.authentication.as_ref().or(innermap.authorization.as_ref()) {
|
||||
if !authenticate(&auth, session).await {
|
||||
let _ = session.respond_error(401).await;
|
||||
warn!("Forbidden: {:?}, {}", session.client_addr(), session.req_header().uri.path());
|
||||
return Ok(true);
|
||||
}
|
||||
}
|
||||
@@ -103,9 +126,6 @@ impl ProxyHttp for LB {
|
||||
let header = ResponseHeader::build(429, None)?;
|
||||
session.set_keepalive(None);
|
||||
session.write_response_header(Box::new(header), true).await?;
|
||||
if let (Some(oi), Some(oa)) = (&_ctx.hostname, rate_key) {
|
||||
warn!("Limit 4XX: {}-rps exceed on {} from {}", rate, oi, oa);
|
||||
}
|
||||
return Ok(true);
|
||||
}
|
||||
}
|
||||
@@ -117,9 +137,6 @@ impl ProxyHttp for LB {
|
||||
let header = ResponseHeader::build(429, None)?;
|
||||
session.set_keepalive(None);
|
||||
session.write_response_header(Box::new(header), true).await?;
|
||||
if let (Some(oi), Some(oa)) = (&_ctx.hostname, rate_key) {
|
||||
warn!("Limit: {}-rps exceed on {} from {}", rate, oi, oa);
|
||||
}
|
||||
return Ok(true);
|
||||
}
|
||||
}
|
||||
@@ -173,24 +190,38 @@ impl ProxyHttp for LB {
|
||||
Some(hostname) => match ctx.upstream_peer.as_ref() {
|
||||
Some(innermap) => {
|
||||
let mut peer = Box::new(HttpPeer::new((&*innermap.address, innermap.port), innermap.is_ssl, hostname.to_string()));
|
||||
|
||||
if innermap.is_http2 {
|
||||
if innermap.is_http2 && !session.is_upgrade_req() {
|
||||
peer.options.alpn = ALPN::H2;
|
||||
}
|
||||
if innermap.is_ssl {
|
||||
peer.options.verify_cert = false;
|
||||
peer.options.verify_hostname = false;
|
||||
}
|
||||
/*
|
||||
Experimental optionsv
|
||||
The following TCP optimizations were tested but caused performance degrade under heavy load:
|
||||
peer.options.tcp_keepalive = Some(TcpKeepalive {
|
||||
idle: Duration::from_secs(60),
|
||||
interval: Duration::from_secs(10),
|
||||
count: 5,
|
||||
user_timeout: Duration::from_secs(30),
|
||||
});
|
||||
|
||||
peer.options.idle_timeout = Some(Duration::from_secs(300));
|
||||
peer.options.tcp_recv_buf = Some(128 * 1024);
|
||||
End of experimental options
|
||||
*/
|
||||
if let Some(_) = ctx.extraparams.sticky_sessions {
|
||||
let mut s = String::with_capacity(64);
|
||||
write!(
|
||||
&mut s,
|
||||
"{}:{}:{}:{}:{}:{}:{}:{:?}",
|
||||
"{}:{}:{}:{}:{}:{}:{}:{}:{:?}",
|
||||
hostname,
|
||||
innermap.address,
|
||||
innermap.port,
|
||||
innermap.is_http2,
|
||||
innermap.to_https,
|
||||
innermap.x4xx_limit.unwrap_or_default(),
|
||||
innermap.rate_limit.unwrap_or_default(),
|
||||
innermap.healthcheck.unwrap_or_default(),
|
||||
innermap.authorization
|
||||
@@ -229,11 +260,11 @@ impl ProxyHttp for LB {
|
||||
}
|
||||
|
||||
async fn upstream_request_filter(&self, session: &mut Session, upstream_request: &mut RequestHeader, ctx: &mut Self::CTX) -> Result<()> {
|
||||
if let Some(client_ip) = session.client_addr() {
|
||||
if let Some(ip) = session.client_addr().and_then(|a| a.as_inet()).map(|i| i.ip()) {
|
||||
IP_BUFFER.with(|buffer| {
|
||||
let mut buf = buffer.borrow_mut();
|
||||
buf.clear();
|
||||
write!(buf, "{}", client_ip).unwrap_or(());
|
||||
write!(buf, "{}", ip).unwrap_or(());
|
||||
upstream_request.append_header("X-Forwarded-For", buf.as_str()).unwrap_or(false);
|
||||
});
|
||||
}
|
||||
@@ -270,30 +301,27 @@ impl ProxyHttp for LB {
|
||||
REVERSE_STORE.insert(hh.clone(), bid.clone());
|
||||
hh
|
||||
};
|
||||
// let _ = _upstream_response.insert_header("set-cookie", format!("backend_id={}; Path=/; Max-Age=600; HttpOnly; SameSite=Lax", tt));
|
||||
let mut buf = String::with_capacity(80);
|
||||
buf.push_str("backend_id=");
|
||||
buf.push_str(&tt);
|
||||
buf.push_str("; Path=/; Max-Age=");
|
||||
buf.push_str(&val.to_string());
|
||||
buf.push_str("; HttpOnly; SameSite=Lax");
|
||||
// buf.push_str("; Path=/; Max-Age=86400; HttpOnly; SameSite=Lax");
|
||||
// println!("{}", buf);
|
||||
let _ = _upstream_response.insert_header("set-cookie", buf.as_str());
|
||||
}
|
||||
}
|
||||
|
||||
if let Some(client_headers) = &ctx.client_headers {
|
||||
for (k, v) in client_headers.iter() {
|
||||
_upstream_response.append_header(k.clone(), v.as_ref())?;
|
||||
let _ = _upstream_response.append_header("set-cookie", buf.as_str());
|
||||
}
|
||||
}
|
||||
Ok(())
|
||||
}
|
||||
async fn upstream_response_filter(&self, _session: &mut Session, upstream_response: &mut ResponseHeader, ctx: &mut Self::CTX) -> Result<()> {
|
||||
if let Some(client_headers) = &ctx.client_headers {
|
||||
for (k, v) in client_headers.iter() {
|
||||
upstream_response.append_header(k.clone(), v.as_ref())?;
|
||||
}
|
||||
}
|
||||
Ok(())
|
||||
}
|
||||
|
||||
async fn logging(&self, session: &mut Session, _e: Option<&pingora::Error>, ctx: &mut Self::CTX) {
|
||||
let response_code = session.response_written().map_or(0, |resp| resp.status.as_u16());
|
||||
debug!("{}, response code: {response_code}", self.request_summary(session, ctx));
|
||||
let m = &MetricTypes {
|
||||
method: session.req_header().method.clone(),
|
||||
code: session.response_written().map(|resp| resp.status),
|
||||
@@ -304,13 +332,21 @@ impl ProxyHttp for LB {
|
||||
calc_metrics(m);
|
||||
ACTIVE_SESSIONS.dec();
|
||||
if let Some(_) = ctx.x4xx_limit.or(ctx.extraparams.x4xx_limit) {
|
||||
if 400 <= response_code && response_code <= 499 {
|
||||
if (400..=499).contains(&response_code) {
|
||||
if let Some(ip) = session.client_addr().and_then(|a| a.as_inet()).map(|i| i.ip()) {
|
||||
let current = REQUESTS_4XX.get(&ip).unwrap_or(0);
|
||||
REQUESTS_4XX.insert(ip, current + 1);
|
||||
}
|
||||
}
|
||||
}
|
||||
// match session.cache.phase() {
|
||||
// CachePhase::Hit => info!("Cache Status: HIT (Served from Memory)"),
|
||||
// CachePhase::Miss => info!("Cache Status: MISS (Fetched from Upstream)"),
|
||||
// CachePhase::Expired => info!("Cache Status: EXPIRED (Revalidating)"),
|
||||
// _ => {}
|
||||
// }
|
||||
|
||||
access_log(response_code, &self.request_summary(session, ctx), session);
|
||||
}
|
||||
}
|
||||
|
||||
|
||||
+73
-12
@@ -1,27 +1,45 @@
|
||||
// use rustls::crypto::ring::default_provider;
|
||||
use crate::tls::grades;
|
||||
use crate::tls::load;
|
||||
use crate::tls::load::CertificateConfig;
|
||||
use crate::utils::lazylock::{CACHE_TTL, EVICTION};
|
||||
use crate::utils::structs::Extraparams;
|
||||
use crate::utils::tools::*;
|
||||
use crate::web::logging::init_access_log;
|
||||
use crate::web::proxyhttp::LB;
|
||||
use arc_swap::ArcSwap;
|
||||
use ctrlc;
|
||||
use dashmap::DashMap;
|
||||
use log::info;
|
||||
use pingora::tls::ssl::{SslAlert, SslRef};
|
||||
use pingora_cache::eviction::simple_lru::Manager;
|
||||
use pingora_core::listeners::tls::TlsSettings;
|
||||
use pingora_core::listeners::TcpSocketOptions;
|
||||
use pingora_core::prelude::{background_service, Opt};
|
||||
use pingora_core::protocols::TcpKeepalive;
|
||||
use pingora_core::server::Server;
|
||||
use privdrop::reexports::libc::SIGQUIT;
|
||||
use rustls::crypto::ring::default_provider;
|
||||
use sd_notify::NotifyState;
|
||||
use signal_hook::{
|
||||
consts::{SIGINT, SIGTERM},
|
||||
iterator::Signals,
|
||||
};
|
||||
use std::sync::mpsc::{channel, Receiver, Sender};
|
||||
use std::sync::Arc;
|
||||
use std::time::Duration;
|
||||
use std::{fs, thread};
|
||||
pub fn run() {
|
||||
// default_provider().install_default().expect("Failed to install rustls crypto provider");
|
||||
default_provider().install_default().expect("Failed to install RusTLS crypto provider");
|
||||
let parameters = Opt::parse_args();
|
||||
let file = parameters.conf.clone().unwrap();
|
||||
let maincfg = crate::utils::parceyaml::parce_main_config(file.as_str());
|
||||
|
||||
let cache_enabled = maincfg.cache_size_mb.is_some();
|
||||
CACHE_TTL.set(maincfg.cache_ttl.unwrap_or(60)).unwrap();
|
||||
if let Some(size) = maincfg.cache_size_mb {
|
||||
let cache_size = size * 1024 * 1024;
|
||||
drop(EVICTION.set(Manager::new(cache_size)));
|
||||
}
|
||||
|
||||
let mut server = Server::new(parameters).unwrap();
|
||||
server.bootstrap();
|
||||
|
||||
@@ -49,18 +67,43 @@ pub fn run() {
|
||||
client_headers: ch_config,
|
||||
server_headers: sh_config,
|
||||
extraparams: ec_config,
|
||||
cache_enabled: cache_enabled,
|
||||
};
|
||||
let al = cfg.access_log.clone().unwrap_or("none".to_string());
|
||||
init_access_log(al.as_str());
|
||||
|
||||
let grade = cfg.proxy_tls_grade.clone().unwrap_or("medium".to_string());
|
||||
info!("TLS grade set to: [ {} ]", grade);
|
||||
|
||||
let bg_srvc = background_service("bgsrvc", lb.clone());
|
||||
let mut proxy = pingora_proxy::http_proxy_service(&server.configuration, lb.clone());
|
||||
let bind_address_http = cfg.proxy_address_http.clone();
|
||||
let bind_address_tls = cfg.proxy_address_tls.clone();
|
||||
|
||||
let mut proxy = pingora_proxy::http_proxy_service(&server.configuration, lb.clone());
|
||||
|
||||
check_priv(bind_address_http.as_str());
|
||||
|
||||
// let mut tcp_options: Option<TcpSocketOptions> = Some(TcpSocketOptions::default());
|
||||
// let mut tcp_options = TcpSocketOptions::default();
|
||||
|
||||
let mut tcp_options: Option<TcpSocketOptions> = None;
|
||||
if let Some(idle) = cfg.tcp_keepalive_idle {
|
||||
let mut to = TcpSocketOptions::default();
|
||||
to.tcp_keepalive = Some(TcpKeepalive {
|
||||
idle: Duration::from_secs(idle),
|
||||
interval: Duration::from_secs(cfg.tcp_keepalive_interval.unwrap_or(10)),
|
||||
user_timeout: Default::default(),
|
||||
count: cfg.tcp_keepalive_count.unwrap_or(5usize),
|
||||
});
|
||||
tcp_options = Some(to);
|
||||
info!(
|
||||
"Applying kernel tcp_keepalive parameters: idle {}, interval {}, count {}",
|
||||
idle,
|
||||
cfg.tcp_keepalive_interval.unwrap_or(60),
|
||||
cfg.tcp_keepalive_count.unwrap_or(5),
|
||||
);
|
||||
}
|
||||
|
||||
if let Some(bind_address_tls) = bind_address_tls {
|
||||
check_priv(bind_address_tls.as_str());
|
||||
let (tx, rx): (Sender<Vec<CertificateConfig>>, Receiver<Vec<CertificateConfig>>) = channel();
|
||||
@@ -88,7 +131,7 @@ pub fn run() {
|
||||
tls_settings.set_servername_callback(move |ssl_ref: &mut SslRef, ssl_alert: &mut SslAlert| certs_for_callback.load().server_name_callback(ssl_ref, ssl_alert));
|
||||
tls_settings.set_alpn_select_callback(grades::prefer_h2);
|
||||
|
||||
proxy.add_tls_with_settings(&bind_address_tls, None, tls_settings);
|
||||
proxy.add_tls_with_settings(&bind_address_tls, tcp_options.clone(), tls_settings);
|
||||
|
||||
let certs_for_watcher = certificates.clone();
|
||||
thread::spawn(move || {
|
||||
@@ -100,19 +143,37 @@ pub fn run() {
|
||||
}
|
||||
});
|
||||
}
|
||||
info!("Running HTTP listener on :{}", bind_address_http.as_str());
|
||||
proxy.add_tcp(bind_address_http.as_str());
|
||||
info!("Running HTTP listener on :{}", bind_address_http);
|
||||
if let Some(tc) = tcp_options {
|
||||
proxy.add_tcp_with_settings(&bind_address_http, tc);
|
||||
} else {
|
||||
proxy.add_tcp(&bind_address_http)
|
||||
}
|
||||
|
||||
server.add_service(proxy);
|
||||
server.add_service(bg_srvc);
|
||||
|
||||
thread::spawn(move || server.run_forever());
|
||||
|
||||
if let (Some(user), Some(group)) = (cfg.rungroup.clone(), cfg.runuser.clone()) {
|
||||
drop_priv(user, group, cfg.proxy_address_http.clone(), cfg.proxy_address_tls.clone());
|
||||
}
|
||||
let _ = sd_notify::notify(&[NotifyState::Ready]);
|
||||
|
||||
let (tx, rx) = channel();
|
||||
ctrlc::set_handler(move || tx.send(()).expect("Could not send signal on channel.")).expect("Error setting Ctrl-C handler");
|
||||
rx.recv().expect("Could not receive from channel.");
|
||||
info!("Signal received ! Exiting...");
|
||||
let pf = cfg.pid_file.clone().unwrap_or("/tmp/aralez.pid".to_string());
|
||||
if let Err(e) = write_pid_file(pf.as_str()) {
|
||||
panic!("Failed to write PID file: {} : {}", pf, e);
|
||||
}
|
||||
let mut signals = Signals::new(&[SIGINT, SIGTERM, SIGQUIT]).unwrap();
|
||||
for sig in signals.forever() {
|
||||
match sig {
|
||||
SIGINT => info!("SIGINT received! Exiting..."),
|
||||
SIGTERM => info!("SIGTERM received! Exiting..."),
|
||||
SIGQUIT => {
|
||||
thread::sleep(Duration::from_secs(300));
|
||||
info!("SIGQUIT received! Exiting...")
|
||||
}
|
||||
_ => unreachable!(),
|
||||
}
|
||||
break;
|
||||
}
|
||||
}
|
||||
|
||||
+63
-97
@@ -1,27 +1,27 @@
|
||||
// use std::net::SocketAddr;
|
||||
use crate::tls::acme::order::CHALLENGES;
|
||||
// use axum_server::tls_openssl::OpenSSLConfig;
|
||||
use crate::tls::acme::{account, order};
|
||||
use crate::utils::discovery::APIUpstreamProvider;
|
||||
use crate::utils::jwt::Claims;
|
||||
use crate::utils::metrics::{get_memory_usage, get_open_files, MEMORY_USAGE, OPEN_FILES};
|
||||
use crate::utils::structs::{Config, Configuration, UpstreamsDashMap};
|
||||
use crate::utils::tools::{upstreams_liveness_json, upstreams_to_json};
|
||||
use crate::web::acme::{acme_create, acme_order, http01_challenge};
|
||||
use axum::body::Body;
|
||||
use axum::extract::{Query, State};
|
||||
use axum::http::{Response, StatusCode};
|
||||
use axum::response::IntoResponse;
|
||||
use axum::routing::{any, get, post};
|
||||
use axum::{Json, Router};
|
||||
use futures::channel::mpsc::Sender;
|
||||
use futures::SinkExt;
|
||||
use jsonwebtoken::{encode, EncodingKey, Header};
|
||||
use log::{debug, error, info, warn};
|
||||
use prometheus::{gather, Encoder, TextEncoder};
|
||||
use serde::Serialize;
|
||||
use signal_hook::{consts::SIGQUIT, iterator::Signals};
|
||||
use std::collections::HashMap;
|
||||
use std::net::SocketAddr;
|
||||
use std::str::FromStr;
|
||||
use std::sync::Arc;
|
||||
use std::time::{Duration, SystemTime, UNIX_EPOCH};
|
||||
use tokio::net::TcpListener;
|
||||
use tokio::sync::mpsc;
|
||||
use tower_http::services::ServeDir;
|
||||
|
||||
#[derive(Serialize, Debug)]
|
||||
@@ -30,19 +30,19 @@ struct OutToken {
|
||||
}
|
||||
|
||||
#[derive(Clone)]
|
||||
struct AppState {
|
||||
pub(crate) struct AppState {
|
||||
master_key: Option<String>,
|
||||
cert_creds: String,
|
||||
certs_dir: String,
|
||||
pub(crate) cert_creds: String,
|
||||
pub(crate) certs_dir: String,
|
||||
upstreams_file: String,
|
||||
config_sender: Sender<Configuration>,
|
||||
config_sender: mpsc::Sender<Configuration>,
|
||||
config_api_enabled: bool,
|
||||
current_upstreams: Arc<UpstreamsDashMap>,
|
||||
full_upstreams: Arc<UpstreamsDashMap>,
|
||||
}
|
||||
|
||||
#[allow(unused_mut)]
|
||||
pub async fn run_server(config: &APIUpstreamProvider, mut to_return: Sender<Configuration>, upstreams_curr: Arc<UpstreamsDashMap>, upstreams_full: Arc<UpstreamsDashMap>) {
|
||||
pub async fn run_server(config: &APIUpstreamProvider, mut to_return: mpsc::Sender<Configuration>, upstreams_curr: Arc<UpstreamsDashMap>, upstreams_full: Arc<UpstreamsDashMap>) {
|
||||
let credsfile = config.config_dir.clone() + "/acme_credentials.json";
|
||||
let app_state = AppState {
|
||||
master_key: config.masterkey.clone(),
|
||||
@@ -56,11 +56,6 @@ pub async fn run_server(config: &APIUpstreamProvider, mut to_return: Sender<Conf
|
||||
};
|
||||
let app = Router::new()
|
||||
// .route("/{*wildcard}", get(senderror))
|
||||
// .route("/{*wildcard}", post(senderror))
|
||||
// .route("/{*wildcard}", put(senderror))
|
||||
// .route("/{*wildcard}", head(senderror))
|
||||
// .route("/{*wildcard}", delete(senderror))
|
||||
// .nest_service("/static", static_files)
|
||||
.route("/jwt", post(jwt_gen))
|
||||
.route("/acme_create", any(acme_create))
|
||||
.route("/acme_order/{*domain}", any(acme_order))
|
||||
@@ -70,28 +65,43 @@ pub async fn run_server(config: &APIUpstreamProvider, mut to_return: Sender<Conf
|
||||
.route("/status", get(status))
|
||||
.with_state(app_state);
|
||||
|
||||
// if let Some(value) = &config.tls_address {
|
||||
// let cf = OpenSSLConfig::from_pem_file(config.tls_certificate.clone().unwrap(), config.tls_key_file.clone().unwrap()).unwrap();
|
||||
// let addr: SocketAddr = value.parse().expect("Unable to parse socket address");
|
||||
// let tls_app = app.clone();
|
||||
// tokio::spawn(async move {
|
||||
// if let Err(e) = axum_server::bind_openssl(addr, cf).serve(tls_app.into_make_service()).await {
|
||||
// eprintln!("TLS server failed: {}", e);
|
||||
// }
|
||||
// });
|
||||
// info!("Starting the TLS API server on: {}", value);
|
||||
// }
|
||||
|
||||
let mut static_handle: Option<tokio::task::JoinHandle<()>> = None;
|
||||
if let (Some(address), Some(folder)) = (&config.file_server_address, &config.file_server_folder) {
|
||||
let static_listen = port_is_available("File Server", &address).await;
|
||||
let static_files = ServeDir::new(folder);
|
||||
let static_serve: Router = Router::new().fallback_service(static_files);
|
||||
let static_listen = TcpListener::bind(address).await.unwrap();
|
||||
drop(tokio::spawn(async move { axum::serve(static_listen, static_serve).await.unwrap() }));
|
||||
info!("Starting file server on: {}", address);
|
||||
|
||||
static_handle = Some(tokio::spawn(async move {
|
||||
match axum::serve(static_listen, static_serve).await {
|
||||
Ok(o) => info!("File server exited normally: {:?}", o),
|
||||
Err(e) => error!("File server exited: {}", e),
|
||||
}
|
||||
}))
|
||||
|
||||
// let a = config.file_server_address.to_owned();
|
||||
// let f = config.file_server_folder.to_owned();
|
||||
// drop(tokio::spawn(async move { run_file_server(a, f).await }));
|
||||
}
|
||||
|
||||
let listener = TcpListener::bind(config.address.clone()).await.unwrap();
|
||||
let listener = port_is_available("Config API", &config.address).await;
|
||||
info!("Starting the API server on: {}", config.address);
|
||||
axum::serve(listener, app).await.unwrap();
|
||||
let api_server = tokio::spawn(async move { axum::serve(listener, app).await.unwrap() });
|
||||
|
||||
let (tx, mut rx) = mpsc::channel(1);
|
||||
std::thread::spawn(move || {
|
||||
let mut signals = Signals::new(&[SIGQUIT]).unwrap();
|
||||
for sig in signals.forever() {
|
||||
tx.blocking_send(sig).unwrap();
|
||||
break;
|
||||
}
|
||||
});
|
||||
rx.recv().await;
|
||||
api_server.abort();
|
||||
if let Some(handle) = static_handle {
|
||||
handle.abort();
|
||||
}
|
||||
info!("Exiting...");
|
||||
}
|
||||
|
||||
async fn conf(State(st): State<AppState>, Query(params): Query<HashMap<String, String>>, content: String) -> impl IntoResponse {
|
||||
@@ -100,7 +110,7 @@ async fn conf(State(st): State<AppState>, Query(params): Query<HashMap<String, S
|
||||
}
|
||||
|
||||
let strcontent = content.as_str();
|
||||
let parsed = serde_yml::from_str::<Config>(strcontent);
|
||||
let parsed = noyalib::from_str::<Config>(strcontent);
|
||||
match parsed {
|
||||
Ok(_) => {
|
||||
if let Some(_) = params.get("save") {
|
||||
@@ -117,7 +127,7 @@ async fn conf(State(st): State<AppState>, Query(params): Query<HashMap<String, S
|
||||
}
|
||||
}
|
||||
|
||||
async fn apply_config(content: &str, mut st: AppState, save: bool) {
|
||||
async fn apply_config(content: &str, st: AppState, save: bool) {
|
||||
let sl = crate::utils::parceyaml::load_configuration(content, "content").await;
|
||||
if let Some(serverlist) = sl.0 {
|
||||
if save {
|
||||
@@ -171,6 +181,9 @@ async fn jwt_gen(State(state): State<AppState>, Json(payload): Json<Claims>) ->
|
||||
}
|
||||
|
||||
async fn metrics() -> impl IntoResponse {
|
||||
MEMORY_USAGE.set(get_memory_usage() as i64);
|
||||
OPEN_FILES.set(get_open_files() as i64);
|
||||
|
||||
let metric_families = gather();
|
||||
let encoder = TextEncoder::new();
|
||||
let mut buffer = Vec::new();
|
||||
@@ -222,72 +235,25 @@ async fn status(State(st): State<AppState>, Query(params): Query<HashMap<String,
|
||||
.unwrap()
|
||||
}
|
||||
|
||||
#[allow(clippy::needless_return)]
|
||||
async fn acme_create(State(state): State<AppState>) -> impl IntoResponse {
|
||||
match account::load_or_create(state.cert_creds.as_str()).await {
|
||||
Ok(txt) => {
|
||||
return Response::builder()
|
||||
.status(StatusCode::OK)
|
||||
.header("Content-Type", "text/plain")
|
||||
.body(Body::from(txt))
|
||||
.unwrap()
|
||||
}
|
||||
Err(e) => {
|
||||
return Response::builder()
|
||||
.status(StatusCode::INTERNAL_SERVER_ERROR)
|
||||
.body(Body::from(format!("Failed to create account: {}", e)))
|
||||
.unwrap()
|
||||
}
|
||||
};
|
||||
}
|
||||
#[allow(clippy::needless_return)]
|
||||
async fn acme_order(State(state): State<AppState>, axum::extract::Path(domain): axum::extract::Path<String>) -> impl IntoResponse {
|
||||
let domain_clean = domain.trim_matches('/');
|
||||
match order::order(domain_clean, state.cert_creds.as_str(), state.certs_dir).await {
|
||||
Ok(txt) => {
|
||||
return Response::builder()
|
||||
.status(StatusCode::OK)
|
||||
.header("Content-Type", "text/plain")
|
||||
.body(Body::from(txt))
|
||||
.unwrap()
|
||||
}
|
||||
Err(e) => {
|
||||
return Response::builder()
|
||||
.status(StatusCode::INTERNAL_SERVER_ERROR)
|
||||
.body(Body::from(format!("Failed to order a certificate: {}", e)))
|
||||
.unwrap()
|
||||
}
|
||||
};
|
||||
}
|
||||
pub async fn port_is_available(name: &str, address: &str) -> TcpListener {
|
||||
let addr = SocketAddr::from_str(address).unwrap_or_else(|e| panic!("{}: Invalid address format: {:?}", name, e));
|
||||
let t = Duration::from_secs(2);
|
||||
|
||||
pub async fn http01_challenge(axum::extract::Path(token): axum::extract::Path<String>) -> impl IntoResponse {
|
||||
if let Ok(challenges) = CHALLENGES.read() {
|
||||
// for k in challenges.iter() {
|
||||
// println!(" ==> {} : {}", k.0, k.1);
|
||||
// }
|
||||
|
||||
if let Some(key_authorization) = challenges.get(&token) {
|
||||
return Response::builder()
|
||||
.status(StatusCode::OK)
|
||||
.header("Content-Type", "text/plain")
|
||||
.body(Body::from(key_authorization.clone()))
|
||||
.unwrap();
|
||||
//if addr.ip() == IpAddr::V4(Ipv4Addr::UNSPECIFIED) {
|
||||
// addr.set_ip(IpAddr::V4(Ipv4Addr::LOCALHOST));
|
||||
//}
|
||||
let p = addr.port();
|
||||
loop {
|
||||
match TcpListener::bind(addr).await {
|
||||
Ok(listener) => {
|
||||
return listener;
|
||||
}
|
||||
Err(_) => {
|
||||
warn!("{} port is not available: {} will try again in {:?}", name, p, t);
|
||||
tokio::time::sleep(t).await;
|
||||
}
|
||||
}
|
||||
}
|
||||
Response::builder()
|
||||
.status(StatusCode::NOT_FOUND)
|
||||
.header("Content-Type", "text/plain")
|
||||
.body(Body::from("Not found"))
|
||||
.unwrap()
|
||||
}
|
||||
|
||||
// fn key_authorization(headers: &HeaderMap, params: &HashMap<String, String>, masterkey: &str) -> bool {
|
||||
// if let Some(s) = headers.get("x-api-key").and_then(|v| v.to_str().ok()).or(params.get("key").map(|s| s.as_str())) {
|
||||
// if s.as_bytes().ct_eq(masterkey.as_bytes()).into() {
|
||||
// return true;
|
||||
// }
|
||||
// }
|
||||
// false
|
||||
// }
|
||||
|
||||
// -- ⚝ by Dave -- in NeoVim ⚝ --
|
||||
|
||||
Reference in New Issue
Block a user